
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Researcher found an Information Disclosure in the Brave browser

Security researcher discovered an Information Disclosure vulnerability in Brave browser and reported it through the HackerOne platform. Security researcher Kirtikumar Anandrao Ramchandani discovered an Information Disclosure vulnerability in the Brave Browser and reported it to the company through the HackerOne platform. The researcher discovered that when the browser is used with Tor it could leak […]

brave browser bug

Security researcher discovered an Information Disclosure vulnerability in Brave browser and reported it through the HackerOne platform.

Security researcher Kirtikumar Anandrao Ramchandani discovered an Information Disclosure vulnerability in the Brave Browser and reported it to the company through the HackerOne platform.

The researcher discovered that when the browser is used with Tor it could leak the referer.

“Brave browser has a function of New Private Window with Tor. The browser when used with Tor shouldn’t leak the referer.” reads the report submitted to HackerOne.

Below is the procedure to reproduce the issue:

  1. Visit exploit.
  2. Click on https://www.whatismybrowser.com/.

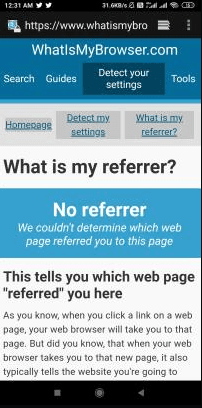
Expected behavior: It should have shown a blank referrer;

Actual behavior: It shows the referrer as: kirtikumarar.com which was the host from where we navigated.

The following screenshot shows the expected behavior:

brave browser bug

The expert also published a video POC on the report page showing the expected behavior.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Brave)

[adrotate banner=”5″]

[adrotate banner=”13″]


