
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CVE-2019-9019 affects British Airways Entertainment System on Boeing 777-36N(ER)

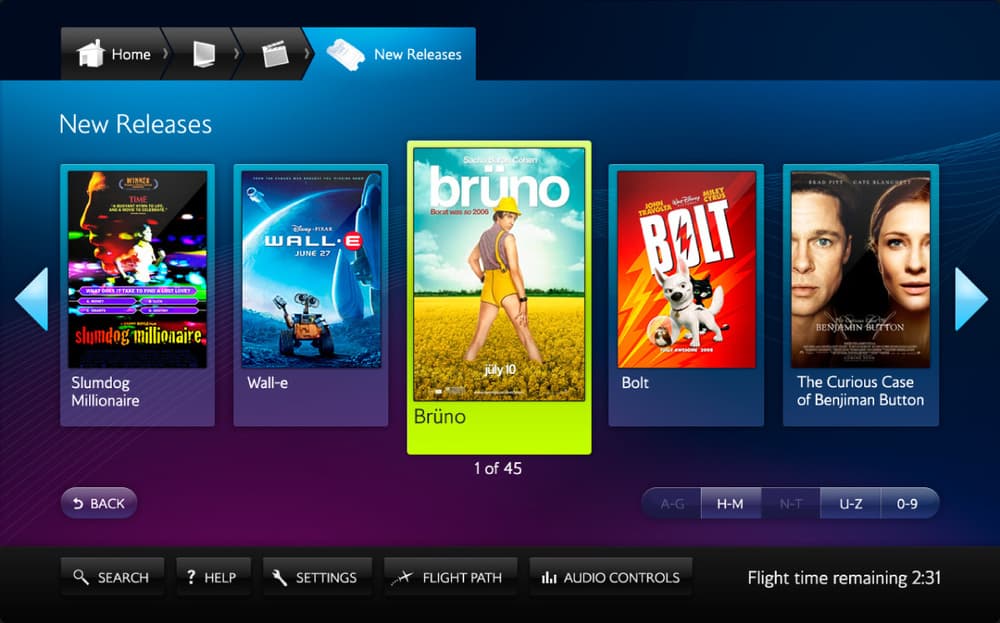
The British Airways Entertainment System, as installed on Boeing 777-36N(ER) and possibly other aircraft, is affected by a privilege escalation issue tracked as CVE-2019-9019. Experts discovered a critical vulnerability in the British Airways Entertainment System. The flaw is a privilege escalation issue that resides in the component USB Handler, an attacker could exploit it using […]

British Airways Entertainment System

The British Airways Entertainment System, as installed on Boeing 777-36N(ER) and possibly other aircraft, is affected by
a privilege escalation issue tracked as CVE-2019-9019.

Experts discovered a critical vulnerability in the British Airways Entertainment System. The flaw is a privilege escalation issue that resides in the component USB Handler, an attacker could exploit it using an unknown input to escalate privileges.

The affected British Airways Entertainment System is installed on Boeing 777-36N(ER) and possibly other aircraft, it does not prevent the USB charging/data-transfer feature from interacting with USB keyboard and mouse devices.

“The British Airways Entertainment System, as installed on Boeing 777-36N(ER) and possibly other aircraft, does not prevent the USB charging/data-transfer feature from interacting with USB keyboard and mouse devices, which allows physically proximate attackers to conduct unanticipated attacks against Entertainment applications, as demonstrated by using mouse copy-and-paste actions to trigger a Chat buffer overflow or possibly have unspecified other impact. ” reads the description for the vulnerability published by Mitre.

British Airways Entertainment System

The flaw was reported on 02/22/2019, it was tracked as CVE-2019-9019, a local unauthenticated attacker could potentially exploit it.

At the time of writing, there are neither technical details nor an exploit publicly available.

Entertainment systems are crucial components in aviation, they could represent entry points for hackers. In December 2016, Ruben Santamarta, a security researcher from IOActive, discovered several vulnerabilities in Panasonic Avionics in-flight entertainment, aka IFE systems.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – British Airways Entertainment System , hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


