
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CaddyWiper, a new data wiper hits Ukraine

Experts discovered a new wiper, tracked as CaddyWiper, that was employed in attacks targeting Ukrainian organizations. Experts at ESET Research Labs discovered a new data wiper, dubbed CaddyWiper, that was employed in attacks targeting Ukrainian organizations. The security firm has announced the discovery of the malware with a series of tweets: “This new malware erases […]

CaddyWiper

Experts discovered a new wiper, tracked as CaddyWiper, that was employed in attacks targeting Ukrainian organizations.

Experts at ESET Research Labs discovered a new data wiper, dubbed CaddyWiper, that was employed in attacks targeting Ukrainian organizations.

The security firm has announced the discovery of the malware with a series of tweets:

“This new malware erases user data and partition information from attached drives,” ESET Research Labs reported. “ESET telemetry shows that it was seen on a few dozen systems in a limited number of organizations.”

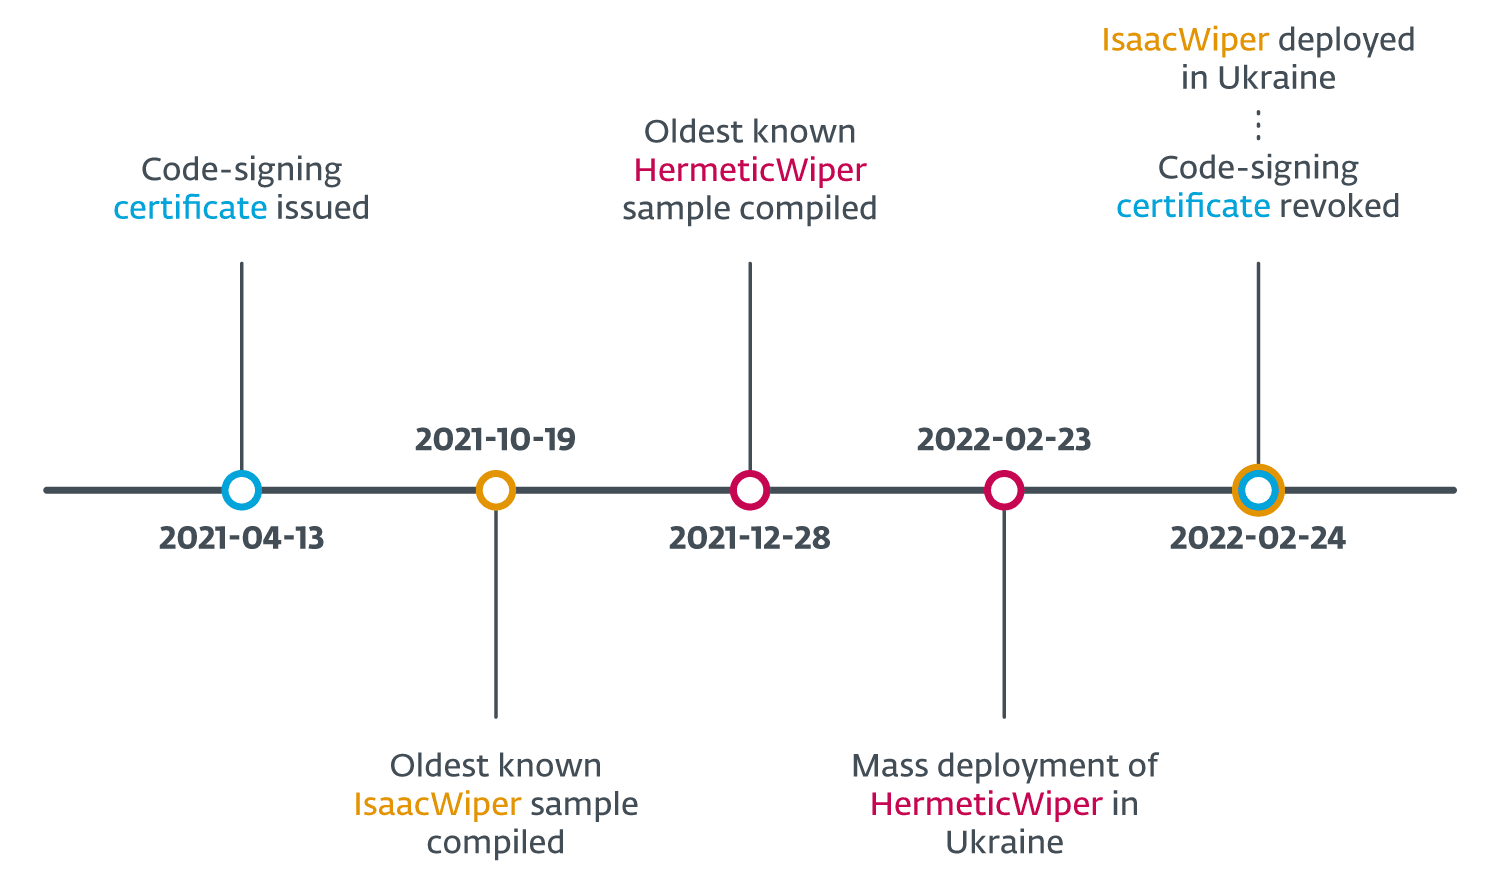
CaddyWiper is the third wiper observed by ESET in attacks against Ukraine after HermeticWiper and IsaacWiper, experts pointed out that it does not share any significant code similarity with them.

Similar to HermeticWiper deployments, CaddyWiper being deployed via GPO, a circumstance that suggests the attackers had initially compromised the target’s Active Directory server.

In order to maintain access to the target organization while still disturbing operations, the CaddyWiper avoids destroying data on domain controllers. CaddyWiper uses the DsRoleGetPrimaryDomainInformation() function to determine if a device is a domain controller.

The CaddyWiper sample analyzed by ESET was not digitally signed, the malware was compiled.

Microsoft researchers also observed another wiper that was employed in attacks against Ukraine, it was tracked as WhisperGate.

In Mid-February, the Security Service of Ukraine (SSU) today revealed the country was the target of an ongoing “wave of hybrid warfare” conducted by Russia-linked malicious actors. Threat actors aim at destabilizing the social contest in the country and instilling fear and untrust in the country’s government. Data wiper usage was part of this hybrid warfare strategy.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, CaddyWiper)

[adrotate banner=”5″]

[adrotate banner=”13″]


