
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CashCrate Cash-for-Surveys Site breached, 6 Million accounts stolen

According to the data breach notification site LeakBase hackers have stolen 6 million accounts for the CashCrate Cash-for-Surveys Site. Another day another data breach, this time hackers have stolen 6 million accounts for CashCrate, a site where users can be paid to complete online surveys. The news was reported by Motherboard who obtained the database and confirmed that records […]

CashCrate Cash-for-Surveys Site breached

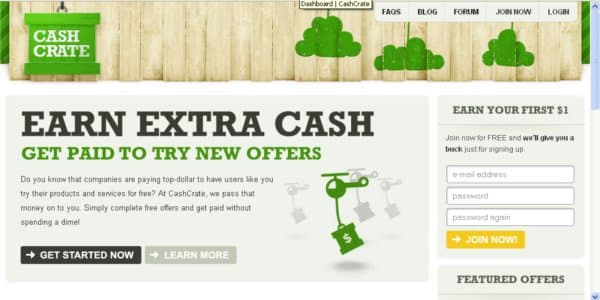
According to the data breach notification site LeakBase hackers have stolen 6 million accounts for the CashCrate Cash-for-Surveys Site.

Another day another data breach, this time hackers have stolen 6 million accounts for CashCrate, a site where users can be paid to complete online surveys. The news was reported by Motherboard who obtained the database and confirmed that records include user email addresses, passwords, names, and physical addresses.

The data breach notification site LeakBase provided Motherboard with a copy of the CashCrate archive.

CashCrate allows companies to pay users that test their products and services, or that participate in daily surveys.

The analysis of the database revealed that the earliest accounts date back to 2006, and the bad news is that accounts registered from 2010 have MD5 hashed passwords.

“Accounts from mid 2010 onwards appear to have passwords hashed with the notoriously weak MD5 algorithm, meaning that hackers may be able to crack the hashes and obtain the real login credentials.” states Motherboard.

CashCrate Cash-for-Surveys Site breached

Motherboard has verified that the accounts are legitimate, it also noticed it its post that CashCrate does not use basic web encryption on its website.

The company is notifying all its users about the security breach.

“We’re in the process of notifying all our members about the breach. While we’re still investigating the cause, at this point it appears that our third-party forum software was compromised, which led to the breach. We’ve deactivated it until we’re confident it’s secure,” a CashCrate spokesperson told Motherboard in an email.

“We have also confirmed that any users who have logged in since October 2013 have passwords that are fully hashed and salted, and we’re looking into why some inactive accounts have plaintext passwords. Those will be hashed and salted immediately,” the spokesperson added.

If you are a CashCrate user change your password now and in case you shared same login credentials on other websites you must change the passwords also for them.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – CashCrate, hacking)

[adrotate banner=”13″]


