
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Ukraine CERT-UA warns of phishing attacks employing Remcos software

The Computer Emergency Response Team of Ukraine (CERT-UA) warns of a new wave of attacks against state authorities to deploy the Remcos software. The Computer Emergency Response Team of Ukraine (CERT-UA) is warning of a phishing campaign aimed at state authorities that involves the use of the legitimate remote access software Remcos. The phishing emails, […]

Remcos CERT-UA

The Computer Emergency Response Team of Ukraine (CERT-UA) warns of a new wave of attacks against state authorities to deploy the Remcos software.

The Computer Emergency Response Team of Ukraine (CERT-UA) is warning of a phishing campaign aimed at state authorities that involves the use of the legitimate remote access software Remcos.

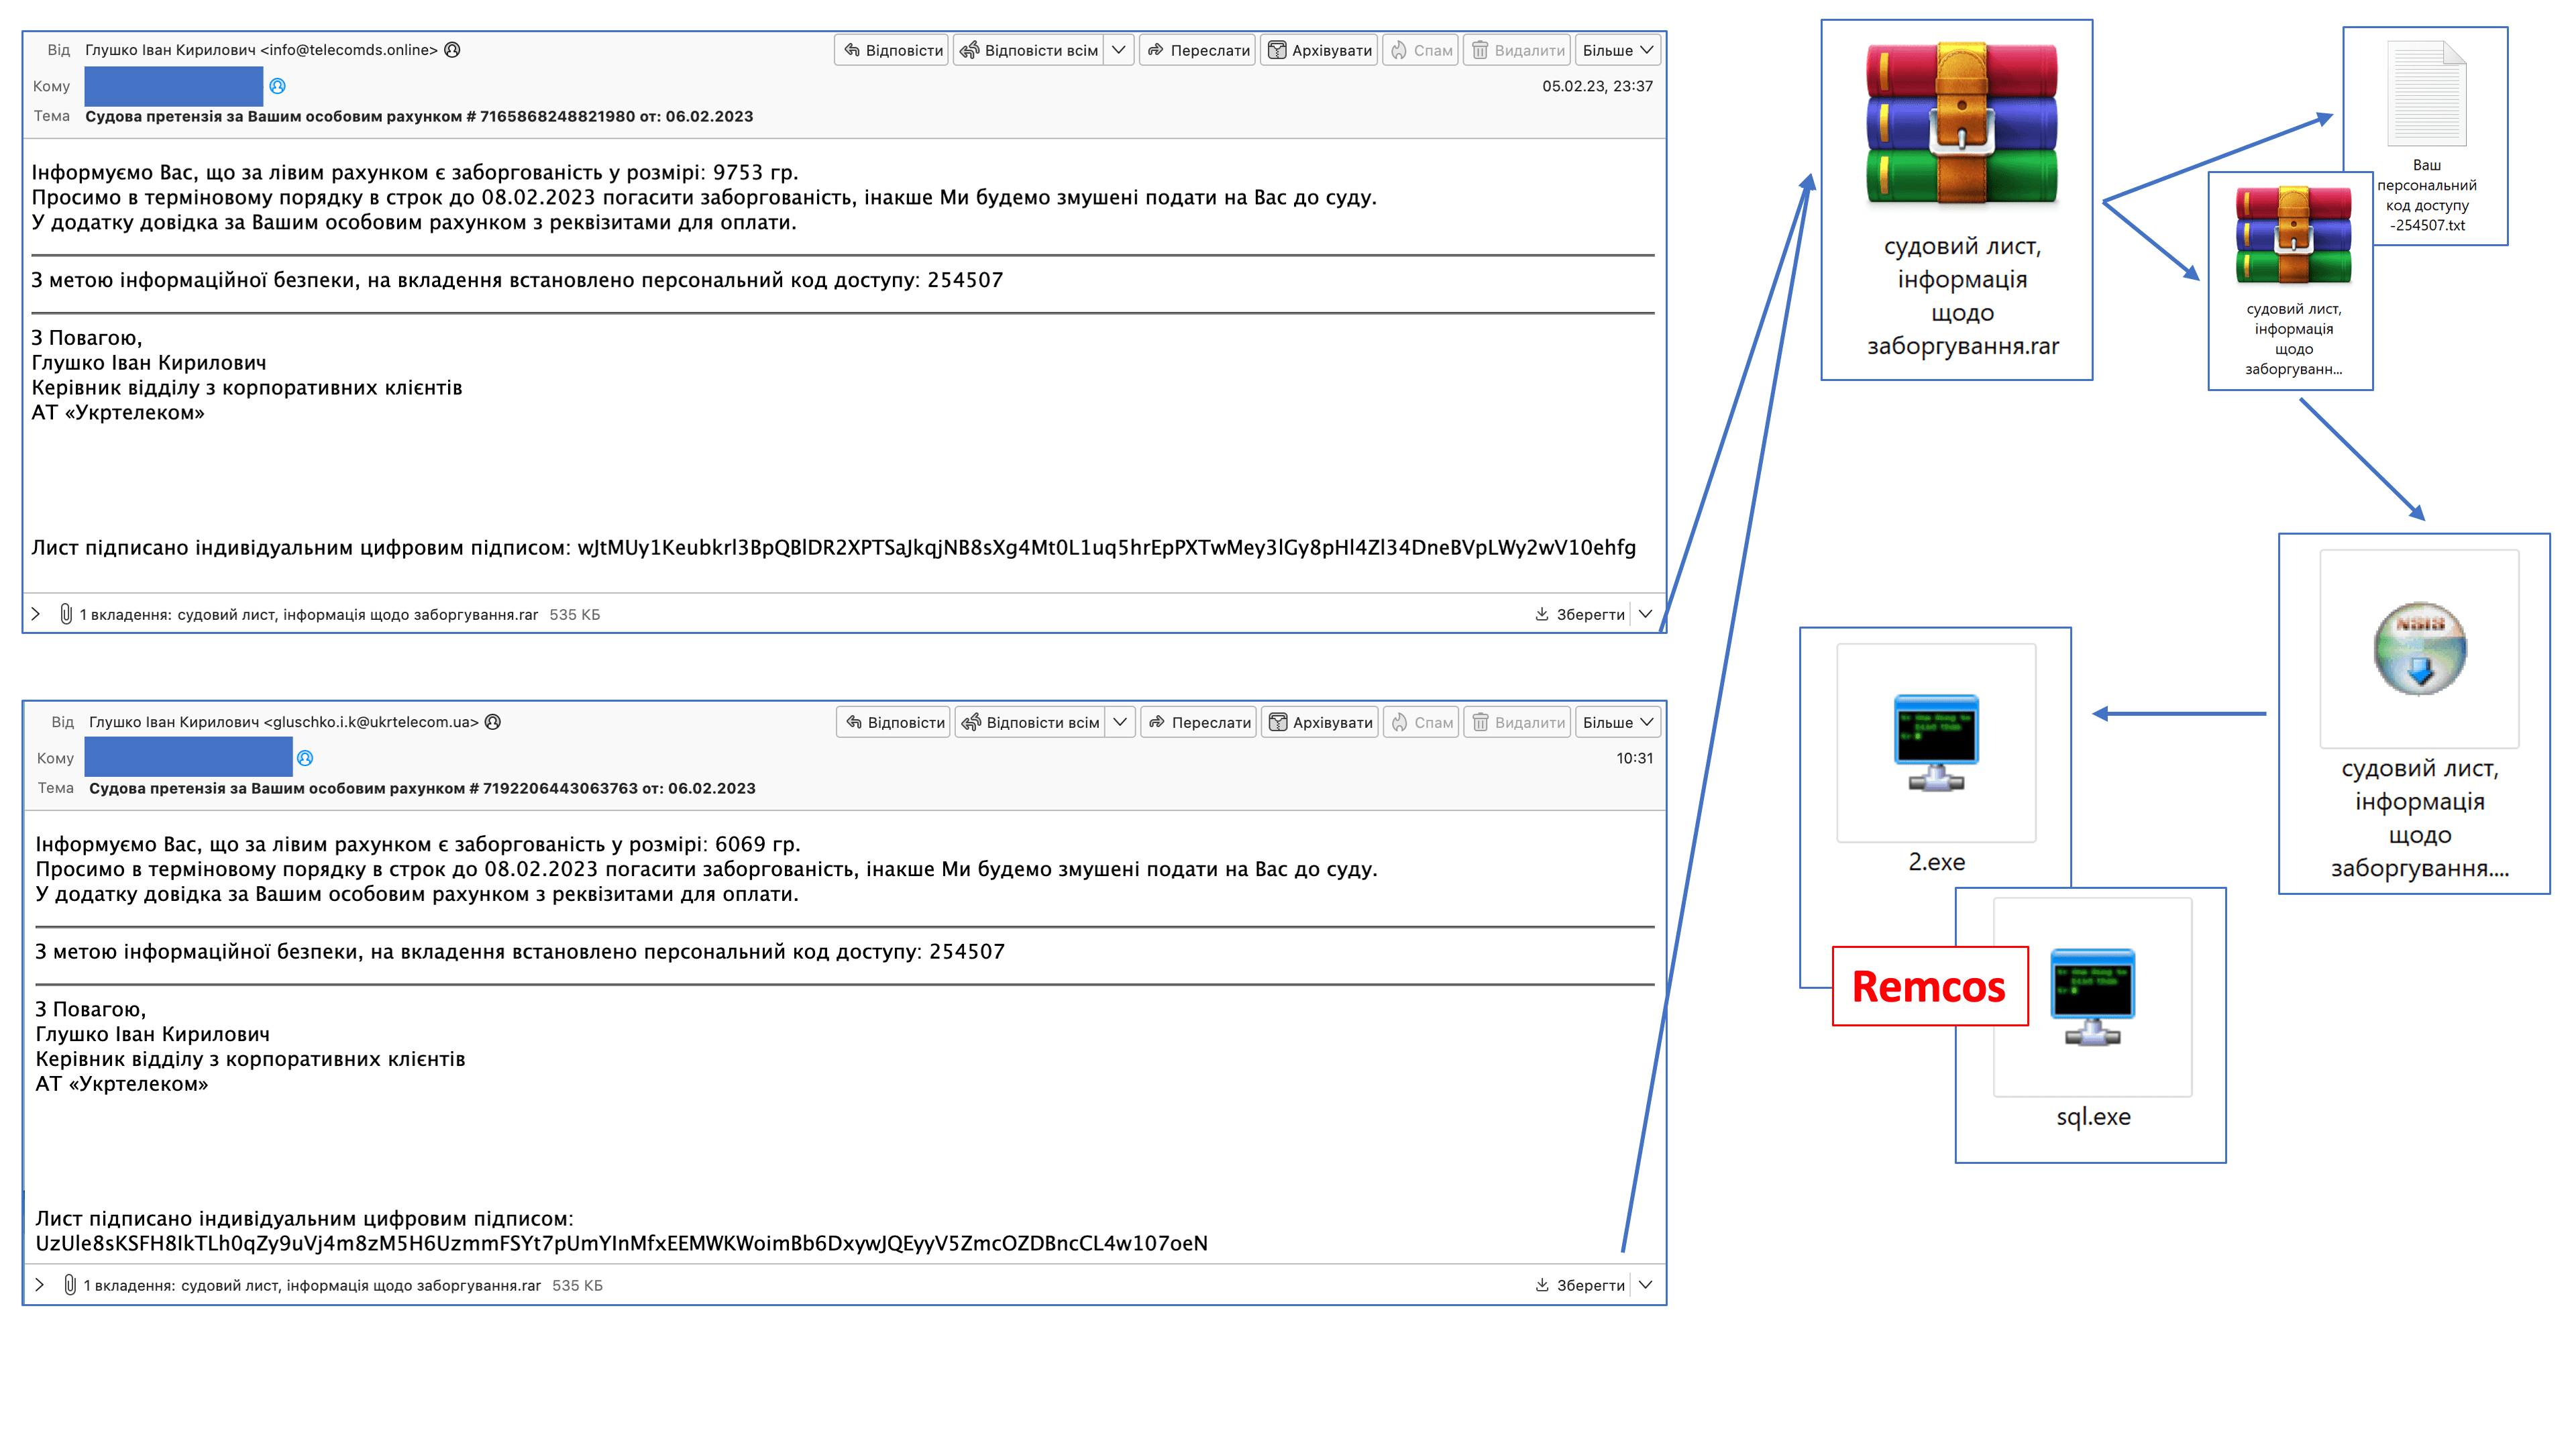
The phishing emails, allegedly from JSC “Ukrtelecom”, have the subject “Court claim against your personal account # 7192206443063763 dated: 06.02.2023” and come with .RAR attachment named “court letter, information on debt.rar”.

The RAR archive contains a text document named “Your personal access code -254507.txt” and another password-protected RAR-archive named “court letter, information on debt. pdf.rar.” The latter archive contains an executable named “court letter, information on debt.pdf.exe.” Upon executing the executable, an the Remcos remote monitoring and surveillance program is installed on the victim’s machine.

The alert pointed out that this executable is more than 600MB in size.

Remcos is a legitimate remote monitoring and surveillance software developed by the company “BreakingSecurity.”

The CERT-UA attributed the campaign to a nation-state actor tracked as UAC-0050.

“Detected activity has been tracked under UAC-0050 since at least 2020. Previous cyberattacks by the mentioned group were carried out using the program for remote administration RemoteUtilities.” reads the alert issued by the Ukrainian CERT. “Based on the fact that the objects of cyberattacks are usually (but not exclusively) the state authorities of Ukraine, and also, taking into account the functionality of the programs used, we believe that the activity is carried out for the purpose of espionage.”

The alert published by the CERT-UA also included Indicators of Compromise (IoCs).

Recently, the State Cyber Protection Centre (SCPC) of Ukraine also warned of targeted attacks conducted by the Russia-linked APT group Gamaredon (aka Shuckworm, Actinium, Armageddon, Primitive Bear, UAC-0010, and Trident Ursa) against public authorities and critical information infrastructure in Ukraine.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Remcos)


