
CERT-UA warned that Russia-linked actor is impersonating the Security Service of Ukraine (SSU) in a new phishing campaign to distribute malware.
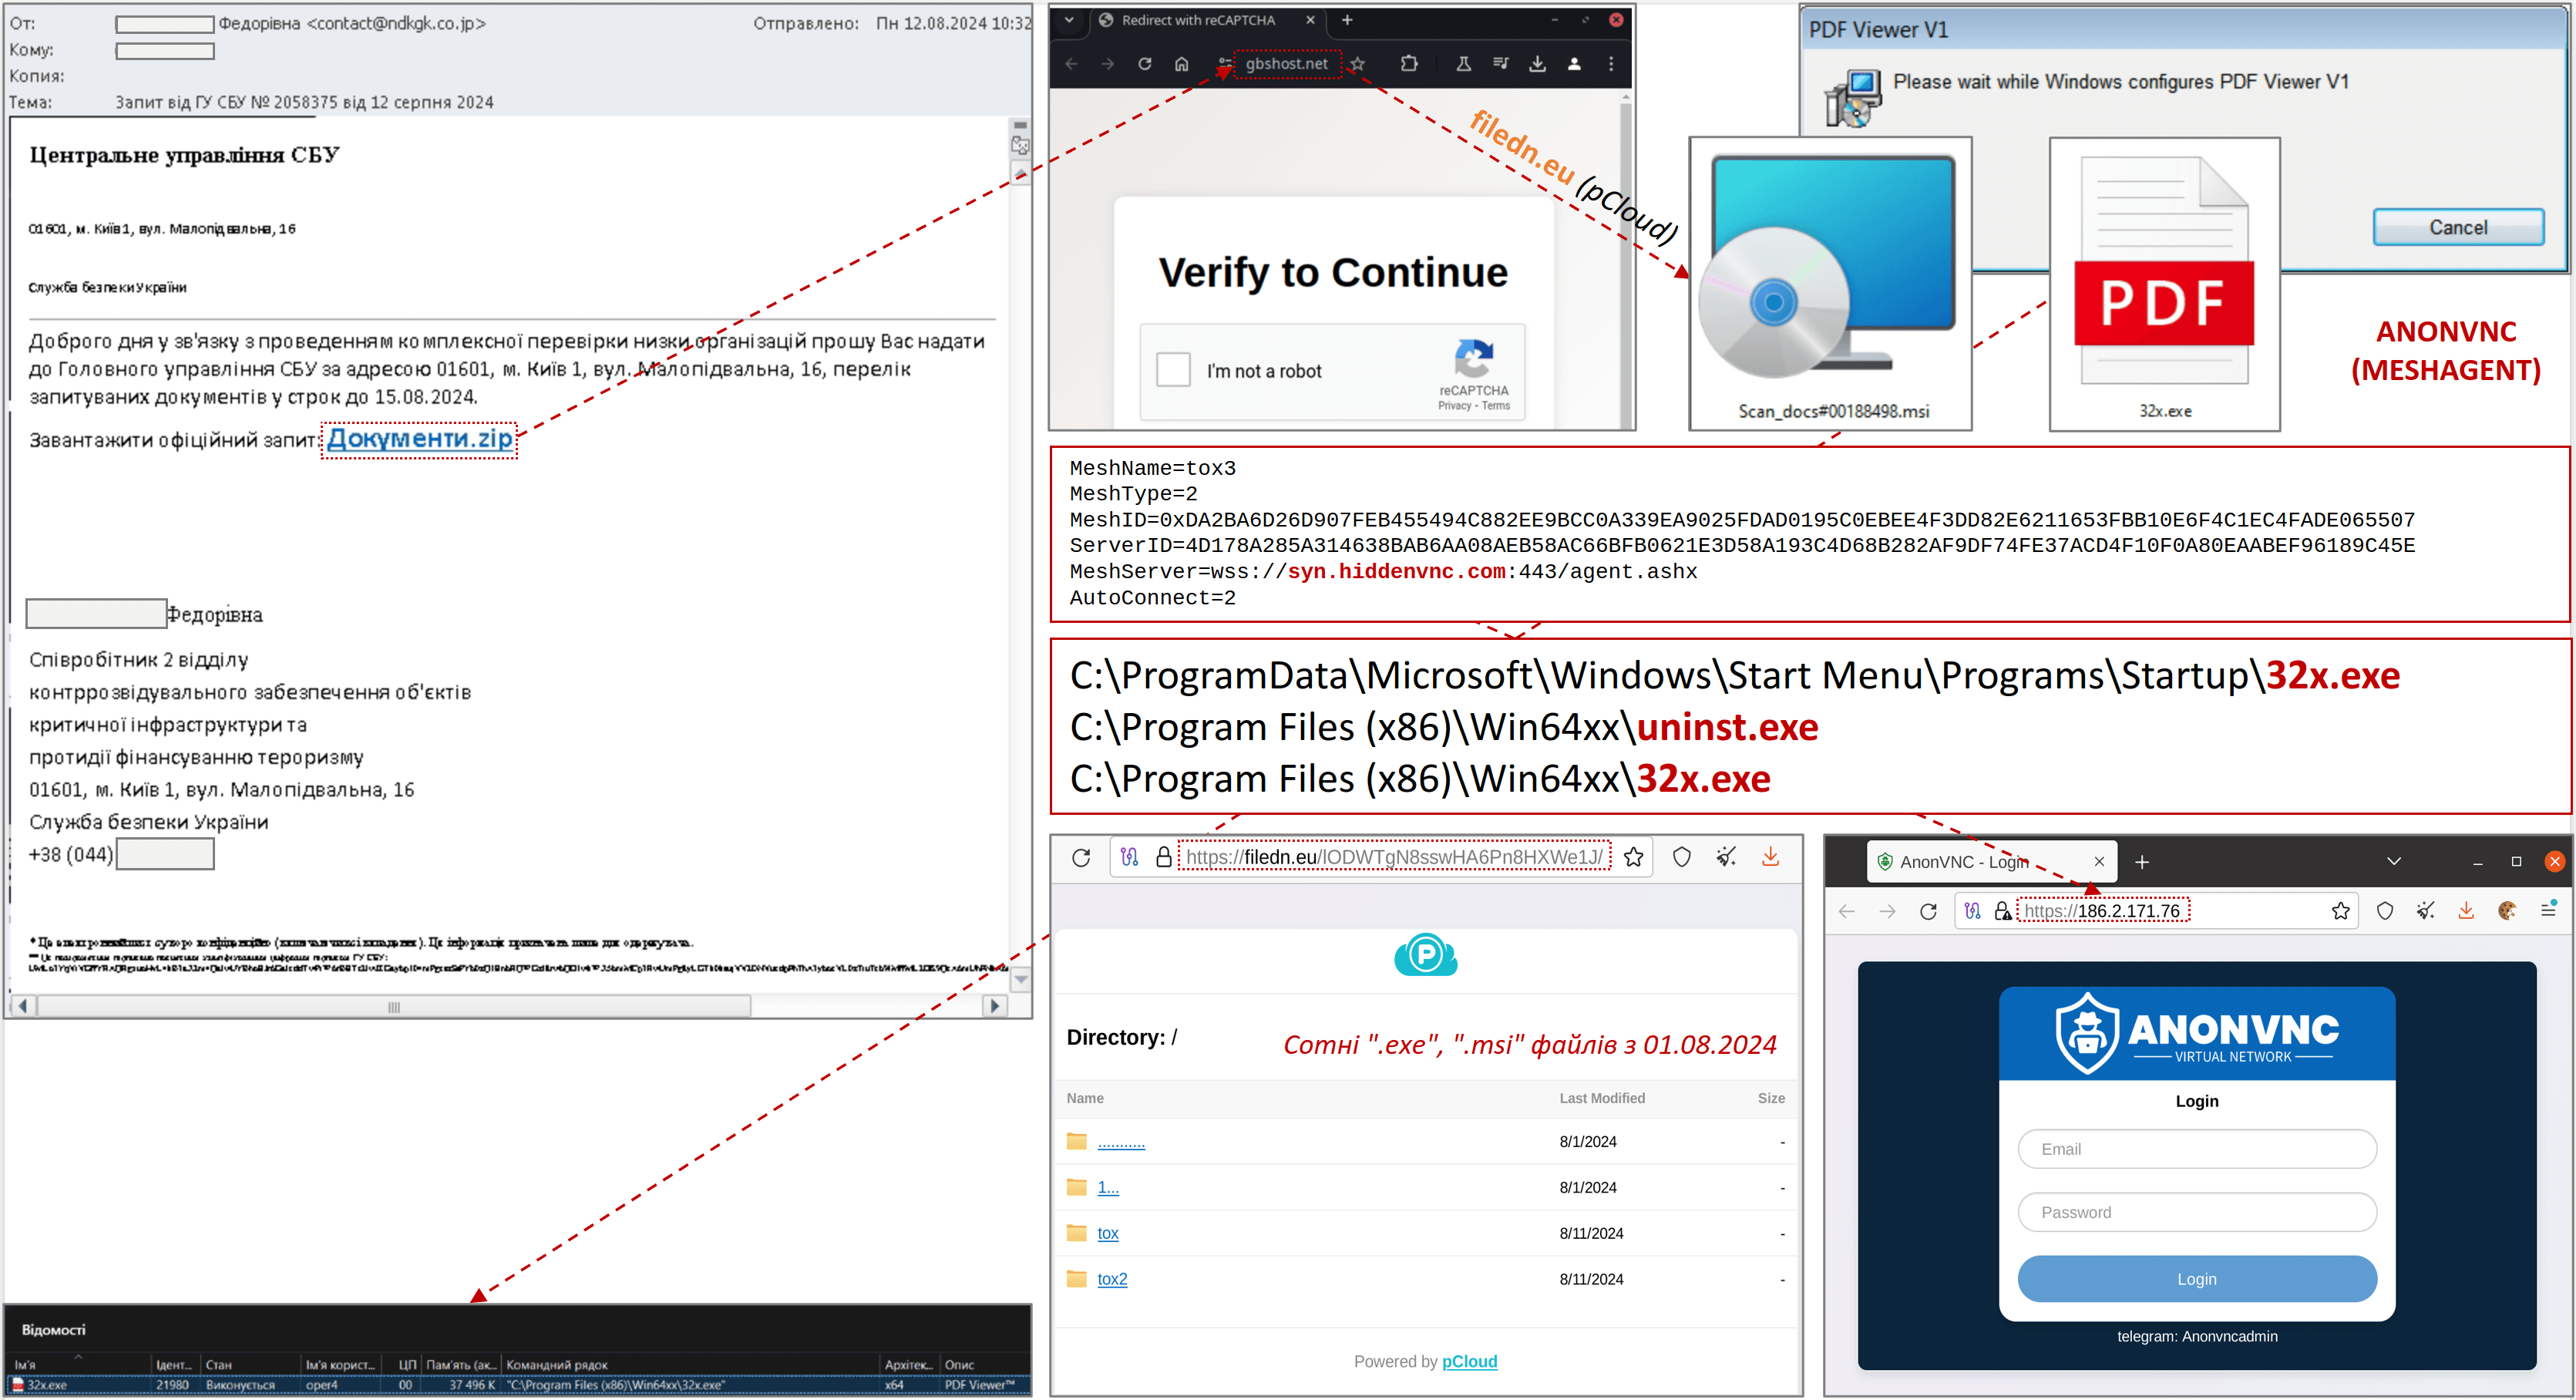
The Computer Emergency Response Team of Ukraine (CERT-UA) has warned of a new phishing campaign targeting organizations in the country, including government entities. The campaign, tracked as UAC-0198, has been active since July. Threat actors sent out emails attempting to impersonate Security Service of Ukraine (SSU) and contains a link to download a file named “Documents.zip.”
Upon clicking the link, an MSI file is downloaded. If the recipient then opens this file, the ANONVNC malware, tracked as MESHAGENT, is executed. ANONVNC borrows the code of the open-source remote management tool MeshAgent, it allows attackers to remotely control the infected hosts.
“On August 12, 2024, Ukraine’s Computer Emergency Response Team (CERT-UA) detected a widespread phishing campaign involving emails purportedly from the Security Service of Ukraine. These emails contain a link to download a file named “Documents.zip.”” states the CERT-UA. “In reality, clicking the link downloads an MSI file (e.g., “Scan_docs#40562153.msi”), which, when opened, triggers the ANONVNC (MESHAGENT) malware. This malware enables hidden, unauthorized access to computers.”
As of 12:00 PM on August 12, 2024, CERT-UA identified over 100 computers were infected with the malware, including those within Ukrainian government and local government agencies.

“Note that related cyberattacks have been occurring since at least July 2024 and may have a broader geographic scope. For instance, more than a thousand EXE and MSI files have been found in the pCloud file service directories since August 1, 2024 (additional indicators related to the August 12, 2024 campaign are included in the article).” concludes the CERT-UA.
In May, CERT-UA warned of a surge in in cyberattacks linked to the financially-motivated threat actor UAC-0006. UAC-0006 has been active since at least 2013. The threat actors focus on compromising accountants’ PCs (which are used to support financial activities, such as access to remote banking systems), stealing credentials, and making unauthorized fund transfers.
The government experts reported that the group carried out at least two massive campaigns since May 20, threat actors aimed at distributing SmokeLoader malware via email.
SmokeLoader acts as a loader for other malware, once it is executed it will inject malicious code into the currently running explorer process (explorer.exe) and downloads another payload to the system.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Security Service of Ukraine)


