
Iranian APT groups continue to very active, recently Charming Kitten cyber spies attempted to pose as an Israeli cyber-security firm that uncovered previous hacking campaigns.
The Iranian Charming Kitten ATP group, aka Newscaster or Newsbeef, launched spear phishing attacks against people interested in reading reports about it.
The Newscaster group made the headlines in 2014 when experts at iSight issued a report describing the most elaborate net-based spying campaign organized by Iranian hackers using social media.
Iranian Hackers used a network of fake accounts (NEWSCASTER network) on principal social media to spy on US officials and political staff worldwide, this is reported in an analysis done by iSIGHTPartners. The Charming Kitten group is also known for the abuse of Open Source Security Tools, including the BeEF.
The threat actor targeted numerous entities in Iran, the U.S., Israel, the U.K. and other countries. The hackers also hit individuals involved in academic research, human rights, and the media.
ClearSky detailed the group’s activities during 2016-2017, the report includes information related to the infrastructure used by the APT and to a new strain of malware dubbed DownPaper.
The report also linked the hacker behind the HBO security breach to the Charming Kitten, and reveals the identities of two other alleged members of the group.
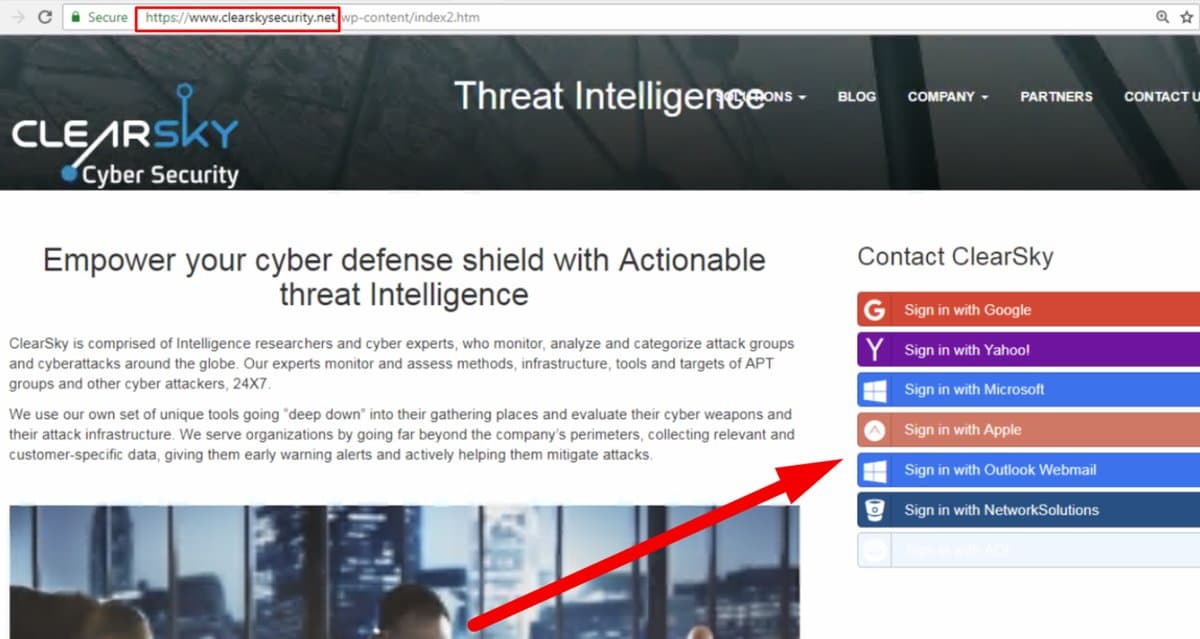
Recently the experts from the Israeli cyber-security firm ClearSky Security, discovered that Charming Kitten APT creates a rogue copy (clearskysecurity.net ) of the official website of the company (clearskysec.com).

“Charming Kitten built a phishing website impersonating our company,” stats ClearkSky. “They copied pages from our public website and changed one of them to include a ‘sign in’ option with multiple services.”
“These sign-in options are all phishing pages that would send the victim’s credentials to the attackers,” ClearSky said. “Our legitimate website does not have any sign in option.”
#CharmingKitten built a phishing website impersonating our company. The fake website is clearskysecurity.net (the real website is https://t.co/kdF5RfVA83). They copied pages from our public website and changed one of them to include a "sign in" option with multiple services. pic.twitter.com/3fETo2GTuJ
— ClearSky Cyber Security (@ClearskySec) July 1, 2018
The experts believe they have discovered the rogue website while the Iranian APT was still working on it.
“It seems that the impersonating website is still being built because some of the pages have error messages in them,” ClearSky added.
The experts discovered that the fake clearskysecurity.net domain was hosted on a server that was associated with the Charming Kitten APT by ClearSky last month.
Potentially #CharmingKitten put BeEF in The Jewish Journal, and set up fake domains of Deutsche Welle (Germany's public international broadcaster) and Frost&Sullivan:
jewishjournal.us
deutcshewelle.org
deutcshewelle.com
frostsullivan.orgMore:https://t.co/1mco1Vw531 pic.twitter.com/Q5HCDtmPOo
— ClearSky Cyber Security (@ClearskySec) June 12, 2018
The server was still hosting content from previous campaigns, a further clue that link it to the Iranian hacker group.
The website appears still under development, it is likely it was not yet involved in any hacking campaign.
As the website was not finished, ClearSky doesn’t believe the Iranian hackers managed to phish anyone yet. The website was taken down after a few hours of its discovery.
Iranian hackers are becoming even more aggressive even if experts believe that they are not particularly sophisticated.
Recently we discussed the OilRig gang has been using a new Trojan in attacks aimed at targets in the Middle East.
OilRig is just one of the Iran-linked hacker crews, other groups tracked by security experts are APT33, Rocket Kitten, Cobalt Gypsy (Magic Hound), Charming Kitten (aka Newscaster and NewsBeef) and CopyKittens.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Charming Kitten, APT)
[adrotate banner=”5″]
[adrotate banner=”13″]


