Check Point fixed CVE-2026-91843, a critical flaw that could let attackers run code as root on Security Management and Log Servers with no login needed.
Check Point addressed CVE-2026-91843 (CVSS score of 9.8), a critical vulnerability in its Security Management and Log Servers. The flaw could let an attacker with no account run code as root over the network.
The flaw sits in the login process before authentication. Censys researchers found that an attacker can trigger the stack overflow by sending a login request with an extremely long username.
“This vulnerability may allow an unauthenticated attacker to remotely execute arbitrary code with root privileges through the login process.” reads the advisory. “At this time, there is no indication that this vulnerability has been exploited in the wild. However, due to its critical severity and potential impact, we strongly recommend taking immediate action to protect your environment.”
Check Point said the attack path works only when customers use the Trusted Clients setting, which controls access to the management server through SmartConsole.
Affected versions includes:
- R82.20
- R82.10 Jumbo Hotfix Take 44 or lower
- R82 Jumbo Hotfix Take 126 or lower
- R81.20 Jumbo Hotfix Take 166 or lower
- R81.10 Jumbo Hotfix Take 190 or lower (EoS)
- R80, R80.10, R80.20, R80.30, R80.40, R81 (all EoS)
Check Point released the fix through its LivePatch channel. Customers with automatic updates enabled should already have protection, while others need to apply the update described in advisory sk1000155. The company urged customers to act.
So far, Check Point is not aware of real-world exploitation of the flaw. Censys reported no public proof-of-concept exploit as of September 16.
Organizations should check their update status and apply the fix if required. These servers manage firewall and admin access, so teams should patch them quickly.
Organizations should apply the LivePatch fix described in sk1000155. Customers who have automatic updates enabled should already have the fix.
As an additional security measure, organizations should follow the recommendations in the Check Point Management and Gateway hardening best practices guide. They should also limit Trusted Clients access on the management server to specific, known internal IP addresses.
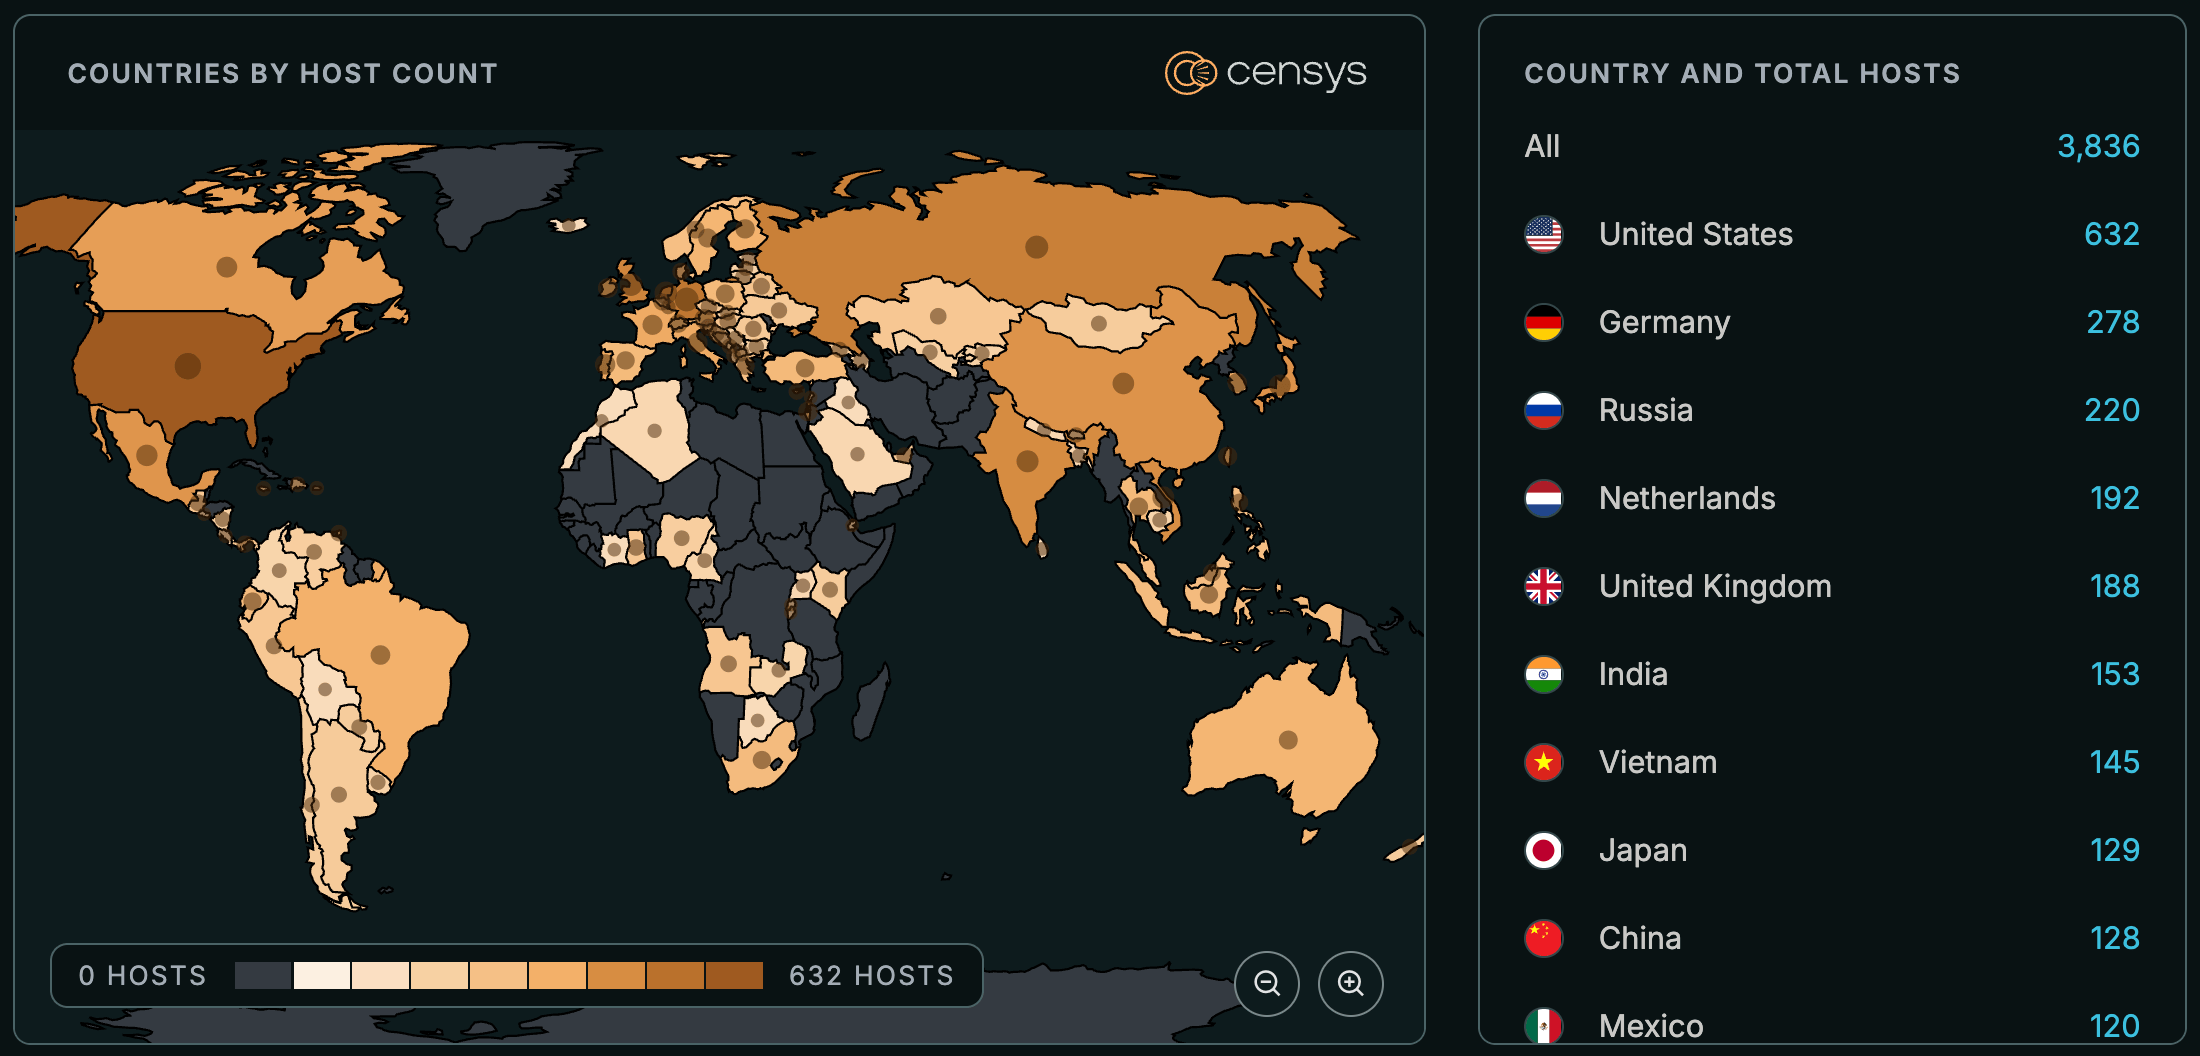
“Censys observes 3,836 hosts globally carrying the Security Management/Log Server role, identified by the Security Internal Communication (SIC) identity Check Point assigns management servers by default rather than by version, since build and Jumbo Hotfix level are not visible in passive scan data.” reads the advisory by Censys. “This figure is total role presence, not a confirmed-vulnerable count.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, CVE-2026-91843)