
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

DoJ indicted a member of China-based hacking group behind Anthem hack

US DoJ indicted a member of sophisticated China-based hacking group for series of computer intrusions. The group is also responsible for the 2015 Health Insurer Anthem data breach. The US Department of Justice indicted Fujie Wang (32), a member of sophisticated Chinese hacking group that breached at several US companies, including the health insurer Anthem […]

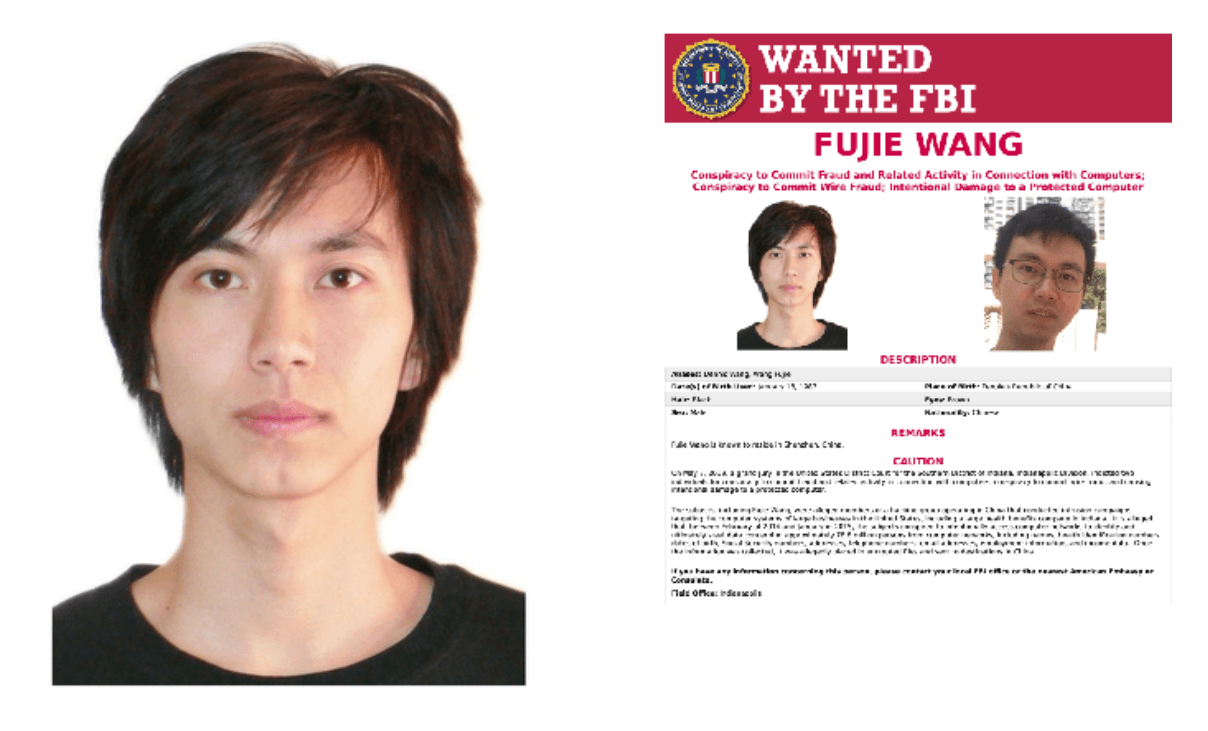
wang chinese hacker anthem

US DoJ indicted a member of sophisticated China-based hacking group for series of computer intrusions. The group is also responsible for the 2015 Health Insurer Anthem data breach.

The US Department of Justice indicted Fujie Wang (32), a member of sophisticated Chinese hacking group that breached at several US companies, including the health insurer Anthem Inc. back in 2015.

“A federal grand jury returned an indictment unsealed today in Indianapolis, Indiana, charging a Chinese national as part of an extremely sophisticated hacking group operating in China and targeting large businesses in the United States, including a computer intrusion and data breach of Indianapolis-based health insurer Anthem Inc. (Anthem). ” reads the press release published by DoJ.

Starting from February 2014, Fujie Wang and other members of the hacking group, including another Chinese individual charged as John Doe, carried out a series of spear-phishing attacks on U.S.-based organizations. 

Wang and Doe are charged with one count of conspiracy to commit fraud and related activity in relation to computers and identity theft, one count of conspiracy to commit wire fraud, and two substantive counts of intentional damage to a protected computer.

Then defendants installed malware and tools on the compromised systems to further compromise the computer networks of the victim businesses.

Once inside a target company’s network, they stole data of interest, including personally identifiable information (PII) and confidential business information.

The group targeted at least four US companies between February 2014 and January 2015, court documents only named Anthem as one of the victims.

“The allegations in the indictment unsealed today outline the activities of a brazen China-based computer hacking group that committed one of the worst data breaches in history,” said Assistant Attorney General Benczkowski.  “These defendants allegedly attacked U.S. businesses operating in four distinct industry sectors, and violated the privacy of over 78 million people by stealing their PII.  The Department of Justice and our law enforcement partners are committed to protecting PII, and will aggressively prosecute perpetrators of hacking schemes like this, wherever they occur.”

Wang is alleged to have controlled two domain names connected to the cyber attacks, one of which was associated with a backdoor used in the intrusion of the Victim Business 1’s network. The other domain name was associated by Wang with a server used to create an email account used to conduct spearfishing attacks against employees of Victim Business 3. 

The indictment doesn’t link the Chinese hacking crew with China-linked APT groups.

Wang is currently on the FBI’s Most Wanted Cyber list and is still at large.

wang chinese hacker anthem
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Chinese hackers, Anthem)

[adrotate banner=”5″]

[adrotate banner=”13″]


