
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Details for 1.9M members of Chinese Communist Party Members leaked

Security experts from Cyble discovered that the details of 1.9 million members of the Chinese Communist Party were leaked on a hacking forum. During routine Dark web monitoring, the experts from Cyble found a post on a Russian-speaking forum offering the details of 1.9 million members of Chinese Communist Party. The huge trove of data, […]

Chinese Communist Party

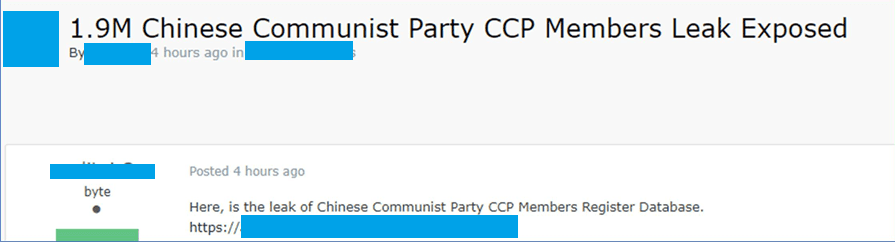
Security experts from Cyble discovered that the details of 1.9 million members of the Chinese Communist Party were leaked on a hacking forum.

During routine Dark web monitoring, the experts from Cyble found a post on a Russian-speaking forum offering the details of 1.9 million members of Chinese Communist Party.

The huge trove of data, a 293 MB CSV file, was offered for free. The exposed records included name, sex, ethnicity, organization, hometown, ID, Address, Mobile Number, Phone Number, Education.

Chinese Communist Party

“People who are concerned about their information exposure can register on Cyble’s data breach monitoring and notification platform, AmiBreached.com, to ascertain the risks at no cost. Also, Android users (Link) and iOS users (Link) can gain full access to it just by downloading the mobile application.” states the post published by Cyble.

Below a list of suggestions provided by Cyble to prevent cyber-attacks:

  • Never click on unverified/unidentified links
  • Do not open untrusted email attachments
  • Only download media from sites you trust
  • Never use unfamiliar USBs
  • Use security software and keep it updated
  • Backup your data periodically
  • Keep passwords unique and unpredictable
  • Keep Software and Systems up to date
  • Train employees on Cyber Security
  • Set up Firewall for your internet
  • Take a Cyber Security assessment
  • Update passwords regularly
[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Chinese Communist Party)

[adrotate banner=”5″]

[adrotate banner=”13″]


