
Security experts have discovered that hackers have stolen 700,000 records from Choice Hotels franchise and are demanding payment for their return.
Experts at Comparitech with the help of the popular researcher Bob Diachenko discovered an unsecured database containing 700,000 records from the hotel franchise Chain Hotel. The experts discovered the unsecured MongoDB archive containing 5.6 million records on July 2, 2019, after the archive was indexed by the BinaryEdge search engine.
“Hackers claim to have stolen 700,000 guest records belonging to Choice Hotels, one of the largest hotel chains in the world. Comparitech collaborated with security researcher Bob Diachenko to uncover the unsecured database, which was left exposed and accessible to anyone with an internet connection.” reads a blog post published by Comparitech.
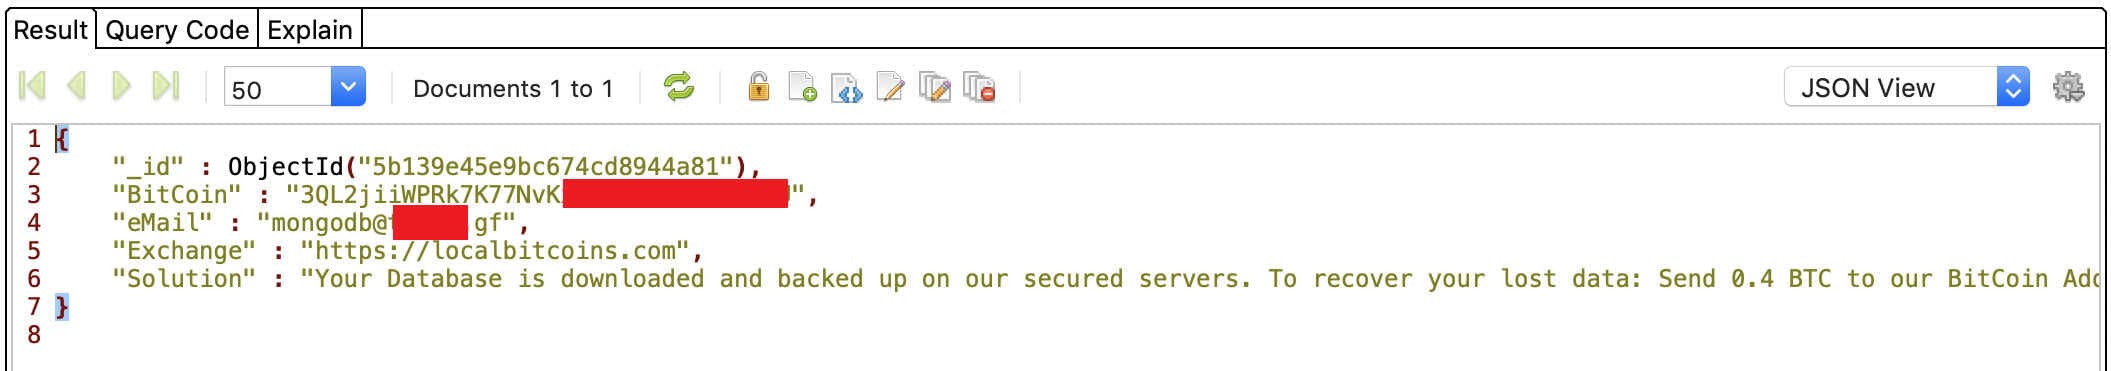
“Diachenko immediately notified the company of the exposed MongoDB instance, but it appears malicious actors got to it first. They left a ransom note demanding 0.4 Bitcoin, or $3,856 as of time of writing.
Choice Hotels attempted to downplay the problem explaining that most of the records in the archive contained test information, except for 700,000 entries that were genuine.
Exposed records contained guests data, including names, email addresses, and phone numbers.
Diachenko immediately reported his findings to Choice Hotels, however, crooks have already got access to the data and attempted to blackmail the business.
Analyzing the database, Diachenko discovered a ransom note left by hackers that demanded 0.4 BTC ($4,000) from the company. Likely the intruders have made a backup of the data and were going to wipe the archive before demanding the payment of the ransom.

The company revealed that the database was hosted on a vendor’s server.
“The vendor was working with the data as part of a proposal to provide a tool,” a company representative told Comparitech.
“We have discussed this matter with the vendor and will not be working with them in the future. We are evaluating other vendor relationships and working to put additional controls in place to prevent any future ccurrences of this nature. We are also establishing a Responsible Disclosure Program, and we welcome Mr. Diachenko’s assistance in helping us identify any gaps.”
The database remained exposed from June 30, when it was first indexed by BinaryEdge, to July 2, when it was secured by the vendor.
On July 28, the expert sent a second notification to Choice Hotels, then the company launched an investigation on the data leak.
“We are evaluating other vendor relationships and working to put additional controls in place to prevent any future occurrences of this nature,” Choice Hotels told Comparitech. “We are also establishing a Responsible Disclosure Program, and we welcome Mr.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – Choice Hotel, data leak)
[adrotate banner=”5″]
[adrotate banner=”13″]


