
Cisco confirms that data published by IntelBroker on a cybercrime forum was taken from the company DevHub environment.
Cisco confirms that the data posted by the notorious threat actor IntelBroker on a cybercrime forum was stolen from its DevHub environment.
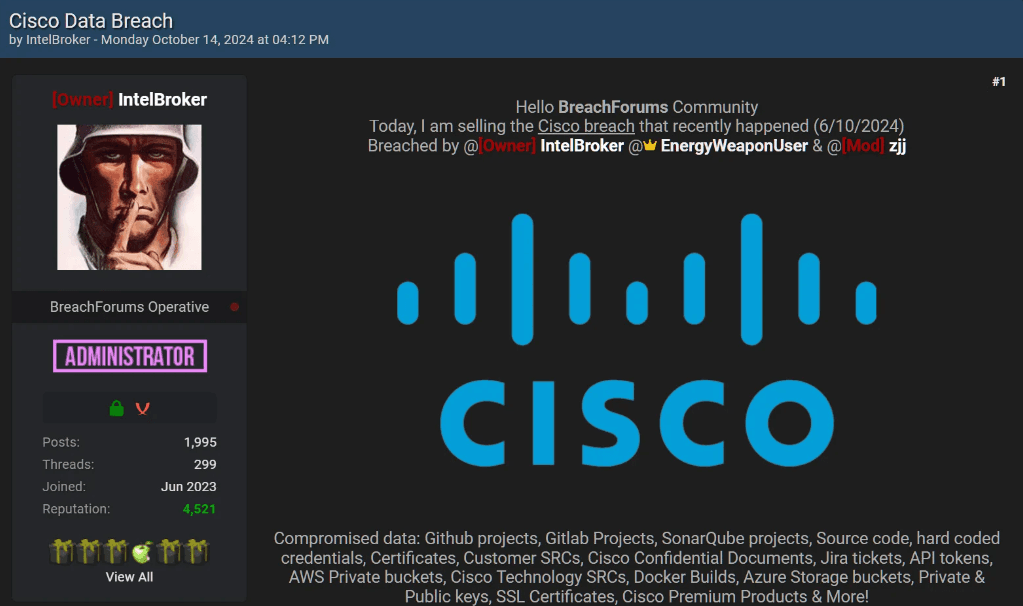
IntelBroker claimed to have gained access to Github projects, Gitlab Projects, SonarQube projects, Source code, hard coded credentials, Certificates, Customer SRCs, Confidential Documents, Jira tickets, API tokens, AWS Private buckets, company Technology SRCs, Docker Builds, Azure Storage buckets, Private & Public keys, SSL Certificates, Cisco Premium Products, and other info.
“Hello BreachForums Community, Today, I am selling the Cisco breach that recently happened (6/10/2024)” reads the message published by IntelBroker. “Compromised data: Github projects, Gitlab Projects, SonarQube projects, Source code, hard coded credentials, Certificates, Customer SRCs, Cisco Confidential Documents, Jira tickets, API tokens, AWS Private buckets, Cisco Technology SRCs, Docker Builds, Azure Storage buckets, Private & Public keys, SSL Certificates, Cisco Premium Products & More!”

Immediately, the company launched an investigation, which is still ongoing, into the alleged security incident.
The networking giant doesn’t believe that its infrastructure was not compromised.
“Cisco is investigating reports that an unauthorized actor is alleging to have gained access to certain Cisco data and data of our customers.” reads the Reports of Security Incident published by the company. “Cisco takes this allegation seriously and we have engaged law enforcement as part of this investigation. To date, our investigation has found no evidence of our systems being impacted.”
Cisco states that the attackers obtained the data from a public-facing DevHub environment.
DevHub is a platform designed for developers to access resources, tools, and APIs to build and integrate applications with Cisco’s technologies. It provides a range of development resources, including SDKs (Software Development Kits), documentation, sample code, and learning materials for networking, security, and cloud infrastructure.
Below is an update published on October 18, 2024:
- Based on our investigations, we are confident that there has been no breach of our systems.
- We have determined that the data in question is on a public-facing DevHub environment—a Cisco resource center that enables us to support our community by making available software code, scripts, etc. for customers to use as needed.
- At this stage in our investigation, we have determined that a small number of files that were not authorized for public download may have been published.
- As of now, we have not observed any confidential information such as sensitive PII or financial data to be included but continue to investigate to confirm.
- Out of an abundance of caution, we have disabled public access to the site while we continue the investigation.
- Meanwhile, Cisco will engage directly with customers if we determine they have been impacted by this event.
The company has disabled public access to the site while we continue the investigation.
IntelBroker targeted many major organizations in past attacks, including AMD, AT&T, Bank of America, Microsoft, Europol, SAP, T-Mobile, Verizon, and others.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)


