

Cisco patched a critical Nexus 9000 vulnerability, CVE-2026-20212, allowing unauthenticated remote root code execution.
Cisco has released patches for a critical flaw, tracked as tracked as CVE-2026-20212 (CVSS score of 9.8) in 10 Silicon One-based Nexus 9000 switches. The vulnerability could let an unauthenticated remote attacker execute code with root privileges.
Cisco’s Technical Assistance Center (TAC) discovered the flaw while investigating a customer support case.
The flaw exists because TCP ports 43210 and 43211 are exposed through the default Layer 3 VRF. An attacker could connect remotely and send specially crafted data that gets executed with root privileges. The attack could also crash the S1HAL process, potentially forcing the affected device to reload.
“A vulnerability in the Silicon One integration for Cisco Nexus 9000 Series Switches could allow an unauthenticated, remote attacker to execute code with root privileges.” reads the advisory. “This vulnerability exists because TCP ports 43210 and 43211 are accessible in the default Layer 3 (L3) virtual routing and forwarding (VRF). A successful exploit could allow the attacker to connect to an affected device and send crafted input that could be executed as code with root privileges. The exploitation of this vulnerability could also cause the S1HAL process to crash, which could cause the device to reload.”
The vulnerability affects Cisco Nexus 9000 Series switches equipped with a Silicon One ASIC.
At the time of disclosure, the following models were known to include the affected Silicon One hardware:
- N9324C-SE1U
- N9348Y2C6D-SE1U
- N9364E-SG2-O
- N9364E-SG2-Q
- N9396T12C-SE1
- N9348Y12C-SE1
- N9396Y12C-SE1
- N9336C-SE1
- N9K-C9804
- N9K-C9808
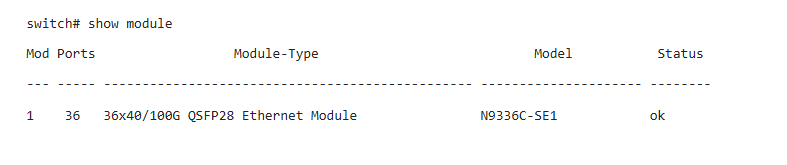
Administrators can check the Product ID (PID) of a switch by running the show module command. For example, the output below shows N9336C-SE1, which is one of the affected models.
Other Nexus 9000 models are not affected. The same applies to Nexus 9000 switches running in ACI mode, as well as the Nexus 3000 and Nexus 7000 series.
Cisco provides a workaround to reduce the risk of remote exploitation. Administrators can use infrastructure access control lists (iACLs) to allow only the management and control traffic that the affected switch actually needs. Another option is to block TCP traffic to locally configured IP addresses on ports 43210 and 43211.
Cisco has also released a Live Protect shield for CVE-2026-20212. The shield provides temporary protection while organizations prepare to install the proper software update.
However, Cisco recommends upgrading to a fixed NX-OS release as the permanent solution. Before deploying any workaround or mitigation, administrators should test it in their own environment, as it could affect network functionality or performance.
Cisco says its Product Security Incident Response Team (PSIRT) is not aware of any public disclosure or active exploitation of this vulnerability.
“The Cisco Product Security Incident Response Team (PSIRT) is not aware of any public announcements or malicious use of the vulnerability that is described in this advisory.” concludes the advisory.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Cisco)


