
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

High severity bug discovered in CISCO NETFLOW GENERATION APPLIANCE

A flaw in Cisco NetFlow Generation Appliance tracked as CVE-2017-3826, could be exploited by an unauthenticated, remote attacker to cause a DoS condition. “A vulnerability in the Stream Control Transmission Protocol (SCTP) decoder of the Cisco NetFlow Generation Appliance (NGA) could allow an unauthenticated, remote attacker to cause the device to hang or unexpectedly reload, causing a denial […]

High severity bug discovered in CISCO NETFLOW GENERATION APPLIANCE

A flaw in Cisco NetFlow Generation Appliance tracked as CVE-2017-3826, could be exploited by an unauthenticated, remote attacker to cause a DoS condition.

“A vulnerability in the Stream Control Transmission Protocol (SCTP) decoder of the Cisco NetFlow Generation Appliance (NGA) could allow an unauthenticated, remote attacker to cause the device to hang or unexpectedly reload, causing a denial of service (DoS) condition.” reads the Cisco Security Advisory.

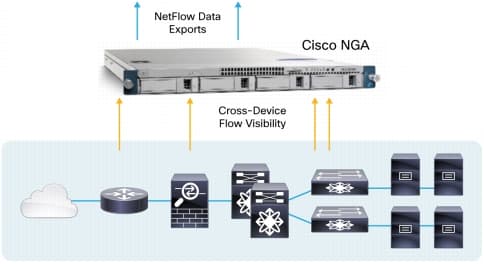
NetFlow Generation Appliances are used in enterprise data centers to monitor Gigabit Ethernet high-throughput networks.

According to Cisco, the vulnerability resides in the hardware’s Stream Control Transmission Protocol (SCTP) used by the appliance.

The flaw is due to incomplete validation of SCTP packets being monitored on the Cisco NetFlow Generation Appliance data ports. The attackers can trigger the flaw by sending malformed SCTP packets on a network that is monitored by an NGA data port.

“SCTP packets addressed to the IP address of the NGA itself will not trigger this vulnerability. An exploit could allow the attacker to cause the appliance to become unresponsive or reload, causing a DoS condition. User interaction could be needed to recover the device using the reboot command from the CLI.” continues the advisory.

The bug impacts Cisco NetFlow Generation Appliances NGA 3140, NGA 3240 and NGA 3340.

High severity bug discovered in CISCO NETFLOW GENERATION APPLIANCE

Cisco this week has released a security patch for its devices and the IT giant confirmed that there are no workarounds to fix the issue. Users need to apply the security update (Cisco NetFlow Generation Appliance Software release 1.1 (1a)) that fixes the bug as soon as possible.

The security patch is not available for the model NGA 3140 because it was dismissed on January 11, 2014.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Cisco NetFlow Generation Appliance, DoS)


