
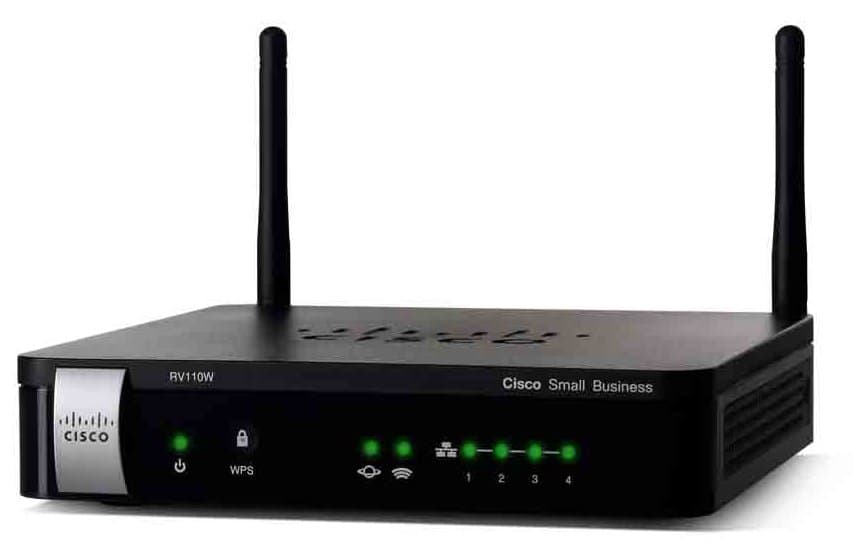
Cisco announced that it will not release updates to fix the CVE-2022-20825 flaw in end-of-life Small Business RV routers.
Cisco will not release updates to address the CVE-2022-20825 RCE flaw in end-of-life Small Business RV routers and encourage upgrading to newer models.
The vulnerability, which received a CVSS severity rating of 9.8 out of 10.0, resides in the web-based management interface of Cisco Small Business RV110W, RV130, RV130W, and RV215W Routers.

An unauthenticated, remote attacker could trigger the issue to execute arbitrary code or cause a denial of service (DoS) condition. The issue is simple to exploit, an attacker could trigger it by sending a specially crafted request to the web-based management interface. Its exploitation requires that the devices have the web-based remote management interface enabled on WAN connections.
“This vulnerability is due to insufficient user input validation of incoming HTTP packets. An attacker could exploit this vulnerability by sending a crafted request to the web-based management interface. A successful exploit could allow the attacker to execute arbitrary commands on an affected device using root-level privileges.” reads the Cisco advisory. “Cisco has not released software updates that address this vulnerability. There are no workarounds that address this vulnerability.”
The vulnerability was reported by security researcher Puzhuo Liu from IIE, CAS.
The IT giant states that there are no workarounds that address this vulnerability.
The Cisco Product Security Incident Response Team (PSIRT) is not aware of any public announcements or attacks in the wild exploiting this vulnerability.
Cisco recently addressed a critical bypass authentication vulnerability affecting Email Security Appliance (ESA) and Secure Email and Web Manager. The flaw, tracked as CVE-2022-20798 (CVSS score 9.8), can be exploited by an unauthenticated, remote attacker to bypass authentication and log in to the web management interface of a vulnerable device.
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Cisco)
[adrotate banner=”5″]
[adrotate banner=”13″]


