
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Cloak ransomware group hacked the Virginia Attorney General’s Office

The Cloak ransomware group claims responsibility for a cyberattack on the Virginia Attorney General’s Office that occurred in February. The ransomware group Cloak has claimed responsibility for a February cyberattack on the Virginia Attorney General Office. A cyberattack on the Virginia Attorney General’s Office forced officials to shut down IT systems, including email and VPN, […]

Virginia Attorney General’s Office

The Cloak ransomware group claims responsibility for a cyberattack on the Virginia Attorney General’s Office that occurred in February.

The ransomware group Cloak has claimed responsibility for a February cyberattack on the Virginia Attorney General Office.

A cyberattack on the Virginia Attorney General’s Office forced officials to shut down IT systems, including email and VPN, and revert to paper filings. Chief Deputy AG Steven Popps called it a “sophisticated attack.” The breach was detected in February, leading to notifications to the FBI, Virginia State Police, and the Virginia Information Technologies Agency. Investigations are ongoing to assess the impact and source of the attack.

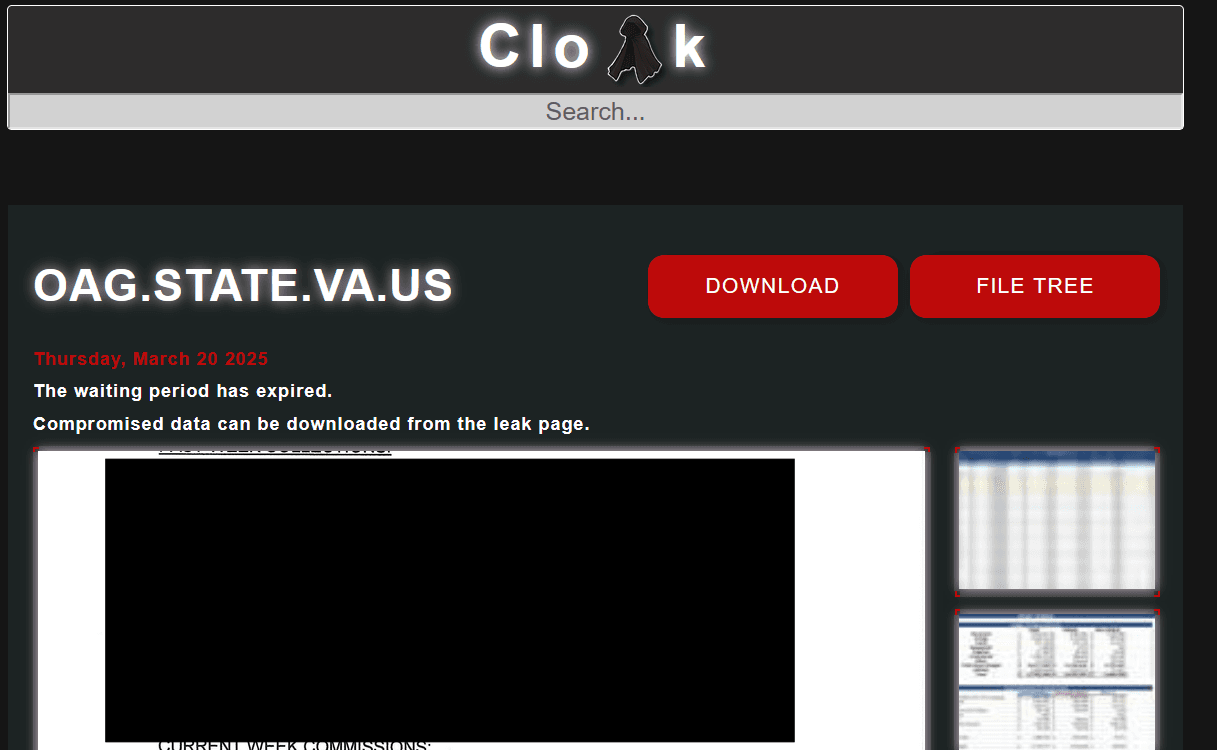
The Virginia Attorney General’s Office did not share details about the attack. On March 20, 2025, the group added the VA General’s Office to the list of victims on its Tor leak site.

The group said that the waiting period had expired and claimed the theft of 134GB of sensitive data.

Initially, the group published screenshots of stolen data as proof of the attack, now the whole archive can be downloaded from the leak page.

The Cloak ransowmare group has been active since at least 2023 and breached more than one hundred organizations across the years.

“Cloak primarily targets small to medium-sized businesses in Europe, with Germany as a key focus. The group has extended its operations to countries in Asia and targets various sectors, including healthcare, real estate, construction, IT, food, and manufacturing.” reads a report published by Halcyon. “Cloak’s attack strategy involves acquiring network access through Initial Access Brokers (IABs) or social engineering methods such as phishing, malvertising, exploit kits, and drive-by downloads disguised as legitimate updates like Microsoft Windows installers.”

The group uses an ARCrypter ransomware variant, derived from Babuk’s leaked code, to encrypt files after infiltrating a network.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


