Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Clop Ransomware group claims the breach of The Washington Post

The Clop Ransomware group claims the breach of The Washington Post and added the American daily newspaper to its Tor data leak site. The Clop Ransomware group announced the hack of the prestigious American daily newspaper The Washington Post. The cybercrime group created a page for the university on its Tor data leak site and announced it will […]

The Washington Post

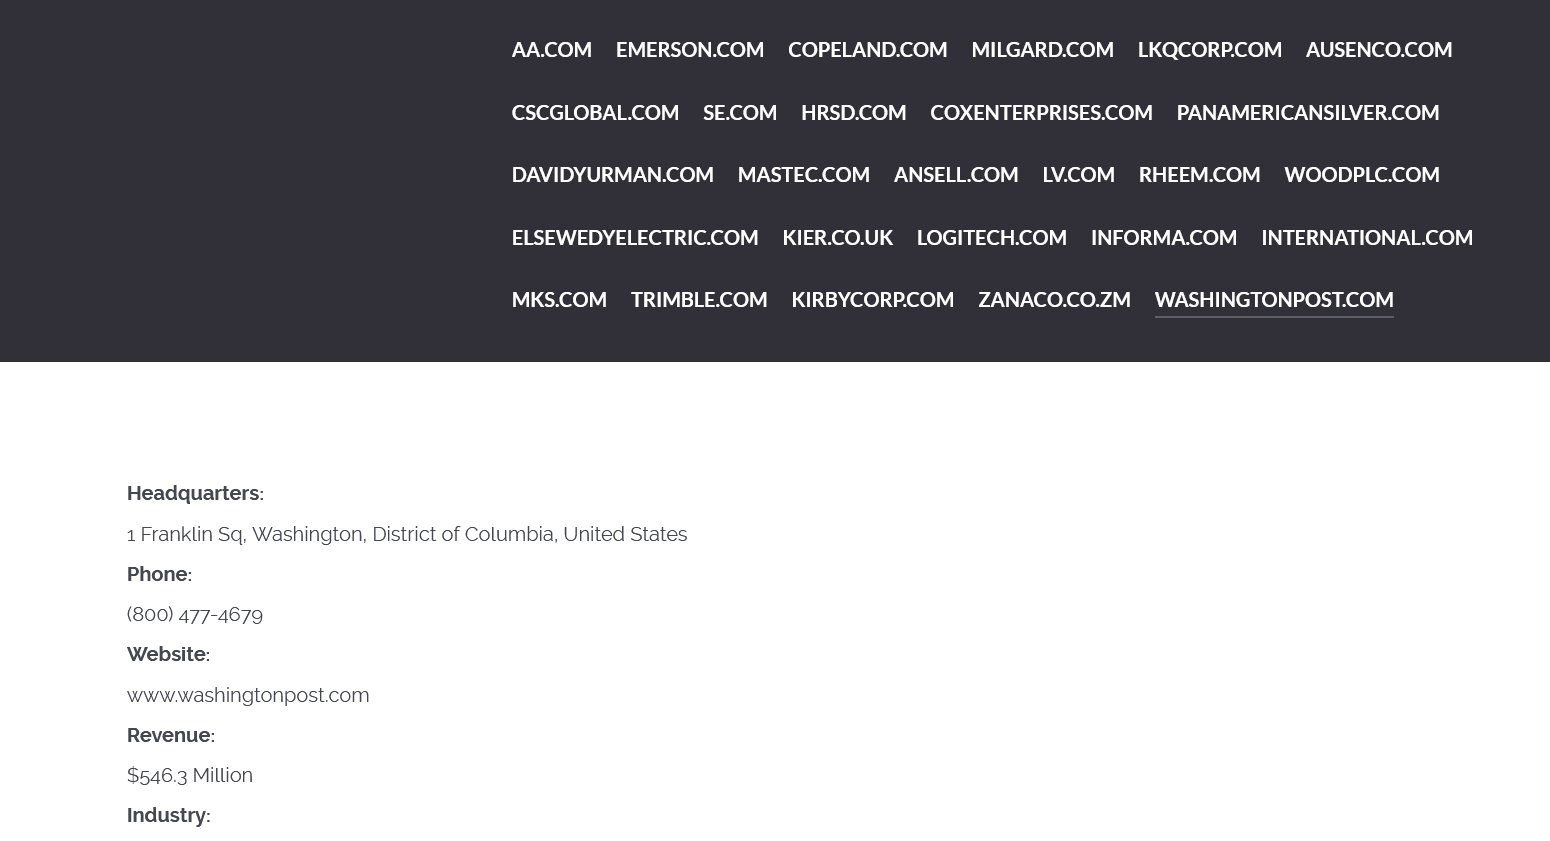
The Clop Ransomware group claims the breach of The Washington Post and added the American daily newspaper to its Tor data leak site.

The Clop Ransomware group announced the hack of the prestigious American daily newspaper The Washington Post. The cybercrime group created a page for the university on its Tor data leak site and announced it will leak the stolen data soon.

The group claimed the company was breached due to its neglect of security, despite its responsibility to protect customers.

“The company doesn’t care about its customers, it ignored their security!!!”

In mid-October, the Clop Ransomware group claimed the breach of The Washington Post and added the American daily newspaper to its Tor data leak site.

Clop (aka Cl0p) is a prolific Russian-speaking ransomware-as-a-service group specializing in big-game hunting and double-extortion.

The Clop ransomware group first appeared on the threat landscape around February 2019, emerging from the TA505 cybercrime group, a financially motivated gang active since at least 2014.

Like other Russia-based threat actors, Clop avoids targets in former Soviet countries and its malware can’t be activated on a computer that operates primarily in Russian.

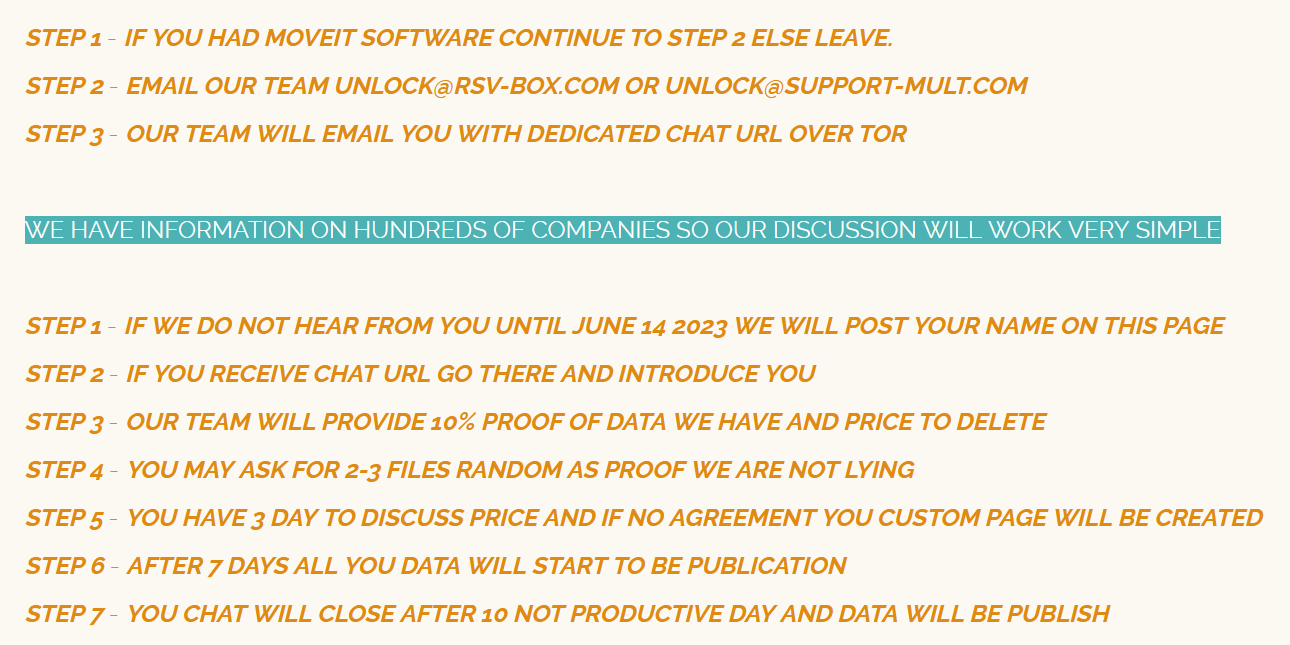
Operators and affiliates identify high-value targets, steal sensitive data, encrypt networks, then publish stolen files on data-leak sites to pressure victims into paying. Clop exploits zero-days and vulnerable third-party software (e.g., MOVEit, GoAnywhere, Oracle EBS), leverages initial-access brokers and automation, and uses sophisticated evasion and lateral-movement techniques to maximize impact and monetization.

Clop’s victims include Shell, British Airways, Bombardier, University of Colorado, PwC, and the BBC.

The group conducted major campaigns including:

  • GoAnywhere MFT (2023): Targeted a flaw (CVE-2023-0669) to compromise over 130 organizations.
  • MOVEit Transfer (2023): One of the largest ransomware campaigns in history, impacting hundreds of companies worldwide, including US and European firms, through an SQL injection zero-day (CVE-2023-34362).
  • Accellion FTA (2020–2021): Exploited a zero-day in the file-transfer appliance to steal data from ~100 organizations.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, The Washington Post)