
Threat actors are actively abusing cloud services from Amazon and Microsoft to deliver RATs such as Nanocore, Netwire, and AsyncRAT.
Threat actors are actively exploiting public cloud services from Amazon and Microsoft to spread RATs such as Nanocore, Netwire, and AsyncRAT used to steal sensitive information from compromised systems.
The malware campaign was spotted by Cisco Talos in October 2021, most of the victims were located in the United States, Italy and Singapore.
Threat actors leverages cloud services like Azure and AWS because they can be easily set up with minimal efforts making it more difficult for defenders to detect and mitigate the campaigns.
The attackers used complex obfuscation techniques in the downloader script.
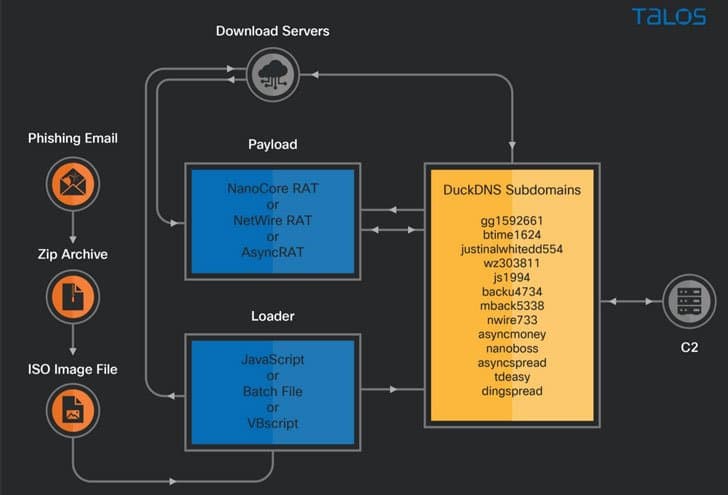
The attack chains starts with a phishing email using a malicious ZIP attachment that contain an ISO image with a loader in the form of JavaScript, a Windows batch file or Visual Basic script. Upon executing the initial script, the victim’s machine download the next stage from the C2 server, which can be hosted on an Azure Cloud-based Windows server or an AWS EC2 instance.
“To deliver the malware payload, the actor registered several malicious subdomains using DuckDNS, a free dynamic DNS service. The malware families associated with this campaign are variants of the Netwire, Nanocore and AsyncRAT remote access trojans.” reads the analysis published by Talos. “Organizations should be inspecting outgoing connections to cloud computing services for malicious traffic. The campaigns described in this post demonstrate increasing usage of popular cloud platforms for hosting malicious infrastructure.”

Once installed the malware on the target system, it can be used to steal confidential data or to deliver additional payloads such as ransomware attacks. Threat actors can also sell the access to other cybercrime gangs, including ransomware affiliates.
“Organizations should deploy comprehensive multi-layered security controls to detect similar threats and safeguard their assets. Defenders should monitor traffic to their organization and implement robust rules around the script execution policies on their endpoints. It is even more important for organizations to improve email security to detect and mitigate malicious email messages and break the infection chain as early as possible.” concludes the report that also includes Indicators of Compromise (IoCs).
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, cloud services)
[adrotate banner=”5″]
[adrotate banner=”13″]


