
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Maritime transport and logistics giant CMA CGM hit with ransomware

The French maritime transport and logistics giant CMA CGM S.A. revealed it was the victim of a malware attack that affecting some servers on its network. CMA CGM S.A., a French maritime transport and logistics giant, revealed that a malware attack affected some servers on its network. The company is present in over 160 countries through 755 […]

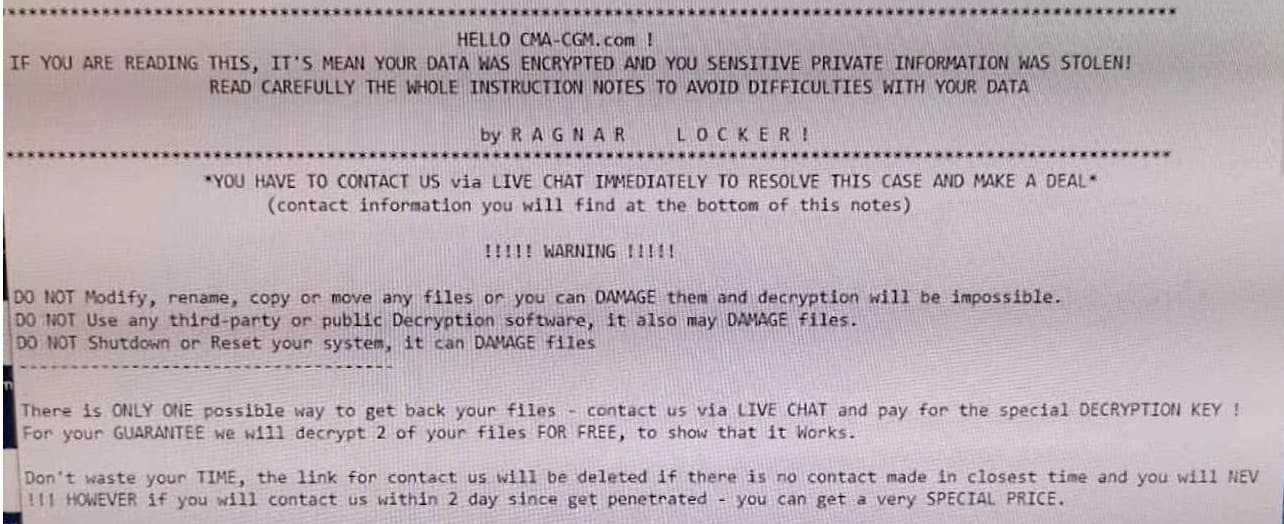
CMA CGM ransom note

The French maritime transport and logistics giant CMA CGM S.A. revealed it was the victim of a malware attack that affecting some servers on its network.

CMA CGM S.A., a French maritime transport and logistics giant, revealed that a malware attack affected some servers on its network.

The company is present in over 160 countries through 755 offices and 750 warehouses with 110,000 employees and 489 vessels. CMA CGM serves 420 of the world’s 521 commercial ports and operates on more than 200 shipping lines. 

The company currently ranks fourth behind Maersk Line, MSC, and COSCO Shipping Lines, all companies that have been curiously hit by malware attacks in the past.

In response to the attack, the IT staff at the CMA CGM isolated some applications for the Internet to avoid the malware from spreading to other systems.

“The CMA CGM Group (excluding CEVA Logistics) is currently dealing with a cyber-attack impacting peripheral servers.” reads the security notice published by the company. “As soon as the security breach was detected, external access to applications was interrupted to prevent the malware from spreading.”

According to a report published by Lloyd’s List, the company’s Chinese offices were allegedly infected with the Ragnar Locker ransomware.

CMA CGM ransom note
Source Lloyds List

The Ragnar Locker appeared in the threat landscape at the end of the 2019 when it was employed in attacks against corporate networks. 

One of the victims of the ransomware is the energy giant Energias de Portugal (EDP), where the attackers claimed to have stolen 10 TB of files.

“The French carrier was asked by hackers using the Ragnar Locker ransomware to contact them within two days ‘via live chat and pay for the special decryption key’. No ransom price has been named yet” reads the report.

At the time of writing, the external access to CMA CGM IT applications is currently unavailable. Customers have to contact their local agencies for all bookings.

The company is investigating the incident with the help of independent experts.

“An investigation is underway, conducted by our internal experts and by independent experts,” continues the notice. “A new communication will be issued at the end of the day.”

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


