
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Are Maze operators behind the attack on the IT services giant Cognizant?

IT services giant Cognizant suffered a ransomware attack on Friday, according to BleepingComputer company was hit by the Maze Ransomware crew. Information technologies services giant Cognizant is the last victim of a ransomware attack, according to BleepingComputer the attack was launched by the Maze Ransomware gang. Cognizant is an American multinational corporation that provides IT services, it is […]

Maze ransomware

IT services giant Cognizant suffered a ransomware attack on Friday, according to BleepingComputer company was hit by the Maze Ransomware crew.

Information technologies services giant Cognizant is the last victim of a ransomware attack, according to BleepingComputer the attack was launched by the Maze Ransomware gang.

Cognizant is an American multinational corporation that provides IT services, it is one of the largest IT managed services company in the world with over $16 billion in revenue.

On Friday, the company sent a security breach notification mail to its clients and shared IoCs related to the threat that affected its systems.

“On Friday, Cognizant began emailing their clients, stating that they had been compromised and included a “preliminary list of indicators of compromise identified through our investigation.” Clients could then use this information to monitor their systems and further secure them.” reported BleepingComputer.

The IOCs provided by the company are associated with past infections attributed to the Maze Ransomware crew, it included IP addresses of servers and file hashes for the kepstl32.dll, memes.tmp, and maze.dll files.

BleepingComputer reached out Maze operators for a comment, but the denied being involved in the attack.

If Maze operators were behind the attack, they likely breached the company network for a long time during which they have stolen credentials and exfiltrated sensitive data.

“It is possible that an attack was conducted but failed to encrypt any devices.” concludes BleepingComputer.

“If the Maze operators conducted this attack, they were likely present in Cognizant’s network for weeks, if not longer.”

Data Breach Notification service UnderTheBreach noticed that on April 11, an operator in the cybercrime underground offered for sale the access to a big enterprise, they speculate the big organizations could be Cognizant.

https://twitter.com/underthebreach/status/1251605359409664005

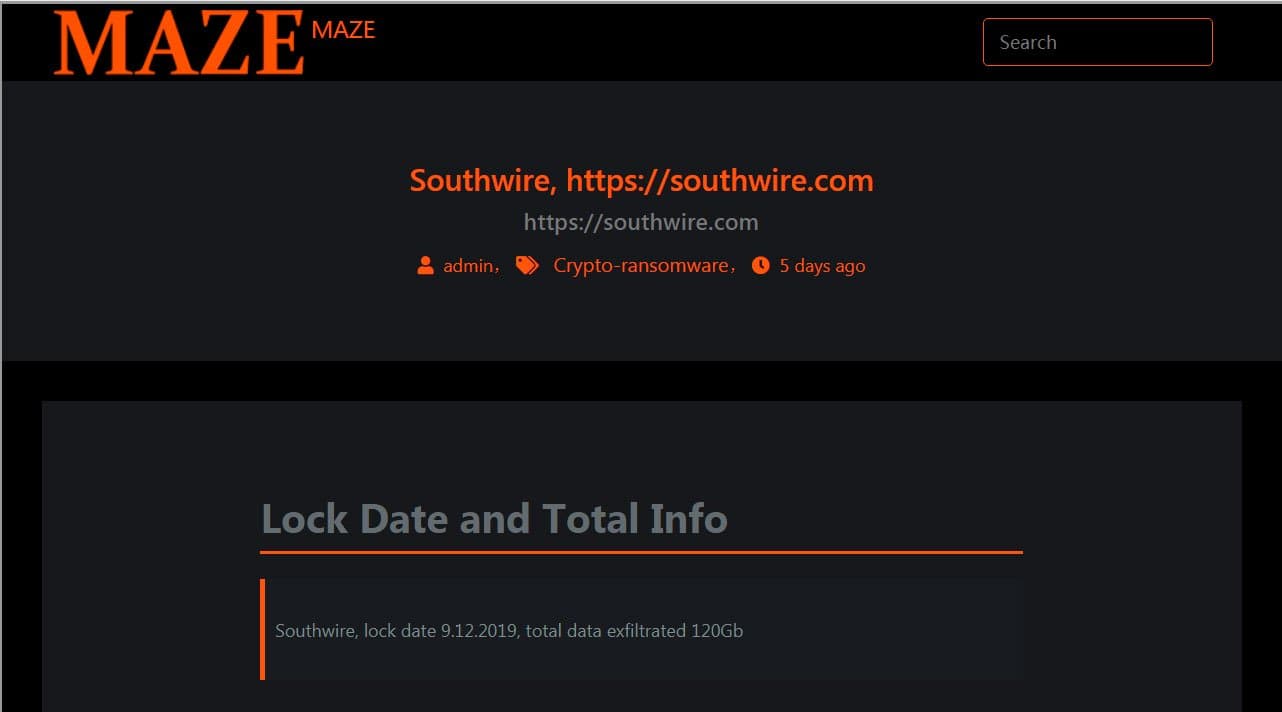
Since December, the victims of the Maze Ransomware are facing another threat because operators behind the malware threaten them to publish their data online.

Maze ransomware

The Maze operators have created a “data leak” site that is used to publish stolen data from victims that did not pay the ransom.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Cognizant, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


