
Researchers with Cisco Talos have monitored a bitcoin phishing campaign conducted by a criminal gang tracked as Coinhoarder that made an estimated $50 million by exploiting Google AdWords.
Researchers with Cisco Talos have monitored a bitcoin phishing campaign for several months with the help of the Ukraine Cyberpolice.
The gang, tracked as Coinhoarder, has made an estimated $50 million by exploiting Google AdWords to trick netizens into visiting Bitcoin phishing sites. This is the element that characterized this phishing campaign, Coinhoarder attackers used geo-targeting filters for their ads, the researchers noticed that hackers were targeting mostly Bitcoin owners in Africa.
The Ukrainian authorities located and shut down the servers hosting some of the phishing websites used by crooks. The phishing sites were hosted on the servers of a bulletproof hosting provider located in Ukraine, Highload Systems. The operation was temporarily disrupted but the police haven’t arrested any individual.
“Cisco has been tracking a bitcoin theft campaign for over 6 months. The campaign was discovered internally and researched with the aid of an intelligence sharing partnership with Ukraine Cyberpolice. The campaign was very simple and after initial setup the attackers needed only to continue purchasing Google AdWords to ensure a steady stream of victims.” reads the analysis published by Talos. “This campaign targeted specific geographic regions and allowed the attackers to amass millions in revenue through the theft of cryptocurrency from victims.”
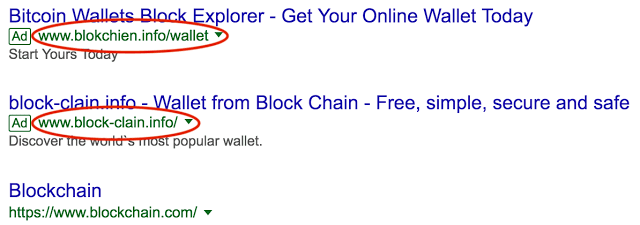
The Coinhoarder group used Google Adwords for black SEO purposes, on February 24, 2017, researchers at Cisco observed a massive phishing campaign hosted in Ukraine targeting the popular Bitcoin wallet site blockchain.info with over 200,000 client queries. Crooks used Google Adwords to poison user search results in order to steal users’ wallets.
Unfortunately, this attack scheme is becoming quite common in the criminal ecosystem, hackers implement it to target many different crypto wallets and exchanges via malicious ads.
The COINHOARDER gang leveraged the typosquatting technique, the hackers used domains imitating the Blockchain.info Bitcoin wallet service in conjunction SSL signed phishing sites in order to appear as legitimate. Based on the number of queries, the researchers confirmed that this is one of the biggest campaigns targeting Blockchain.info to date.
“The COINHOARDER group has made heavy use of typosquatting and brand spoofing in conjunction SSL signed phishing sites in order to appear convincing. We have also observed the threat actors using internationalized domain names.” continues the analysis. “These domains are used in what are called homograph attacks, where an international letter or symbol looks very similar to one in English. Here are some examples from this campaign.
The Punycode (internationalized) version is on the left, the translated (homographic) version on the right:
xn–blockchan-d5a[.]com → blockchaìn[.]com
xn–blokchan-i2a[.]info → blokchaín[.]info”
Talos researchers revealed that one campaign that was conducted between September and December 2017, the group made around $10 million.
“While working with Ukraine law enforcement, we were able to identify the attackers’ Bitcoin wallet addresses and thus, we could track their activity for the period of time between September 2017 to December 2017. In this period alone, we quantified around $10M was stolen.In one specific run, they made $2M within 3.5 week period. ” states Cisco Talos.
Further technical details on the campaign, including Indicators of Compromise are included in the analysis published by Cisco Talos.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Coinhoarder, Bitcoin phishing campaign)
[adrotate banner=”5″]
[adrotate banner=”13″]


