
The former NSA hacker and malware researcher Patrick Wardle is back, this time he spotted a new remote access Trojan dubbed Coldroot RAT.
The Coldroot RAT is a cross-platform that is targeting MacOS systems and the bad news is that AV software is not able to detect it. The malware acts as a keylogger on MacOS systems prior to the OS High Sierra allowing it to capture user passwords and credentials.
Wardle published a detailed analysis of the RAT that is currently available for sale on the underground markets since Jan. 1, 2017, while some versions of the Coldroot RAT code have also been available on GitHub for nearly two years.
The expert explained that the RAT masquerades as an Apple audio driver “com.apple.audio.driver2.app” that when clicked on displays an authentication prompt requesting the victim to provide its MacOS credentials.
“an unflagged file named com.apple.audio.driver2.app caught my eye. It was recently submitted for a scan, in early January. ” wrote Wardle.
“Though currently no AV-engine on VirusTotal flags this application as malicious, the fact it contained a reference to (TCC.db) warranted a closer look.”
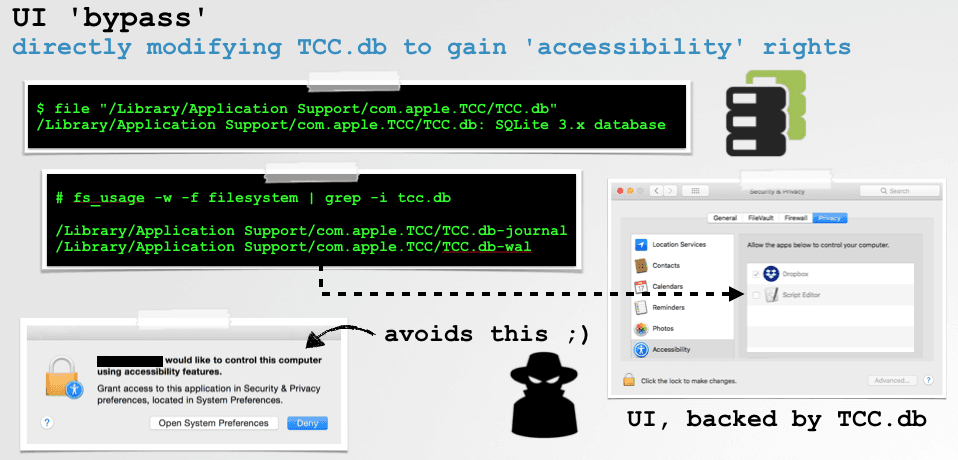
Once obtained the credentials the RAT modifies the privacy TCC.db database. The researchers analyzed a sample that once installed attempts to provide the malware with accessibility rights (so that it may perform system-wide keylogging) by creating the
/private/var/db/.AccessibilityAPIEnabled
file and then modifies the privacy database TCC.db that keep track of the applications installed on the machine and the related level of accessibility rights.
“Think, (ab)using AppleScript, sending simulated mouse events via core graphics, or directly interacting with the file system. An example of the latter was DropBox, which directly modified macOS’s ‘privacy database’ (TCC.db) which contains the list of applications that are afforded ‘accessibility’ rights.” Wardle wrote.
“With such rights, applications can then interact with system UIs, other applications, and even intercept key events (i.e. keylogging). By directly modifying the database, one could avoid the obnoxious system alert that is normally presented to the user: ”

Patrick Wardle explained that the RAT gain persistence by installing itself as a launch daemon.
The researcher highlighted that systems running MacOS High Sierra protect TCC.db via System Integrity Protection (SIP).
“Thought this script is executed as root, on newer versions of macOS (Sierra+) it will fail as the privacy database is now protected by SIP,” Wardle added.
The static analysis of the malware revealed the commands it supports that are:
Repeating this process for the other commands reveals the following capabilities:
- file/directory list
- file/directory rename
- file/directory delete
- process list
- process execute
- process kill
- download
- upload
- get active window
- remote desktop
- shutdown
Patrick Wardle believes that author of the RAT is “Coldzer0” that advertised the malicious code for sale offering the possibility to customize it.
“Besides revealing the likely identify of the malware author, this turns up:
- source code for an old (incomplete) version of Coldroot
- an informative demo video of the malware
The source code, though (as noted), is both old and incomplete – provides some confirmation of our analysis. For example, the PacketTypes.pas file contains information about the malware’s protocol and tasking commands: “
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Coldroot RAT, malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


