
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Security firm Recorded Future discovered the hacker behind Collection #1

Researchers at the threat intel firm Recorded Future, have identified the hacker who amassed credentials in Collection #1 archive. Security experts at the threat intel firm Recorded Future, have discovered the hacker who allegedly created and offered for sale the massive collection known as Collection #1. The ‘Collection #1’ archive was discovered by the cyber security […]

Collection #1

Researchers at the threat intel firm Recorded Future, have identified the hacker who amassed credentials in Collection #1 archive.

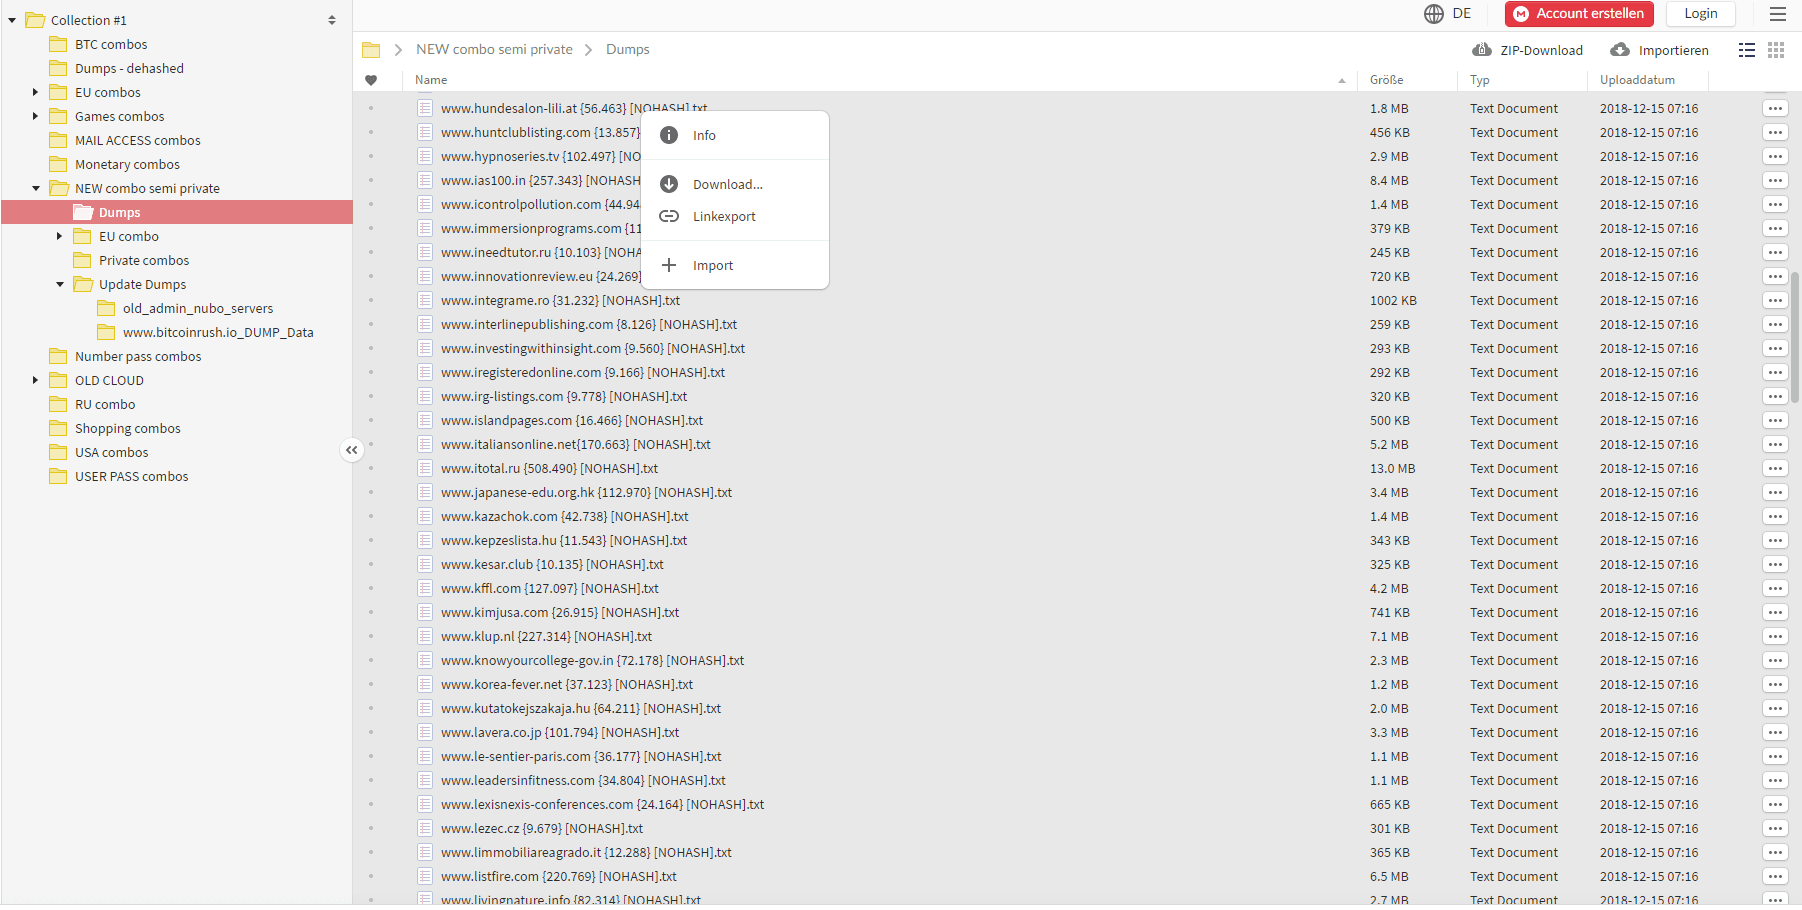
Security experts at the threat intel firm Recorded Future, have discovered the hacker who allegedly created and offered for sale the massive collection known as Collection #1.

The ‘Collection #1’ archive was discovered by the cyber security expert Troy Hunt, it included 773 million records.

Collection #1

The responsible for the sale of the huge trove of data goes online by the moniker of “C0rpz.” C0rpz has collected a huge trove of data through credential stuffing, the ‘Collection #1’ archive is a set of email addresses and passwords totalling 2,692,818,238 rows resulting from thousands of different sources.

According to Hunt, there are 1,160,253,228 unique combinations of email addresses and passwords, while the unique email addresses totalled 772,904,991.

“Recorded Future assesses with moderate confidence that the original creator and seller of Collection #1 was the actor “C0rpz.”” reads the analysis published by Recorded Future.

“Another actor from a well-known Russian hacking forum was also observed sharing a large database of 100 billion user accounts, which possibly has some of the same datasets found in Collection #1. “

Collection #1 was included in a larger dump containing seven other databases:

  • “ANTIPUBLIC #1” (102.04 GB)
  • “AP MYR & ZABUGOR #2” (19.49 GB)
  • “Collection #1” (87.18 GB)
  • “Collection #2” (528.50 GB)
  • “Collection #3” (37.18 GB)
  • “Collection #4” (178.58 GB)
  • “Collection #5” (40.56 GB)

While the AntiPublic dump had already leaked online, the remaining ones were seen for the first time in the hacking underground last month.

According to Recorded Future, C0rpz sold the archives to other hackers that offered them for sale on multiple hacking forums, the collections were also distributed for free via online sharing service MEGA and via torrent magnet links.

Sanix and Clorox are two hackers who bought the data from C0rpz, the former was identified by the investigator Brian Krebs as the source of Collection 1, the latter is the individual who shared Collection for free on Raid Forums.

All the hackers mentioned by Recorded Future were seen for the first time by the experts of the company after the disclosure of Collection #1, they were not involved in previous campaigns or operations.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – credential stuffing, data leak)

[adrotate banner=”5″] [adrotate banner=”13″]


