
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

FBI confirmed that Darkside ransomware gang hit Colonial Pipeline

The U.S. FBI confirmed that the attack against the Colonial Pipeline over the weekend was launched by the Darkside ransomware gang. The U.S. Federal Bureau of Investigation confirmed that the Colonial Pipeline was shut down due to a cyber attack carried out by the Darkside ransomware gang. “The FBI confirms that the Darkside ransomware is […]

darkside US Colonial Pipeline

The U.S. FBI confirmed that the attack against the Colonial Pipeline over the weekend was launched by the Darkside ransomware gang.

The U.S. Federal Bureau of Investigation confirmed that the Colonial Pipeline was shut down due to a cyber attack carried out by the Darkside ransomware gang.

“The FBI confirms that the Darkside ransomware is responsible for the compromise of the Colonial Pipeline networks. We continue to work with the company and our government partners on the investigation.” reads the statement published by the FBI.

US Colonial Pipeline

Source WSJ

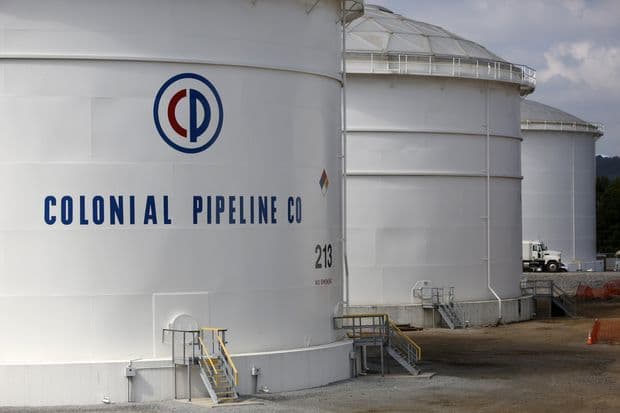
The pipeline allows carrying 2.5 million barrels of refined gasoline and jet fuel each day up the East Coast from Texas to New York, it covers 45 percent of the East Coast’s fuel supplies.

The Darkside ransomware gang first emerged in the threat landscape in August 2020, in recent months the group was very active and targeted organizations worldwide.

Despite its intense activity, early this year the group announced that it will no longer attack organizations in the healthcare industry, companies involved in the development and distribution of COVID-19 vaccines, and funeral service organizations.

“Our goal is to make money, and not creating problems for society. From today we introduce moderation and check each company that our partners want to encrypt to avoid social consequences in the future.” reads a statement published by the gang on its leak site.

Colonial Pipeline is not the first organization in the oil and energy industry targeted by the Darkside ransomware gang, in February the group the Brazilian state-owned electric utility company Copel.

In April, the Darkside ransomware operators announced that they are stepping up their extortion tactics targeting companies that are listed on NASDAQ or other stock markets with a new technique.

The group announced with a message on their leak side that they will provide information stolen from these companies before the publication, so that it would be possible to earn in the reduction price of shares.

The ransomware gang aims at making pressure on the companies threatening them to leak information that could have a negative impact on their stock price, making it possible to traders to make a profit from the fall of the stock prices.

This is an unprecedented tactic in the cybercrime ecosystem.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Colonial Pipeline)

[adrotate banner=”5″]

[adrotate banner=”13″]


