
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Colonial Pipeline discloses data breach after May ransomware attack

Colonial Pipeline discloses a data breach of the personal information of thousands of individuals after the ransomware attack that took place in May 2021. Colonial Pipeline has started notifying more than 5000 people that had their personal information compromised after a ransomware attack that took place in May. The Colonial Pipeline facility in Pelham, Alabama […]

darkside US Colonial Pipeline

Colonial Pipeline discloses a data breach of the personal information of thousands of individuals after the ransomware attack that took place in May 2021.

Colonial Pipeline has started notifying more than 5000 people that had their personal information compromised after a ransomware attack that took place in May.

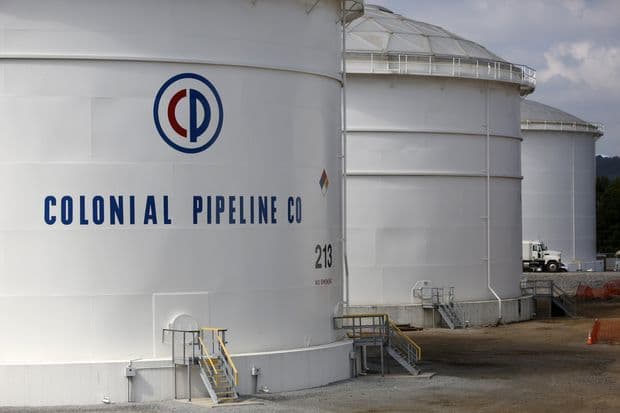
The Colonial Pipeline facility in Pelham, Alabama was hit by a cybersecurity attack, its operators were forced to shut down its systems. The pipeline allows carrying 2.5 million barrels of refined gasoline and jet fuel each day up the East Coast from Texas to New York, it covers 45 percent of the East Coast’s fuel supplies.

US Colonial Pipeline

Source WSJ

The attack was orchestrated by the Darkside ransomware operators, the facility paid a $5 million ransom to recover stolen information. Most of the money was recovered, the US announced in June.

Colonial Pipeline sent out a notification letter to the Maine Attorney General’s Office, saying that 5,810 people was impacted in the attack

“On May 6, 2021, an unauthorized third party acquired certain records stored in our systems,” states the letter. “Total number of persons affected (including residents): 5,810”

Exposed data includes names, birth dates, contact information, driver’s license information, Social Security numbers, government-issued ID (such as military ID and tax ID), and health-related information (including health insurance information).

The company added that not all of this information was affected for each impacted individual.

“We encourage you to remain vigilant by reviewing your account statements and monitoring your free credit reports. In addition, we have arranged to offer you identity restoration and credit monitoring services for two
years at no cost to you.” concludes the letter.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)

[adrotate banner=”5″]

[adrotate banner=”13″]


