Hackers breached one of Comodo Forums, 245,000 users impacted
The ITarian Forum, the Comodo discussion board and support forums, has been hacked and data belonging to nearly 245,000 registered users were exposed. Hackers breached the ITarian Forum, the Comodo discussion board and support forums, accessing login credentials of nearly 245,000 users registered with the Comodo Forums websites. Comodo has not specified which of its […]
The ITarian Forum, the Comodo discussion board and support forums, has been hacked and data belonging to nearly 245,000 registered users were exposed.
Hackers breached the ITarian Forum, the Comodo discussion board and support forums, accessing login credentials of nearly 245,000 users registered with the Comodo Forums websites. Comodo has not specified which of its two forums has been hacked. Exposed data include login username, name, email address, hashed passwords, last IP address used to access the forums, and some social media usernames for a limited number of users.
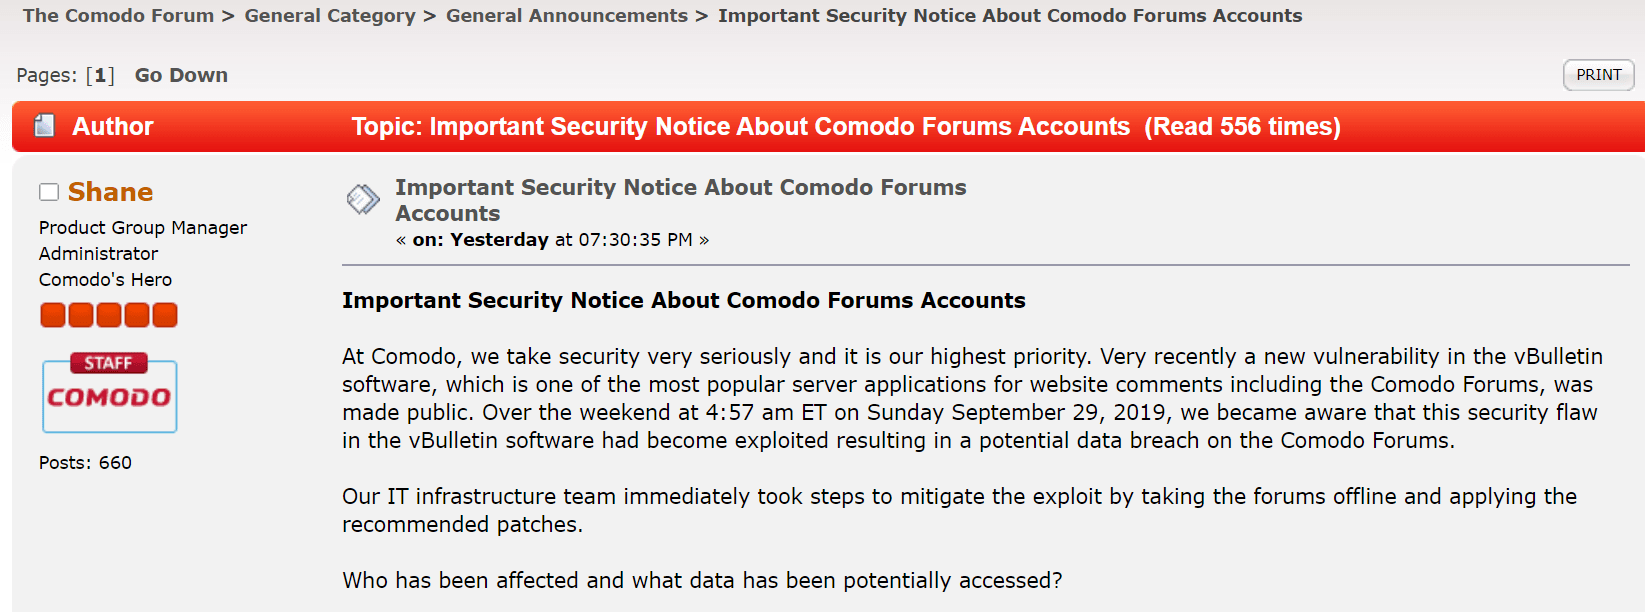
“Very recently a new vulnerability in the vBulletin software, which is one of the most popular server applications for website comments including the Comodo Forums, was made public.” reads the security notice published by Comodo. “Over the weekend at 4:57 am ET on Sunday September 29, 2019, we became aware that this security flaw in the vBulletin software had become exploited resulting in a potential data breach on the Comodo Forums.“
“Our IT infrastructure team immediately took steps to mitigate the exploit by taking the forums offline and applying the recommended patches.”
Comodo attempted to reassure its forum users saying that its staff immediately took the forums offline to apply the necessary countermeasures.
The attackers exploited the recently disclosed zero-day vulnerability in vBulletin(CVE-2019-16759).
The hack of Comodo forum took place on September 29, a few days after vBulletin developers have released a patch to address it, this means that for some reason administrators at Comodo failed in applying it.
vBulletinis one of the most popular forum software, for this reason, the disclosure of a zero-day flaw affecting it could impact a wide audience. More than 100,000 websites online run on top of vBulletin.
On September 24, an anonymous hacker disclosed technical details and proof-of-concept exploit code for a critical zero-day remote code execution flaw in vBulletin.
Two days later, the security expert Troy Mursch of Bad Packets observed a botnet that it utilizing the recently disclosed vBulletin exploit to secure vulnerable servers to avoid that can be compromised by other threat actors. This technique is not new and allows them to preserve their own botnet.
Currently, Comodo operates two forums, “forums.comodo.com,” and ITarian Forum hosted at “forum.itarian.com,” the former runs on the Simple Machines Forum software, while the latter is based on vBulletin.
For this reason, hackers likely breached the ITarian Forum that is used as a discussion board for its customers searching for technical information and assistance.
“As a precautionary measure we recommend that forum users should immediately change their passwords and exercise good password practices such as strong random passwords and not share your passwords across different Internet accounts.” recommends Comodo. “The account passwords were encrypted in vBulletin for the Comodo Forum users, but a password change is recommended as part of good password practices.”“We deeply regret any inconvenience or distress this vulnerability may have caused you, our users,” the company says.