
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Critical Confluence flaw exploited in ransomware attacks

Experts warn threat actors that started exploiting a recent critical flaw CVE-2023-22518 in Confluence Data Center and Confluence Server. Over the weekend threat actors started exploiting a recently disclosed vulnerability (CVE-2023-22518) in all versions of Atlassian Confluence Data Center and Confluence Server. Atlassian last week warned of the CVE-2023-22518 (CVSS score 9.1), the issue is an […]

Confluence flaw

Experts warn threat actors that started exploiting a recent critical flaw CVE-2023-22518 in Confluence Data Center and Confluence Server.

Over the weekend threat actors started exploiting a recently disclosed vulnerability (CVE-2023-22518) in all versions of Atlassian Confluence Data Center and Confluence Server.

Atlassian last week warned of the CVE-2023-22518 (CVSS score 9.1), the issue is an improper authorization issue that can lead to significant data loss if exploited by an unauthenticated attacker.

“As part of our continuous security assessment processes, we have discovered that Confluence Data Center and Server customers are vulnerable to significant data loss if exploited by an unauthenticated attacker.” reads the advisory.

At the time of the initial disclosure, Atlassian was not aware of attacks in the wild exploiting this vulnerability, however, the company urged customers to immediately take action to protect their installs.

The vulnerability was addressed with the release of the following versions:

  • 7.19.16 or later
  • 8.3.4 or later
  • 8.4.4 or later
  • 8.5.3 or later, and
  • 8.6.1 or later

Atlassian states that there is no impact on confidentiality as an attacker cannot exfiltrate any instance data. Confluence sites that are accessed via an atlassian.net domain are not impacted by this issue because are hosted by Atlassian.

On Friday, the software company updated its advisory again revealing that the vulnerability is under active exploitation.

“We received a customer report of an active exploit. Customers must take immediate action to protect their instances. If you already applied the patch, no further action is required.” states the advisory.

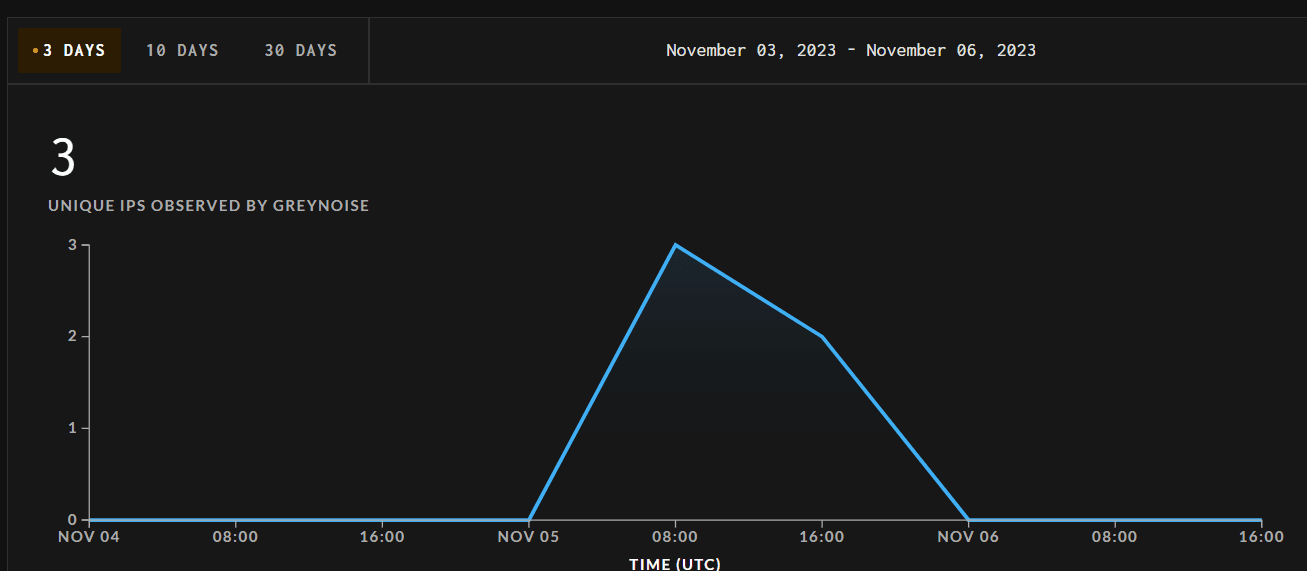
Over the weekend, threat intelligence firm GreyNoise observed exploitation attempts for the vulnerability CVE-2023-22518.

Confluence flaw

Rapid7 researchers observed the exploitation of Atlassian Confluence in multiple customer environments, including for ransomware deployment.

“As of November 5, 2023, Rapid7 Managed Detection and Response (MDR) is observing exploitation of Atlassian Confluence in multiple customer environments, including for ransomware deployment,” reads the report published by Rapid7.

“In multiple attack chains, Rapid7 observed post-exploitation command execution to download a malicious payload hosted at 193.43.72[.]11 and/or 193.176.179[.]41, which, if successful, led to single-system Cerber ransomware deployment on the exploited Confluence server.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


