
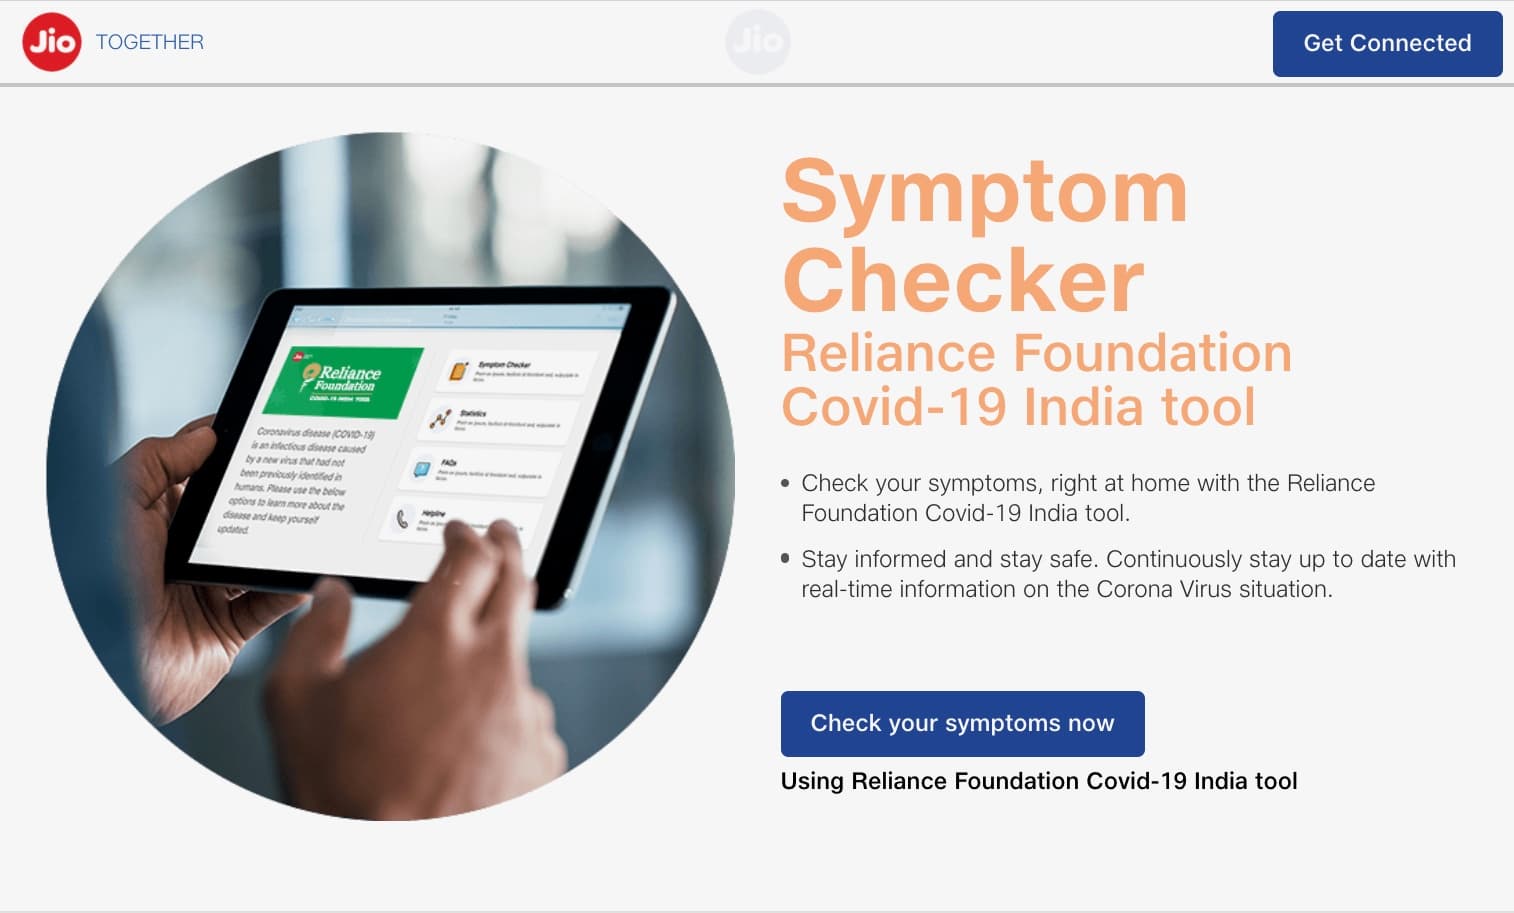
A security glitch in the self-test coronavirus symptom checker developed by India’s Jio cell network exposed test results.
While Coronavirus was spreading worldwide, India’s largest cell network Jio, a subsidiary of Reliance, has developed a coronavirus self-test symptom checker, days before the Indian government imposed a local lockdown to prevent the outbreak.
The app was developed to help users to simply check the COVID-19 symptoms.
A security lapse in the symptom checker application exposed one of its databases online without a password, TechCrunch reported.
The database was discovered by the security researcher Anurag Sen on May 1, immediately after it was first exposed. The researcher shared his discovery with TechCrunch and reported it to Jio. The cell network quickly took pulled the system offline, at the time it is not possible to determine if third-parties accessed the database.
“We have taken immediate action,” said Jio spokesperson Tushar Pania. “The logging server was for monitoring performance of our website, intended for the limited purpose of people doing a self-check to see if they have any COVID-19 symptoms.”
“The database contains millions of logs and records starting April 17 through to the time that the database was pulled offline. Although the server contained a running log of website errors and other system messages, it also ingested vast numbers of user-generated self-test data.” reads the post published by TechCrunch. “Each self-test was logged in the database and included a record of who took the test — such as “self” or a relative, their age, and their gender.“
The database also included user agent, the user’s browser version, the operating system along with data associated with each profile (answers to each question asked by the symptom checker, user’s precise location if allowed).
“From one sample of data we obtained, we found thousands of users’ precise geolocation from across India.” reads the post published by TechCrunch. “TechCrunch was able to identify people’s homes using the latitude and longitude records found in the database.”
Most of the location data is clustered around major cities, like Mumbai and Pune. TechCrunch also found users in the United Kingdom and North America.

Please vote Security Affairs for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – coronavirus symptom checker, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


