
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Crooks leverage Zoom’s popularity in Coronavirus outbreak to serve malware

Online communication platforms such as Zoom are essential instruments at the time of Coronavirus outbreak, and crooks are attempting to exploit their popularity. The Coronavirus outbreak is changing our habits and crooks are attempting to take advantage of the popularity of online communication platforms such as Zoom that are used by businesses, school classrooms and […]

zoom

Online communication platforms such as Zoom are essential instruments at the time of Coronavirus outbreak, and crooks are attempting to exploit their popularity.

The Coronavirus outbreak is changing our habits and crooks are attempting to take advantage of the popularity of online communication platforms such as Zoom that are used by businesses, school classrooms and normal users.

Zoom has over 74,000 customers and 13 million monthly active users, its popularity exploded with the COVID19 outbreak because the platform is used by millions of students, government and private employees.

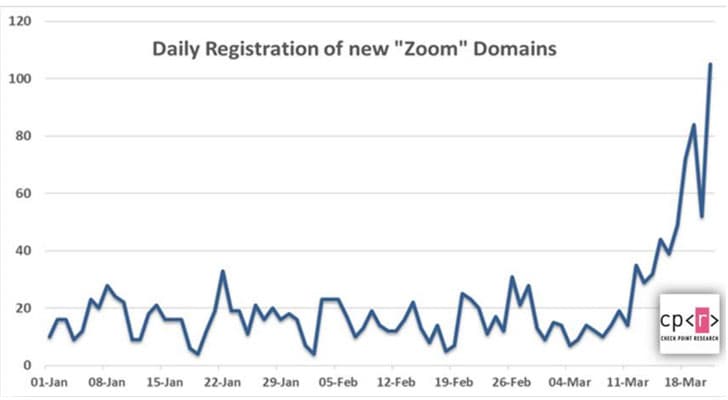
According to a report published by Check Point, experts observed a significant increase in the number of registrations for new fake “Zoom” domains and malicious “Zoom” executable files, both are evidence of malicious campaigns carried out by experts.

“During the past few weeks, we have witnessed a major increase in new domain registrations with names including “Zoom”, which is one of the most common video communication platforms used around the world.” reads the analysis published by CheckPoint.

“Since the beginning of the year, more than 1700 new domains were registered and 25% of them were registered in the past week. Out of these registered domains, 4% have been found to contain suspicious characteristics.”

Check Point researchers observed over 1,700 new “Zoom” domains that have been registered since the beginning of the Coronavirus outbreak, with 25 percent of them registered in the last week.

Experts have also detected malicious files with names such as “zoom-us-zoom_##########.exe” and “Microsoft-teams_V#mu#D_##########.exe” (# representing various digits). The file acts as a dropper for the InstallCore PUA and could potentially deliver other malicious payloads.

Check Point pointed out that crooks are also targeting other applications widely adopted during this period due to the Coronavirus epidemic, such as Google Classroom.

Threat actors registered malicious domains like googloclassroom[.]com and googieclassroom[.]com to deliver malware.

Below the recommendations published by CheckPoint:

  1. Be cautious with emails and files received from unknown senders, especially if they are offering special deals or discounts.
  2. Don’t open unknown attachments or click on links within the emails.
  3. Beware of lookalike domains, spelling errors in emails and websites, and unfamiliar email senders.
  4. Ensure you are ordering goods from an authentic source. One way to do this is NOT to click on promotional links in emails, and instead, Google your desired retailer and click the link from the Google results page.
  5. Prevent zero-day attacks with a holistic, end to end cyber architecture.
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – coronavirus, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


