
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Conti ransomware claims responsibility for the attack on Costa Rica

Conti ransomware gang claimed responsibility for a ransomware attack that hit the government infrastructure of Costa Rica. Last week a ransomware attack has crippled the government infrastructure of Costa Rica causing chaos. The Conti ransomware gang claimed responsibility for the attack, while the Costa Rican government refused to pay a ransom. “The Costa Rican state […]

Costa Rica Conti ransomware

Conti ransomware gang claimed responsibility for a ransomware attack that hit the government infrastructure of Costa Rica.

Last week a ransomware attack has crippled the government infrastructure of Costa Rica causing chaos.

The Conti ransomware gang claimed responsibility for the attack, while the Costa Rican government refused to pay a ransom.

“The Costa Rican state will not pay anything to these cybercriminals.” said Costa Rica President Carlos Alvarado.

Costa Rica Conti ransomware

The attack took place early this week, it impacted multiple government services from the Finance Ministry to the Labor Ministry.

“The initial attack forced the Finance Ministry to shut down for several hours the system responsible for the payment of a good part of the country’s public employees, which also handles government pension payments. It also has had to grant extensions for tax payments.” reads the post published by the Associated Press.

Costa Rican businesses fear that the ransomware gang could have infiltrated confidential information they provided to the government. The leak of this data could pose a serious risk to these organizations.

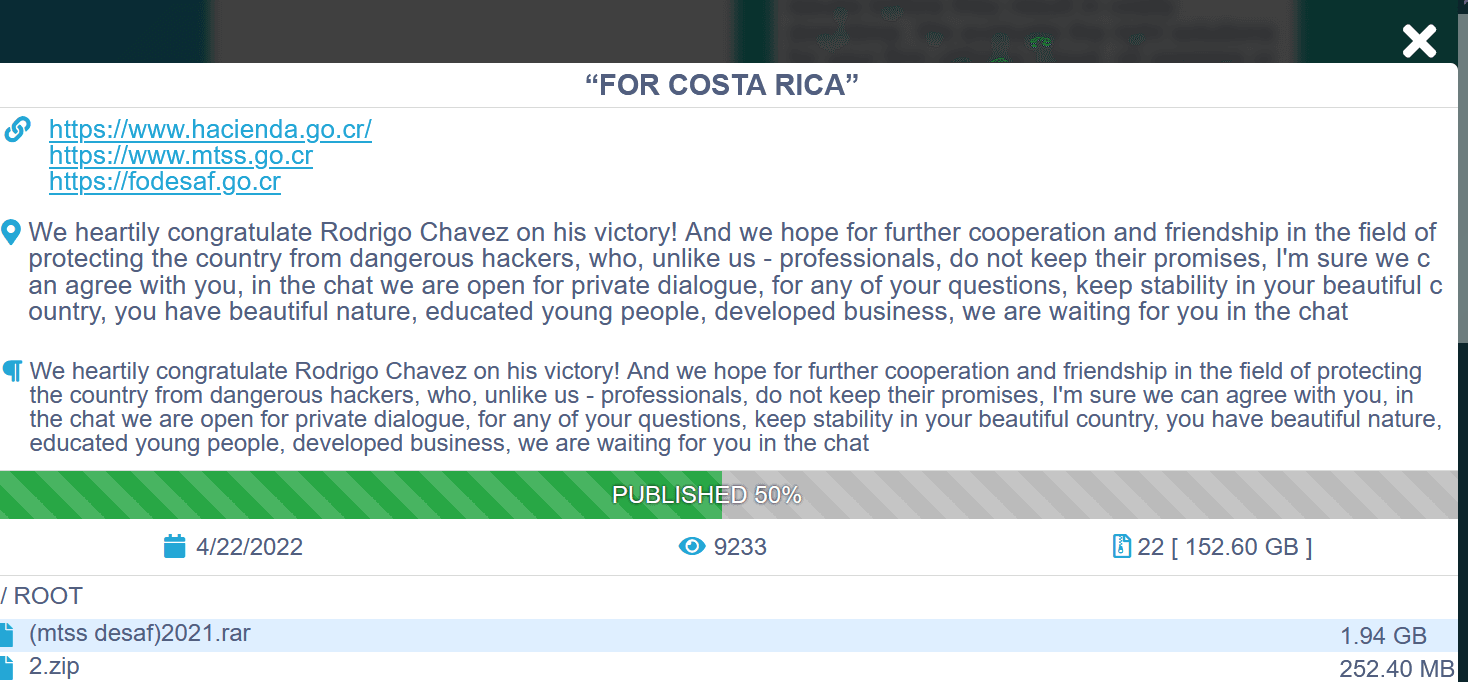
At the time of this writing, the Conti ransomware gang had published 50% of the stolen data.

It is not clear if this attack was politically motivated, while Conti ransomware gang announced its support for Russia’s invasion of Ukraine, Costa Rica publicly condemned the invasion.

“You also can’t separate it from the complex global geopolitical situation in a digitalized world,” Alvarado said.

Please vote for Security Affairs as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog” and others of your choice.
To nominate, please visit: 
https://docs.google.com/forms/d/e/1FAIpQLSfxxrxICiMZ9QM9iiPuMQIC-IoM-NpQMOsFZnJXrBQRYJGCOw/viewform  

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Costa Rica)

[adrotate banner=”5″]

[adrotate banner=”13″]


