
Experts from threat intelligence firm Cyble have found documents relating to Covid-19 vaccine of European Medicines Agency in the Darkweb
Security experts from threat intelligence firm Cyble have found several documents relating to the Covid-19 vaccine allegedly stolen from the European Medicines Agency (EMA) leaked in the Darkweb.
While the pandemic is spreading on a global scale, threat actors continue to target government organizations and entities in the pharmaceutical industry.
In early December, the European Medicines Agency (EMA) announced a cyber attack that has targeted it. The EMA did not provide technical details about the attack, nor whether it will have an impact on its operations while it is evaluating and approving COVID-19 vaccines.
“EMA has been the subject of a cyberattack. The Agency has swiftly launched a full investigation, in close cooperation with law enforcement and other relevant entities.” reads the EMA’s announcement.
“EMA cannot provide additional details whilst the investigation is ongoing. Further information will be made available in due course.”

At the time of this writing, it is not clear whether the cyber attack was successful, either when it took place. The agency confirmed to have launched an investigation into the incident.
The European agency plays a crucial role in the evaluation of COVID-19 vaccines across the EU, it has access to sensitive and confidential information, including quality, safety, and effectivity data resulting from trials.
In the last months, security experts reported the surge of the illegal market for Covid-19 vaccines on the Darkweb market.
Recently, Cyble started tracking documents being shared on one of the Russian-speaking forums. The links to the documents have been shared by a newly created profile which was used only for the alleged data leak.
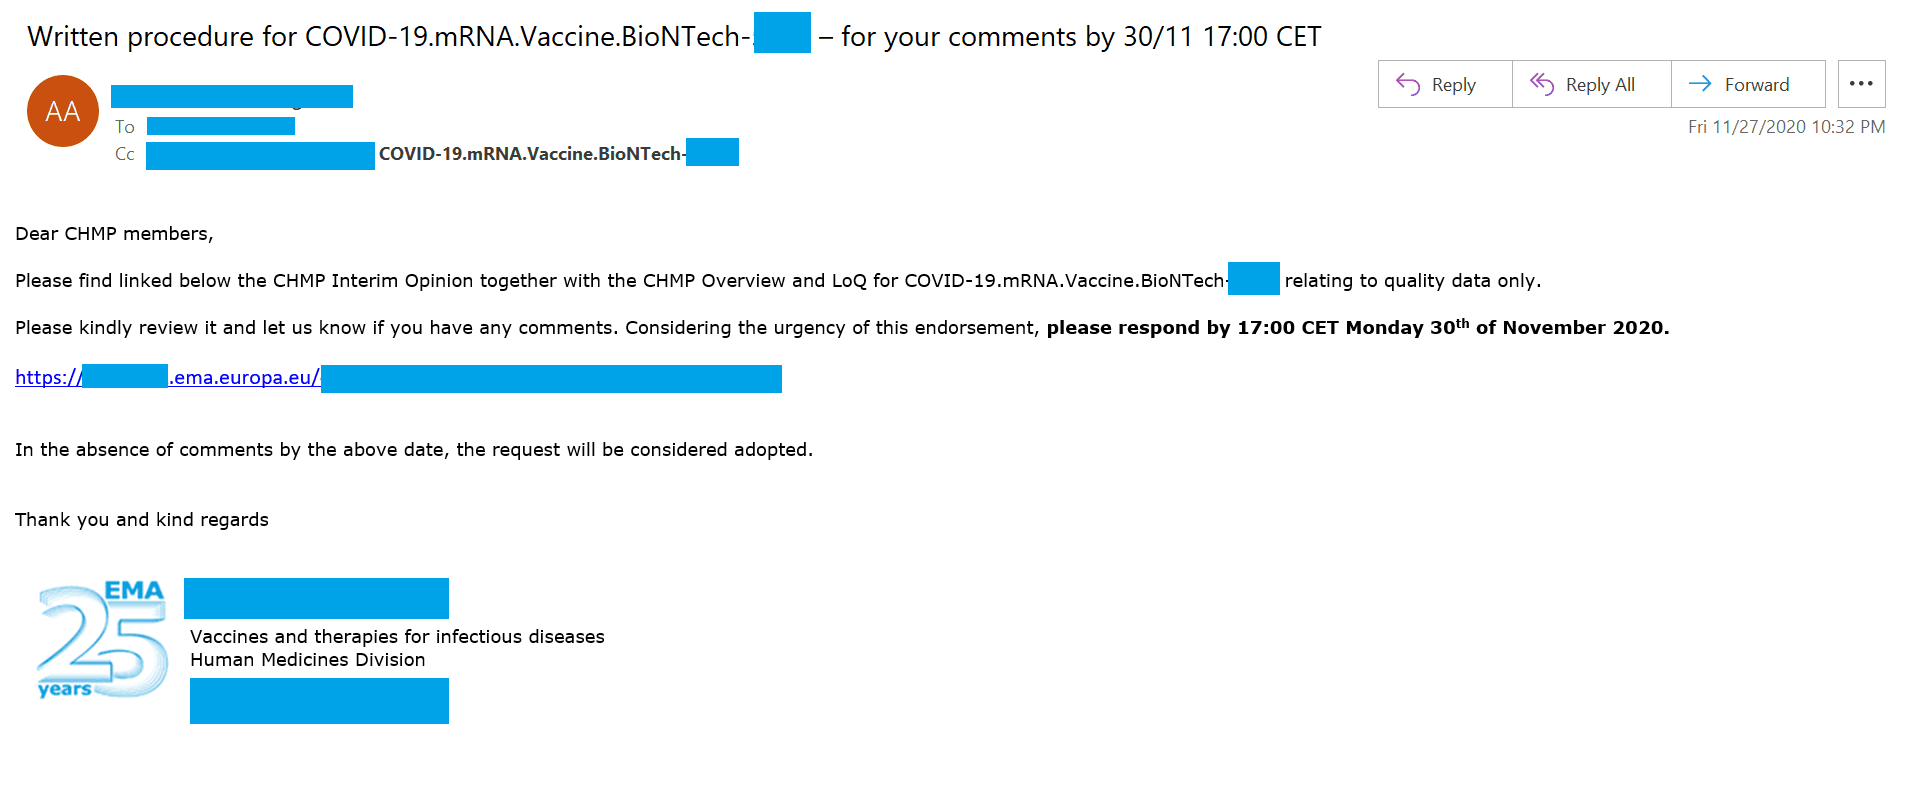
“During the assessment of data, our researchers noticed that multiple confidential files, including MoMs, assessment reports, confidential emails, login portal links and images of its internal pages were accessed and leaked.” reported the analysis published by Cyble.

The experts shared screenshots of the internal email where the portal link was shared, the login page for the portal to access the reports, and images of internal pages.

The documents also include the alleged assessment report of COVID-19 vaccine along with the summary report of drug release and stability.
Below a list of security measures that organizations can adopt to counter the impact of cyberattacks targeting the COVID-19 vaccine supply chain.
- Validating third-parties and ensuring that they have the necessary level of cyber defences
- Never clicking on unverified/unidentified links
- Refraining from opening email attachments before validating their authenticity
- Using security software and keeping it updated
- Training employees on cybersecurity through cyber literacy programs
- Periodically conducting third-party/suppliers risk assessment
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, COVID-19 vaccine)
[adrotate banner=”5″]
[adrotate banner=”13″]


