
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts observed a spike in COVID-19 related malspam emails containing GuLoader

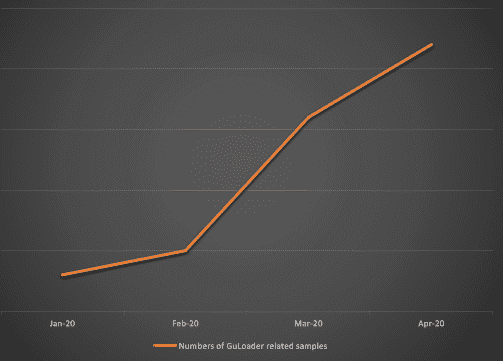
Security experts observed a spike in the use of the GuLoader since March 2020 while investigating COVID-19-themed malspam campaigns. Researchers from Vipre Labs observed a spike in the use of GuLoader in COVID-19-themed campaign since March 2020. The discovery confirms that crooks continue to use COVID-19 lures in malspam campaigns. In the campaign monitored by […]

GuLoader

Security experts observed a spike in the use of the GuLoader since March 2020 while investigating COVID-19-themed malspam campaigns.

Researchers from Vipre Labs observed a spike in the use of GuLoader in COVID-19-themed campaign since March 2020.

GuLoader

The discovery confirms that crooks continue to use COVID-19 lures in malspam campaigns. In the campaign monitored by Vipre Labs, attackers used spam email samples containing GuLoader.

The GuLoader is a popular RAT that appeared in the threat landscape in 2019 and that was involved in other COVID-19 campaigns, it is written in VB5/6 and compressed in a .rar/.iso file. 

GuLoader is usually employed in spam campaigns using bill payments, wire transfers or COVID lures.

In the last campaign observed by experts, the downloader utilizes cloud hosting services to keep the payload encrypted.

“This malware downloader utilizes cloud hosting services like Microsoft OneDrive or Google Drive to keep its payload encrypted. Also, GuLoader is used to download Remote Access Trojan (RAT) or files that allow attackers to control, monitor, or steal information on the infected machine.” reads the analysis.

The malware implements anti-analysis techniques, such as an anti-debugger. In order to achieve persistence, GuLoader creates a folder in which to place a copy of itself and modifies a registry key.

Now the loader implements process hollowing and use the child processes to download, decrypt, and map the payload into memory.

Common payloads downloaded by the loader are Formbook, NetWire, Remcos, Lokibot, and others.

The analysis published by Vipre Labs includes technical details about the threats, including Indicators of Compromise (IoCs).

In early March, experts at MalwareHunterTeam uncovered a COVID-19-themed campaign that was distributing the GuLoader malware to deliver the FormBook information-stealing Trojan.

The campaign was using emails that pretend to be sent by members of the World Health Organization (WHO).

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – COVID-19, malspam)

[adrotate banner=”5″]

[adrotate banner=”13″]


