
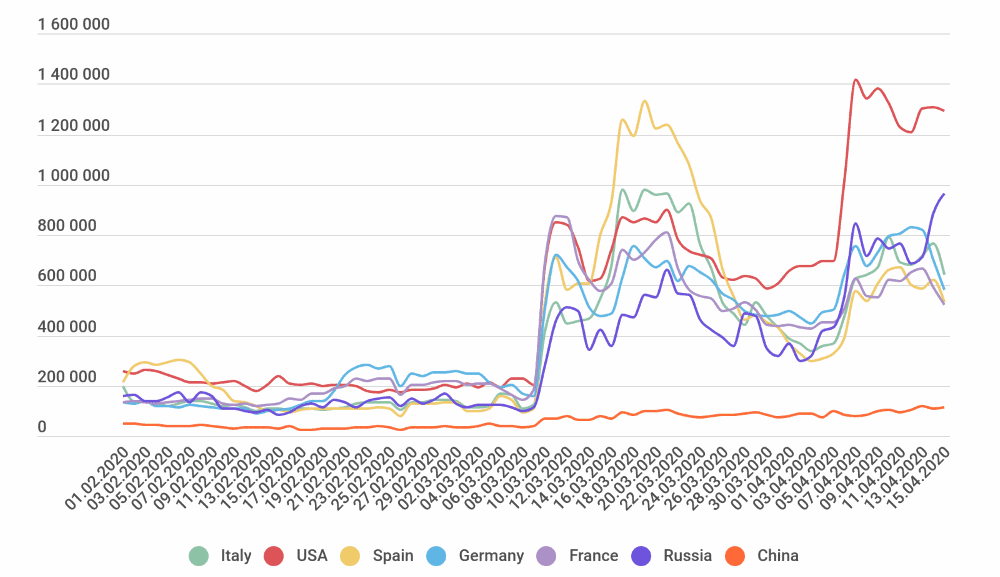
The number of RDP brute-force attacks is skyrocketing in mid-March due to remote working imposed during the COVID-19 pandemic.
Researchers from Kaspersky Lab are observing a significant increase in the number of RDP brute-force attacks since the beginning of the COVID-19 pandemic.
Earlier this month, researchers from Shodan reported a 41% increase in the number of RDP endpoints exposed online, since the beginning of the COVID-19 pandemic.
RDP brute-force attacks skyrocketed in March due to remote working imposed during the COVID-19 pandemic that forced organizations to deploy more systems online accessible through RDP connections.
“One of the most popular application-level protocols for accessing Windows workstations or servers is Microsoft’s proprietary protocol — RDP. The lockdown has seen the appearance of a great many computers and servers able to be connected remotely, and right now we are witnessing an increase in cybercriminal activity with a view to exploiting the situation to attack corporate resources that have now been made available (sometimes in a hurry) to remote workers.” reads the post published by Kaspersky.
“Since the beginning of March, the number of Bruteforce.Generic.RDP attacks has rocketed across almost the entire planet”

Attackers attempt to brute-force the username and password used to protect RDP access to systems exposed online, they can use combinations of random characters or leverage dictionary of most popular passwords.
Kaspersky recommends organizations to adopt the following security measures:
- At the very least, use strong passwords.
- Make RDP available only through a corporate VPN.
- Use Network Level Authentication (NLA).
- If possible, enable two-factor authentication.
- If you don’t use RDP, disable it and close port 3389.
- Use a reliable security solution.
Experts also warn of vulnerabilities in other remote working tools, such as VNC, that could expose organizations to hack. In November, Kaspersky experts reported dozens of flaws in Linux and Windows VNC clients in
At the time, querying shodan.io Kaspersky find over 600,000 VNC servers available online.

Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – RDP, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


