
Cracka hackers who took over the personal email account of CIA Director John Brennan have now doxed more than 2000 Government employees.
The young hackers of the crew known as Crackas With Attitude (CWA) announced that they have doxed more than 2,000 Government employees.
The hackers are the same that accessed into the AOL email account of the CIA director and violated the email account of the FBI Deputy Director’s wife.
Now the hackers claim to have broken into government computers, on Thursday the official account of the Cracka group published a list of more than 2,000 names, phone numbers and email addresses of law enforcement and military personnel.

Cracka claimed to have broken into government systems and leaked the data belonging to government employees in support of Palestine
“Maybe the USgov should listen to us, I mean, we have enough information to make them look like the little bitches they are,” Cracka said in a tweet.

How did Cracka obtain the information?
Members of the group explained to Motherboard that they took over the account of an internal employee, then they got access to several “tools feds use” such as the JABS, a database containing information on the arrested people, the IC3, that is crime-reporting tool used by the FBI, and VCC, a sharing tool for law enforcement agencies.

Wired reported that hackers exploited a flaw to gain access to the private portal.
“The CWA hackers said they found a vulnerability that allowed them to gain access to the private portal, which is supposed to be available only to the FBI and other law enforcement agencies around the country. That portal in turn, they say, gave them access to more than a dozen law enforcement tools that are used for information sharing.” states Wired.
Cracka doesn’t provide information on the hacked account, it is clear that the employee is “high in the [government].” The hacker confirmed that they didn’t download all the data available.
“We let the [government] off by a lot, this could be so damaging it could affect the whole of USA by ALOT,” the hacker explained via online chat.
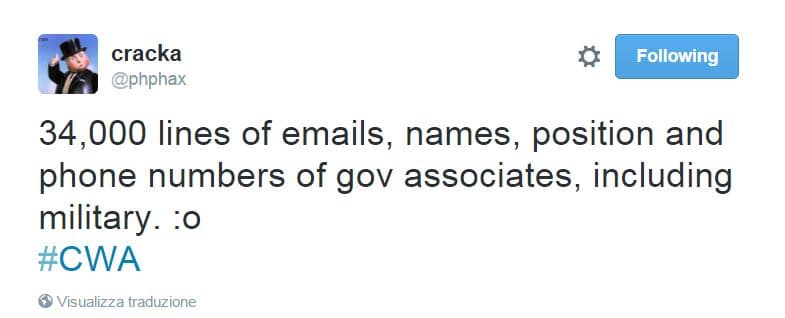
Cracka also published a tweet claiming to have stolen also “34,000 lines of emails, names, position and phone numbers of gov associates, including military.”
As correctly highlighted by Cracka, this kind of data breach could have serious consequence for the Homeland Security. The personal information belonging to government entities could be used by foreign state-sponsored hackers in cyber espionage operations.
“Just to clear this up, CWA did, indeed, have access to everybody in USA’s private information, now imagine if we was [sic] Russia or China,” he said in another tweet.

Journalists at Motherboard confirmed that at least five random numbers in the list they analyzed are legitimate.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Cracka, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


