
The newfound critical vulnerability on Twitter seems to allow remote code execution! Which is the reason behind the recent Twitter security issues?
The newfound critical vulnerability on Twitter seems to allow remote code execution!
The last days we have seen some cases that have to do with Twitter’s security making us wonder if the famous social network needs further security attention. A recent case is the hack of the Twitter account of Facebook’s founder Mark Zuckerberg, while at the same moment it’s really easy for someone to buy databases with Twitter account credentials on Darknet for the amount of 10 Bitcoins.
IT Security researchers, as well as the media, rushed to scream that the recent hacking didn’t have to do with Twitter’s infrastructure, but with some state-of-the art malware which could steal usernames and passwords. But what is the exact truth?
Not more than one day ago, a user on Hackerone, one of the biggest platforms where security researchers find vulnerabilities on websites and applications, known as a bug bounty platform, received from Twitter a huge price for a vulnerability that he found.
The user, known as filedescriptor on Hackerone, received the amount of 15,120$ for his achievement. We believe that Twitter didn’t want to disclose any further details about the case, and as we can see from the payment, the details cannot be seen, as well as the title of the vulnerability!

If someone sees Twitter’s praises regarding vulnerability disclosure on Hackerone platform, it is clear that the given amount has to do with a vulnerability that allows remote code execution which affects Core Twitter. You can see more details bellow:

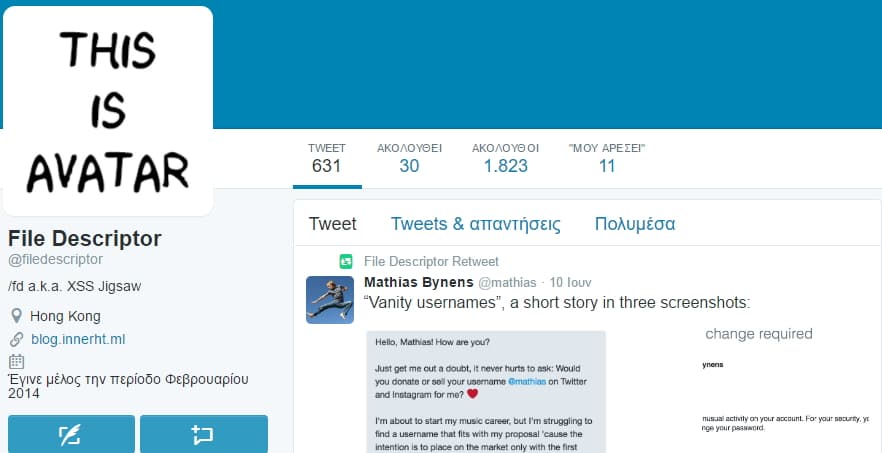
The user filedescriptor is from Hong Kong and well known as one the best bug bounty hunters worldwide. His record regarding numerous critical vulnerabilities for companies like Twitter, puts him on top of the list as one of the best ethical hackers worldwide.
You can see some of his achievements here.


Until Twitter will not give as a straight forward answer by confirming this case, we won’t be able to be 100% sure about the nature of the vulnerability that filedescriptor found and of course his proof of concept. All the evidences that we found, indicate that a serious vulnerability existed on Twitter until one day before, which was patched probably after filedescriptor’s disclosure.
We strongly recommend all Twitter users to immediately change their passwords and to activate Twitter’s two factor authentication in order to enhance their security.
What happens though if this specific vulnerability was found previously also from malicious users? What if the latest incidents of Twitter’s leakages had to do with this exact vulnerability which was patched only one day before?
We are still waiting for an official answer from Twitter.
Secnews has also its own bug bounty program on Hackerone platform. Please read the terms and conditions for our bug bounty program too. We are waiting for your reports!
You can login and check the security of our website here: https://hackerone.com/secnews
 Written by: Konstantinos Vavousis – Editor in Chief, SecNews
SecNews is the top specialized IT security collective website in Greece & Cyprus, that informs its visitors about the latest threats and hacking techniques. The reader is able to obtain zero-day information from the IT Security field and also exchange opinions, upload comments, even post its own articles. Being collective, anyone from hackers to IT Security experts have the ability to post articles, after being checked from the editors. The SecNews hacker-friendly approach, gives the opportunity to most of the hackers to post their achievements in the web site with details, mostly events that happened in Greece but also abroad. SecNews is one of the most trusted reference media sites for IT Security experts in Greece, working in organizations,banks and companies.
[adrotate banner=”9″]
(Security Affairs – Twitter, hacking)


