
Grandoreiro Banking Trojan resurfaces, targeting users in Latin America and Europe in new phishing campaigns.
Forcepoint X-Labs researchers warn of new phishing campaigns targeting Latin America and Europe in new phishing campaigns. The Trojan has been active since 2016, it initially targeted Brazil but expanded to Mexico, Portugal, and Spain since 2020.
Grandoreiro is a modular backdoor that supports the following capabilities:
- Keylogging
- Auto-Updation for newer versions and modules
- Web-Injects and restricting access to specific websites
- Command execution
- Manipulating windows
- Guiding the victim’s browser to a certain URL
- C2 Domain Generation via DGA (Domain Generation Algorithm)
- Imitating mouse and keyboard movements
Forcepoint states that the large-scale phishing campaigns use VPS hosting and obfuscation to evade detection.
The cybersecurity firm uncovered a Grandoreiro campaign targeting users in Mexico, Argentina, and Spain via phishing emails impersonating tax agencies. Attackers use Contabo-hosted links to deliver obfuscated Visual Basic scripts and disguised EXE payloads for credential theft. Attackers also employ encrypted or password-protected files to evade security detection.

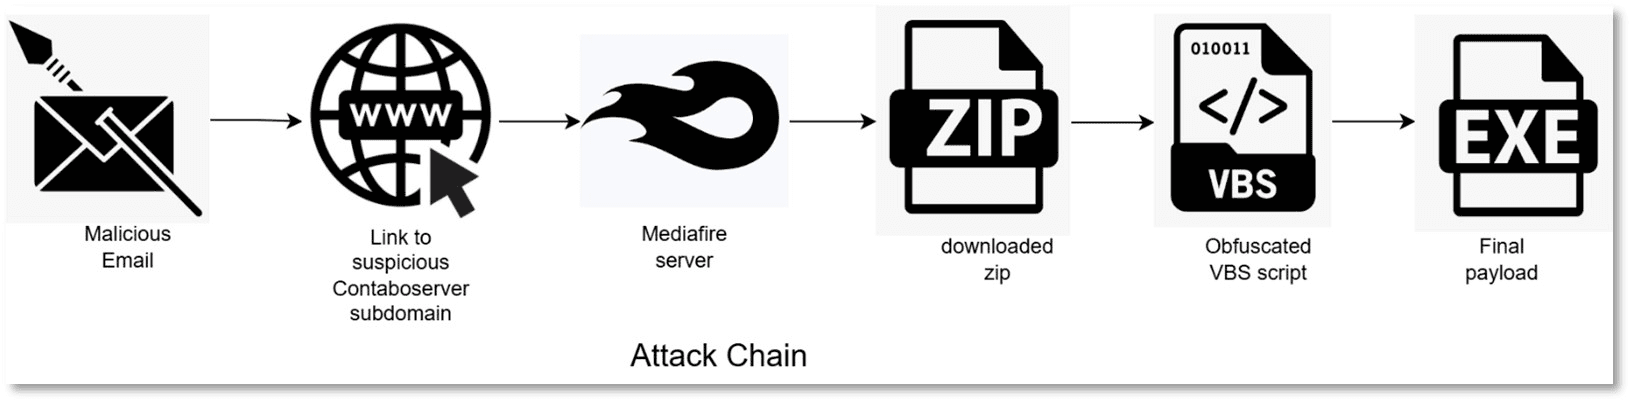
The phishing email contains malicious links that redirect users to VPS or dedicated servers hosted on Contabo, with subdomains like vmi\d{7}[.]contaboserver[.]net. Clicking the “Download PDF” button leads to a zip payload from MediaFire. These subdomains change with each campaign, linked to specific virtual machines or servers on Contabo’s network.
Clicking the “Download PDF” button triggers a JavaScript function that checks the browser and platform, then retrieves a Mediafire URL from a PHP file to download a .zip file. The .zip often contains a password-protected, obfuscated VBS script. This script decodes a base64 stream, drops an EXE file in the system directory, and executes it using Wscript.shell.
The extracted 32-bit EXE file is compiled with Delphi, it masquerades as a PDF and triggers an Acrobat Reader error. Upon user interaction, it connects to a C2 server (18.212.216.95) and searches for personal data, including Bitcoin files, system GUID, computer name, and language settings. The malware uses a custom URI Client and unusual port numbers to communicate with the server.
“The attack involves malicious ZIP files containing obfuscated VBS scripts that drop a Delphi-based EXE. Once executed, the malware steals credentials, searches for Bitcoin wallet directories connects to a C2 server, Attackers frequently change subdomains under contaboserver[.]net to evade detection.” concludes the report that includes Indicators of compromise (IoCs).
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


