
Several US universities and colleges were targeted in phishing attacks aimed at delivering malware previously used by China-linked APT groups.
Faculty and students at several U.S. universities and colleges were targeted in phishing attacks, threat actors attempted to infect the victims’ systems with a remote access Trojan (RAT) previously used by Chinese state-sponsored hackers.
The malicious code employed in the attacks is the Hupigon RAT, a RAT previously spotted in campaigns carried out by China-linked APTs such as APT3 (aka TG-0100, Buckeye, Gothic Panda, and UPS).
Hupigon is a remote access Trojan (RAT) that has been active since at least 2006, it was first detected by FireEye in 2010.
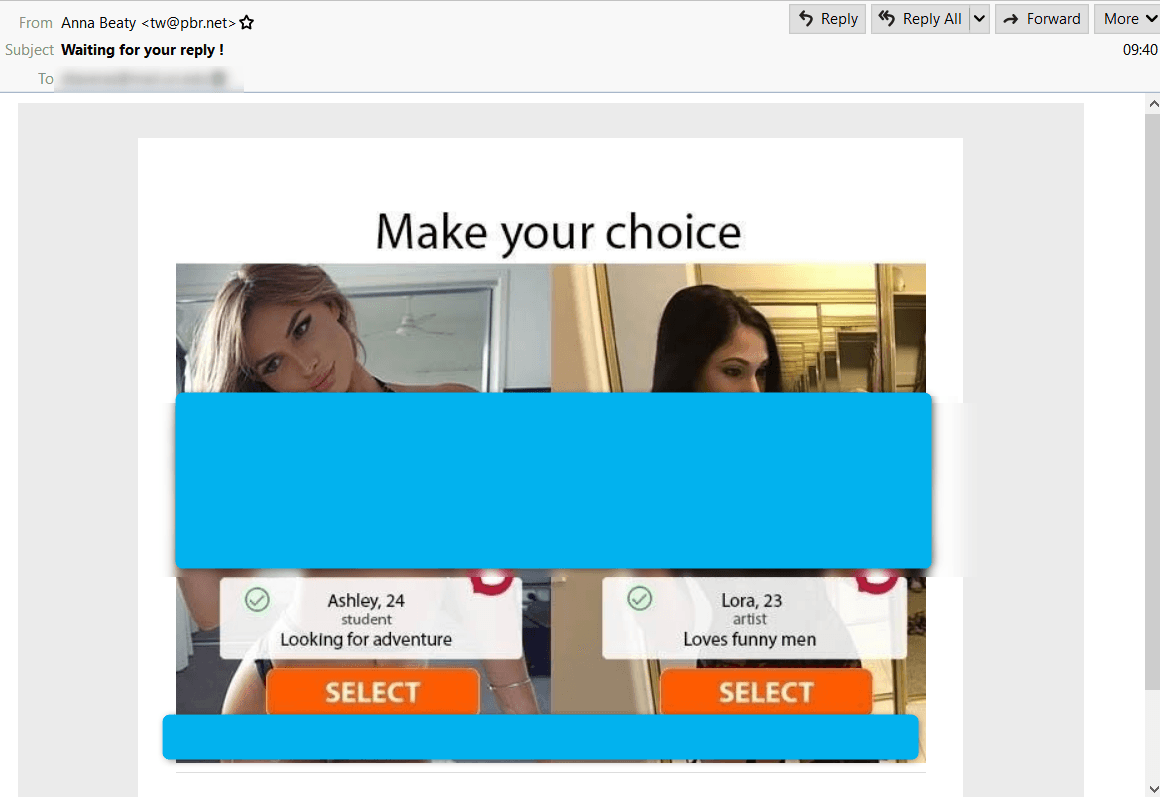
The campaign targeting the US universities uses adult dating lures.
“Messages arrive obfuscated as adult dating lures requesting the user to choose between one of two pictures to connect with by clicking the link under their picture,” reads the analysis published by Proofpoint.

Once the victim has clicked on one of the two links in the content of the message, the infection chain will start by downloading an executable used as a dropper for the Hupigon RAT.
The malware allows the attacker to take full control of the infected system, it could be used to steal sensitive personal information, to take screenshots, and audio recordings, and to control the webcam.
Most of the messages associated with this phishing campaign were observed between April 14 and April 15, Proofpoint researchers observed roughly 80,000 messages, coinciding with an observed rotation in payload.
Researchers believe this campaign is financially motivated, this opinion is based on the distribution methods and message volumes.
‘This campaign delivered over 150,000 messages to over 60 different industries, with 45% focused on education, colleges, and universities,” Proofpoint concluded.
“These attacks demonstrate the inverse relationship of commoditized RATs incorporated into criminal and state-sponsored campaigns over time. In this case, cybercriminals repurposed an attack tool leveraged by state-sponsored threat actors among other. In this particular case, this is a general crimeware-based campaign.”
Additional technical details were reported in the analysis published by Proofpoint, including indicators of compromise (IOCs).

Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – US universities, phishing)
[adrotate banner=”5″]
[adrotate banner=”13″]


