
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

How to hack Google FR by exploiting a cross-site scripting flaw

The security expert Issam Rabhi (@issam_rabhi) has discovered a cross-site scripting vulnerability in Google France. The giant already fixed it. A security expert from French security outfit Sysdream, Issam Rabhi (@issam_rabhi), discovered a cross-site scripting vulnerability in Google France. Yes, you‘ve got it right, the website of the IT giant was affected by one of the […]

How to hack Google FR by exploiting a cross-site scripting flaw

The security expert Issam Rabhi (@issam_rabhi) has discovered a cross-site scripting vulnerability in Google France. The giant already fixed it.

A security expert from French security outfit Sysdream, Issam Rabhi (@issam_rabhi), discovered a cross-site scripting vulnerability in Google France. Yes, you‘ve got it right, the website of the IT giant was affected by one of the most common vulnerabilities. According to the OWASP Top Ten, the cross-site scripting is the third most popular issue affecting web applications.
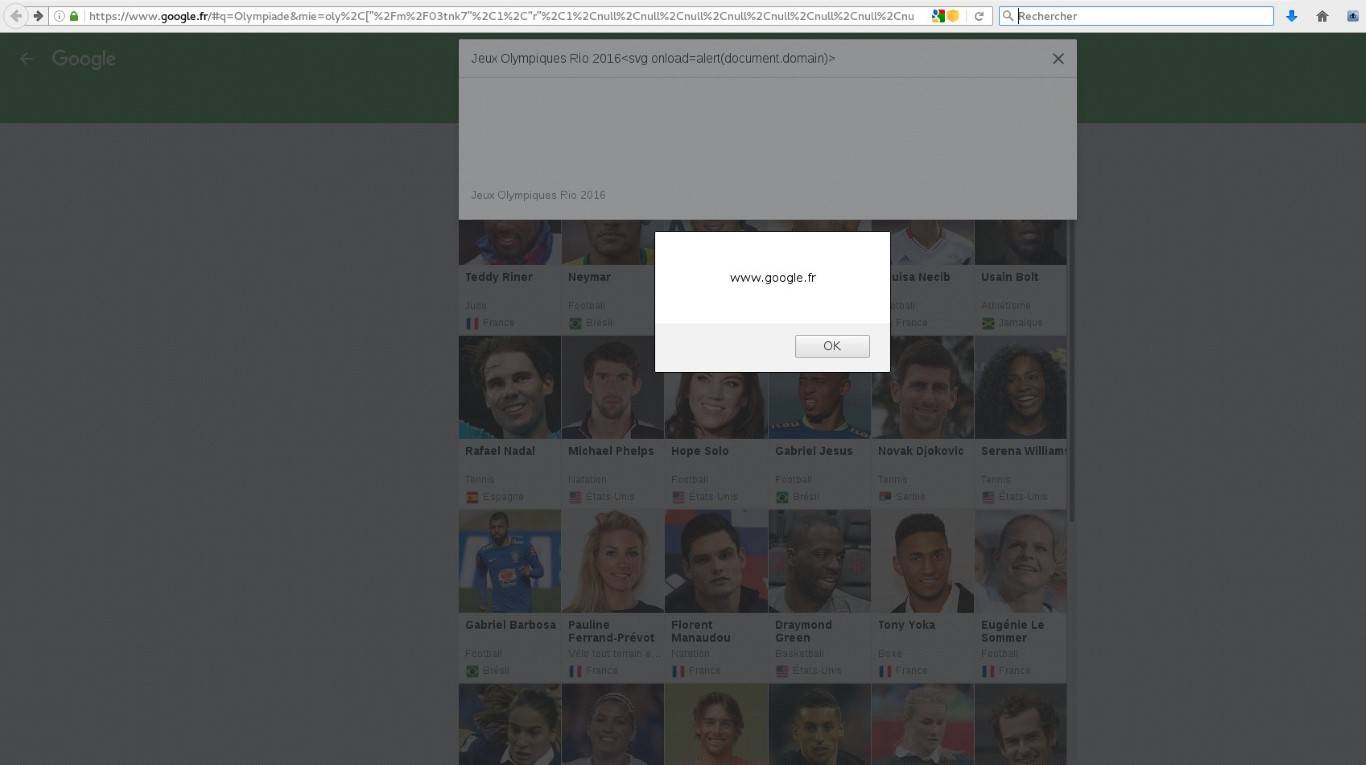
cross-site scripting Google FR

Such kind of flaw could be exploited by a malicious attacker for various attacks, including defacements and traffic hijacking.

“XSS flaws occur whenever an application takes untrusted data and sends it to a web browser without proper validation or escaping. XSS allows attackers to execute scripts in the victim’s browser which can hijack user sessions, deface web sites, or redirect the user to malicious sites.” reads the description provided by the OWASP TOP 10.

The experts reported the cross-site scripting vulnerability to Google on August 5th and the experts of the company fixed the vulnerability in just four days.

Rabhi published a Proof-of-concept for the attack on his website, below the exploitation step by step:

  1. First we need to click the link below using Firefox browser:
https://www.google.fr/#q=Olympiade&mie=oly%2C%5B%22%2Fm%2F03tnk7%22%2C1%2C%22r%22%2C1%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2Cnull%2C0%5D
  1. Then, to insert the following payload in the input field related to search:
<svg onload=alert(document.domain)>

Finally, the alert message box will pop up on the screen.

The expert did not submit the bug under the Google bug bounty program, anyway he received kudos from his colleagues.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – cross-site scripting, hacking)


