Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CrushFTP CVE-2025-2825 flaw actively exploited in the wild

Attackers exploit CrushFTP CVE-2025-2825 flaw, enabling unauthenticated access to unpatched devices using public proof-of-concept code. Threat actors are exploiting a critical authentication bypass vulnerability, tracked as CVE-2025-2825, in the CrushFTP file transfer software. Attackers are using exploits based on publicly available proof-of-concept exploit code. The vulnerability impacts CrushFTP versions 10.0.0 through 10.8.3 and 11.0.0, it […]

CrushFTP CVE-2025-54309

Attackers exploit CrushFTP CVE-2025-2825 flaw, enabling unauthenticated access to unpatched devices using public proof-of-concept code.

Threat actors are exploiting a critical authentication bypass vulnerability, tracked as CVE-2025-2825, in the CrushFTP file transfer software. Attackers are using exploits based on publicly available proof-of-concept exploit code.

The vulnerability impacts CrushFTP versions 10.0.0 through 10.8.3 and 11.0.0, it may result in unauthenticated access. Remote and unauthenticated HTTP requests to CrushFTP may allow attackers to gain unauthorized access.

The file transfer software maker CrushFTP urge customers to take immediate action to address the vulnerability. Admins unable to update their installs should enable the DMZ perimeter network as a temporary security measure.

Researchers at Shadowserver warned that threat actors are attempting to exploit the vulnerability in the wild, they found approximately 1,800 vulnerable instances exposed online, mainly (904) in the US.

An update provided by Shadowserer on March 30, 2025, reports that more than 1500 vulnerable instances are exposed online.

“We are observing CrushFTP CVE-2025-2825 exploitation attempts based on publicly available PoC exploit code. You can track attempts on our Dashboard at dashboard.shadowserver.org/statistics/h… Still 1512 unpatched instances vulnerable to CVE-2025-2825.” reads the update.

Your sentence is already well-structured, but here’s a slight refinement for clarity and flow:

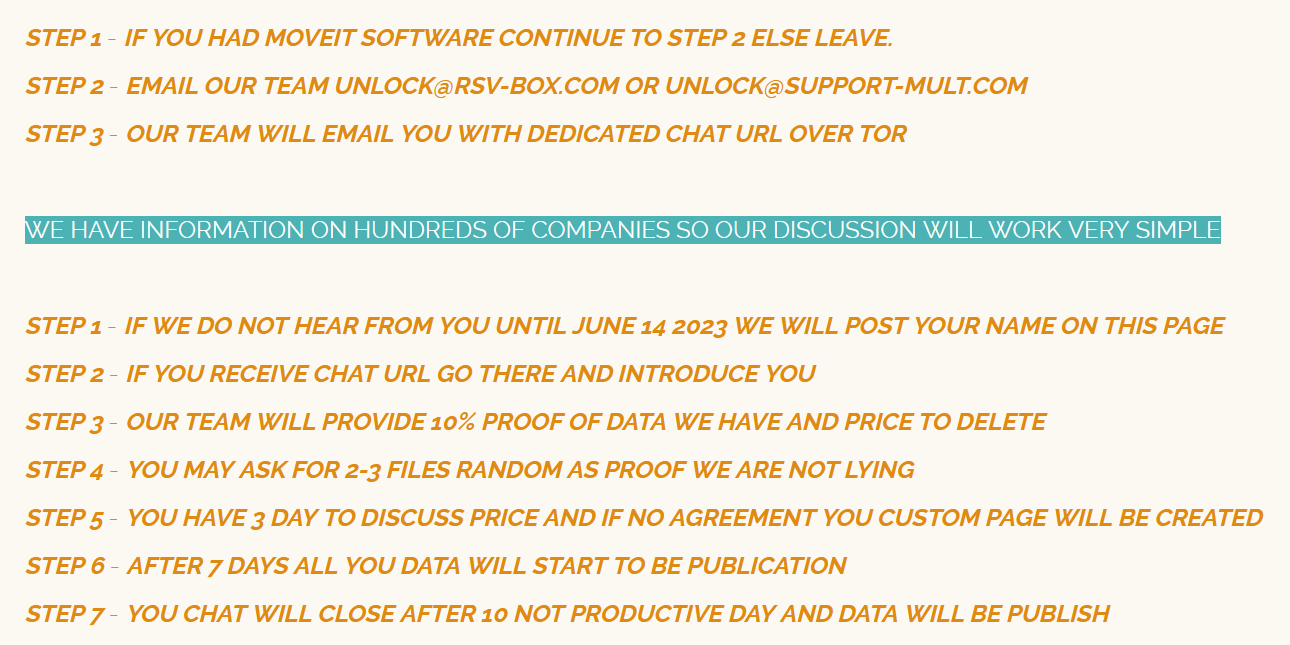
Threat actors, including the ransomware group Cl0p, are known for attacking file transfer software such as Accellion FTA, MOVEit Transfer, GoAnywhere MFT, and Cleo.

In January, the Clop ransomware group added 59 new companies to its leak site, the gang claimed to have breached them by exploiting a vulnerability ​​in Cleo file transfer products. 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CrushFTP)