
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Data of over a million users of the crypto exchange GokuMarket exposed

GokuMarket, a centralized crypto exchange owned by ByteX, left an open instance, revealing the details of virtually all of its users, the Cybernews research team has discovered. The leak comes after the team discovered an unprotected MongoDB instance, which stored information on GokuMarket crypto exchange users. Businesses employ MongoDB to organize and store large swaths […]

GokuMarket

GokuMarket, a centralized crypto exchange owned by ByteX, left an open instance, revealing the details of virtually all of its users, the Cybernews research team has discovered.

The leak comes after the team discovered an unprotected MongoDB instance, which stored information on GokuMarket crypto exchange users.

Businesses employ MongoDB to organize and store large swaths of document-oriented information, and in GokuMarket’s case, the details of over a million customers and admin users.

GokuMarket, a cryptocurrency exchange, was recently acquired by Canada-based crypto exchange ByteX. The move came after GokuMarket, which had around a million users at the time, almost went bankrupt after denying users a withdrawal option in mid-2022, a disastrous year for crypto.

GokuMarket’s exposed database was discovered in October 2023 and secured the next day after researchers sent a responsible disclosure note.

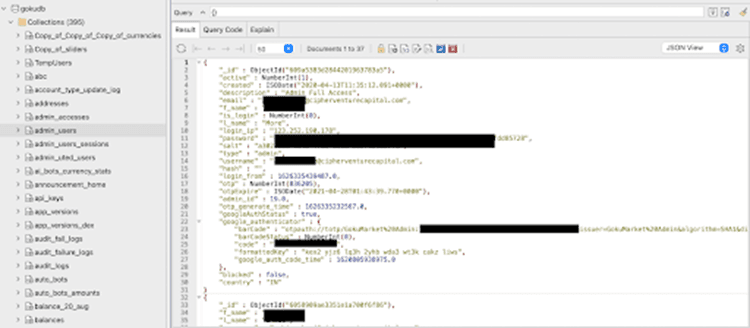
However, the database was exposed to the web for some time, which means anyone could have accessed it. Meanwhile, the open instance held a trove of sensitive data on over a million users. The data included:

  • User IP
  • Country
  • Email addresses
  • Encrypted passwords
  • User crypto wallet addresses
  • Dates of birth
  • First and last names
  • Mobile numbers
GokuMarket

The researchers believe that there’s more than enough information for a persistent attacker to develop a spear-phishing campaign, which would likely aim to drain the user’s crypto funds.

Additionally, the team discovered that the database held 35 accounts with full-admin access, including private Telegram channel IDs, exchange platform secret tokens, passwords, and other extremely sensitive information.

While individual user data may be exploited to target exposed users on other platforms through credential stuffing attacks, admin access details open up far nastier cans of worms, with attackers gaining the ability to scam en-masse, with the risk of unauthorized fund transfer.

Do you want to know more about the impact of this data leak? Take a look at the original post:

https://cybernews.com/security/gokumarket-user-data-leak/

About the author: Vilius Petkauskas, Deputy Editor at @CyberNews

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, GokuMarket)


