
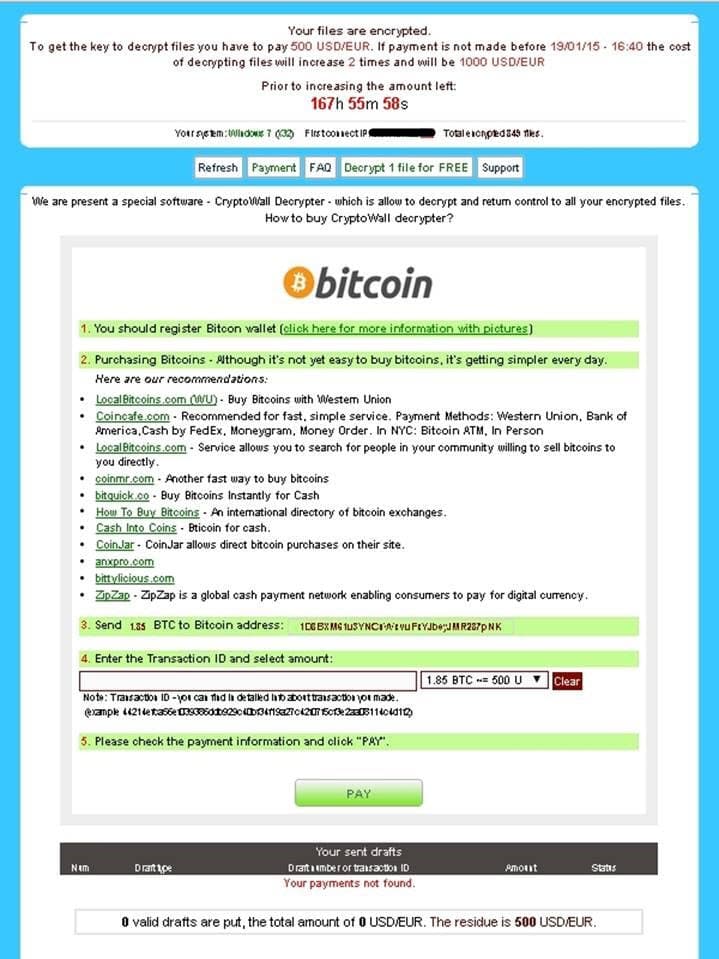
Security Experts at Microsoft discovered a new variant of CryptoWall 3.0 ransomware that adopts I2P Anonymity Network for C&C Communications.
A new version of CryptoWall ransomware has been detected in the wild by experts at Microsoft, just a week after I reported that Cisco’s Talos Security Intelligence and Research Group detected a new strain of the same malware that exploits the Tor network. In the analysis published by the Cisco team is reports that the new variant of CryptoWall is able to distinguish between 32- and 64-bit architectures and to execute different versions for each.
The new variant of CryptoWall ransomware, like others, is distributed via malicious email and through malvertising campaigns.
The experts that detected the new variant of CryptoWall, also known as CryptoWall 3.0 or Win32/Crowti, explained that it is very similar to previous strains of the same ransomware, including the recently added support of Tor network to hide C&C infrastructure.
However the experts noted that the names of the files containing the ransom demand have been changed to “HELP_DECRYPT.”
The malware customizes files for each victim by providing a personal link to a page that includes instructions. The instruction page is still reached through the Tor network.
The victims of the Cryptowall 3.0 are given 7 days to pay $500 in Bitcoins if they want to decrypt their documents, but if they don’t pay in 7 days the ransom increases to $1,000.
On January 12, Microsoft identified 288 unique Cryptowall ver. 3.0 infections .
“The graph below shows the spike after two days of no activity from 288 unique machines affected by this malware” reads the post published Microsoft.

The French researcher Kafeine who analyzed CryptoWall 3.0, reported that the communications to C&C served are encoded with the RC4 cipher.
Another feature implemented in the last variant of the malware is the support of I2P (Invisible Internet Project) for C&C communications.
“It seems communication with the C&C are Rc4 encoded (key seems to be alphanum sorted path of the POST ) and using i2p protocol” said Kafeine.
I2P is another anonymizing network used to hide the location of the control servers and make the botnet resilient the C&C to the law enforcement.
Recently also a new version of the popular black market Silk Road, the Silk Road Reloaded, migrated on I2P, probably because in this moment there is the conviction that it is more secure of Tor.
According to Kafeine, CryptoWall 3.0 is the first CryptoWall variant that uses I2P. The researcher told SecurityWeek that the malware developers seem to be chaining Tor and I2P for the file decryption services.
Stay tuned for further information
(Security Affairs – CryptoWall, malware)


