Security Affairs
CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CVE-2016-6374 – Don’t waste time, patch your CISCO Cloud Services Platform

Cisco has issued a security patch to address a remote hijacking vulnerability, tracked as CVE-2016-6374, in the Cloud Services Platform (CSP). This patch is very important, CISCO urges all customers who run CSP 2100 software to install the 2.1.0 update that addresses a “high” risk remote code execution flaw. The CISCO Cloud Services Platform (CSP) is […]

CVE-2016-6374 – Don’t waste time, patch your CISCO Cloud Services Platform

Cisco has issued a security patch to address a remote hijacking vulnerability, tracked as CVE-2016-6374, in the Cloud Services Platform (CSP).

This patch is very important, CISCO urges all customers who run CSP 2100 software to install the 2.1.0 update that addresses a “high” risk remote code execution flaw.

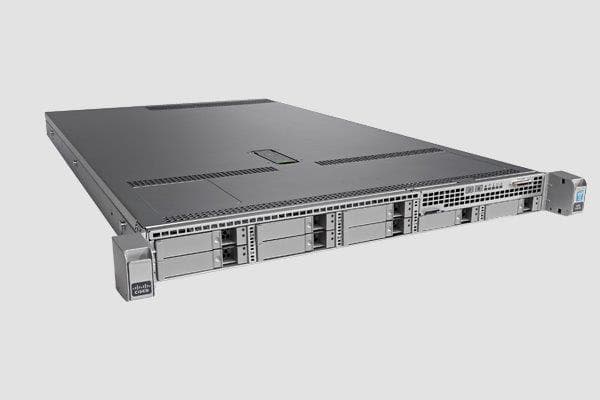
The CISCO Cloud Services Platform (CSP) is a product designed to manage virtualized network services and components, it runs as a Linux x86 virtual machine built into a Cisco network appliance.

cisco-cloud-services-platform-2100

The Cisco Cloud Services Platform 2100 allows to quickly deploy any Cisco or third-party network virtual service through a simple, built-in, native web user interface (WebUI), command-line interface (CLI), or representational state transfer (REST) API.

“A vulnerability in the web interface of Cisco Cloud Services Platform (CSP) 2100 could allow an unauthenticated, remote attacker to execute arbitrary code on a targeted system.” reads the security advisory published by CISCO.

According to CISCO, the exploitation of the CVE-2016-6374 flaw is simple, attackers just need to send malformed HTTP requests to achieve remote code execution. An unauthenticated attacker has to use a malicious DNS-lookup request through the CSP web interface in order to execute commands on the server.

“The vulnerability is due to insufficient sanitization of specific values received as part of a user-supplied HTTP request. An attacker could exploit this vulnerability by sending a malicious dnslookuprequest to the affected system. An exploit could allow the attacker to execute arbitrary code with the privileges of the user.”

The Cisco Product Security Incident Response Team (PSIRT) confirmed that its experts are not aware of any public announcements or malicious use of the CVE-2016-6374 vulnerability in the wild.

Cisco customers have no choice due to the absence of mitigations for the CVE-2016-6374 flaw, they need urgently to apply the patch.

A few days ago CISCO issued another patch for a high-severity vulnerability in the IOS platform that was discovered while analyzing the exploits included in the Equation Group data leak.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Cloud Services Platform, CVE-2016-6374)