
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers are exploiting the CVE-2018-0101 CISCO ASA flaw in attacks in the wild

Hackers are exploiting the CVE-2018-0101 CISCO ASA flaw in attacks in the wild and a Proof-of-concept exploit code is available online. This week, Cisco has rolled out new security patches for a critical vulnerability, tracked as CVE-2018-0101, in its CISCO ASA (Adaptive Security Appliance) software. This is the second the tech giant issued a security patch to fix the […]

CISCO ASA

Hackers are exploiting the CVE-2018-0101 CISCO ASA flaw in attacks in the wild and a Proof-of-concept exploit code is available online.

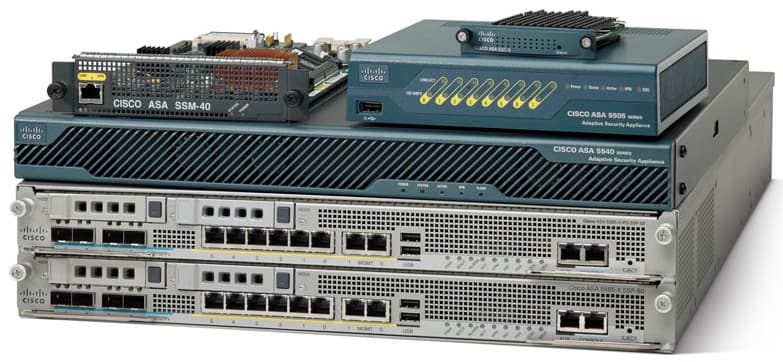
This week, Cisco has rolled out new security patches for a critical vulnerability, tracked as CVE-2018-0101, in its CISCO ASA (Adaptive Security Appliance) software.

This is the second the tech giant issued a security patch to fix the critical vulnerability in CISCO ASA, the first one released in January. The vulnerability could be exploited by a remote and unauthenticated attacker to execute arbitrary code or trigger a denial-of-service (DoS) condition causing the reload of the system.

The affected models are:

  • 3000 Series Industrial Security Appliance (ISA)
  • ASA 5500 Series Adaptive Security Appliances
  • ASA 5500-X Series Next-Generation Firewalls
  • ASA Services Module for Cisco Catalyst 6500 Series Switches and Cisco 7600 Series Routers
  • ASA 1000V Cloud Firewall
  • Adaptive Security Virtual Appliance (ASAv)
  • Firepower 2100 Series Security Appliance
  • Firepower 4110 Security Appliance
  • Firepower 9300 ASA Security Module
  • Firepower Threat Defense Software (FTD)

Now the company confirmed that attackers are trying to exploit the vulnerability CVE-2018-0101 in attacks in the wild.

“The Cisco Product Security Incident Response Team (PSIRT) is aware of public knowledge of the vulnerability that is described in this advisory,” reads the security advisory published by CISCO. the update states. “Cisco PSIRT is aware of attempted malicious use of the vulnerability described in this advisory.”

The vulnerability was discovered by Cedric Halbronn and received a CVSS base score of 10.0, the highest one.

This week Halbronn presented its findings at the REcon conference in Brussels, in its speech titled ‘Robin Hood vs CISCO ASA Anyconnect.’ he highlighted that the vulnerability could be present up to seven years old because the AnyConnect Host Scan is available since 2011.

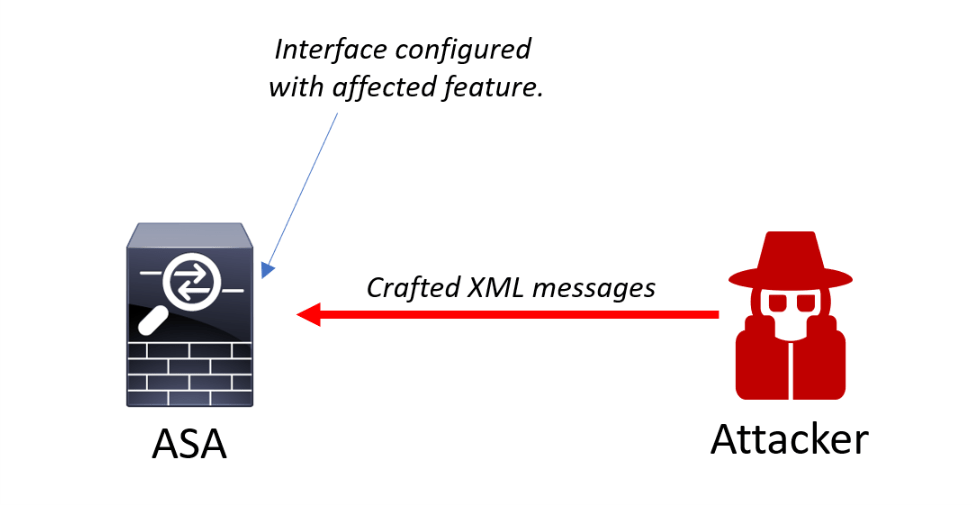
The new attack scenario covered with the new update sees an attacker exploiting the vulnerability by sending specially crafted XML packets to a webvpn-configured interface.
CISCO ASA attack

A “Cisco ASA CVE-2018-0101 Crash PoC” was already published by some users on Pastebin.

[adrotate banner=”9″] [adrotate banner=”12″]  

Pierluigi Paganini

(Security Affairs – CISCO ASA, CVE-2018-0101)

[adrotate banner=”5″]

[adrotate banner=”13″]


