
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Docker runc flaw opens the door to a ‘Doomsday scenario’

Security experts found a serious flaw tracked CVE-2019-5736 affecting runc, the default container runtime for Docker, containerd, Podman, and CRI-O. Aleksa Sarai, a senior software engineer at SUSE Linux GmbH, has disclosed a serious vulnerability tracked CVE-2019-5736 affecting runc, the default container runtime for Docker, containerd, Podman, and CRI-O. The vulnerability was discovered by the security researchers […]

runc dockers

Security experts found a serious flaw tracked CVE-2019-5736 affecting runc, the default container runtime for Docker, containerd, Podman, and CRI-O.

Aleksa Sarai, a senior software engineer at SUSE Linux GmbH, has disclosed a serious vulnerability tracked CVE-2019-5736 affecting runc, the default container runtime for Docker, containerd, Podman, and CRI-O.

The vulnerability was discovered by the security researchers Adam Iwaniuk and Borys Popławski.

Such kind of vulnerabilities could have a significant impact on an IT environment, its exploitation could potentially escape containment, impacting the entire container host, ultimately compromising the hundreds-to-thousands of other containers running on it

“The disclosure of a security flaw (CVE-2019-5736) in runc and docker illustrates a bad scenario for many IT administrators, managers, and CxOs.” reads a blog post. published by Red Hat.

“While there are very few incidents that could qualify as a doomsday scenario for enterprise IT, a cascading set of exploits affecting a wide range of interconnected production systems qualifies…and that’s exactly what this vulnerability represents,”

“The vulnerability allows a malicious container to (with minimal user interaction) overwrite the host runc binary and thus gain root-level code execution on the host.” Sarai wrote in a post to the OpenWall mailing list.

“The level of user interaction is being able to run any command (it doesn’t matter if the command is not attacker-controlled) as root within a container in either of these contexts:

  • Creating a new container using an attacker-controlled image.
  • Attaching (docker exec) into an existing container which the attacker had previous write access to.”

Sarai, which is one of the maintainers of runc, has pushed a git commit to address the vulnerability, but all the project built on runc need to include the changes.

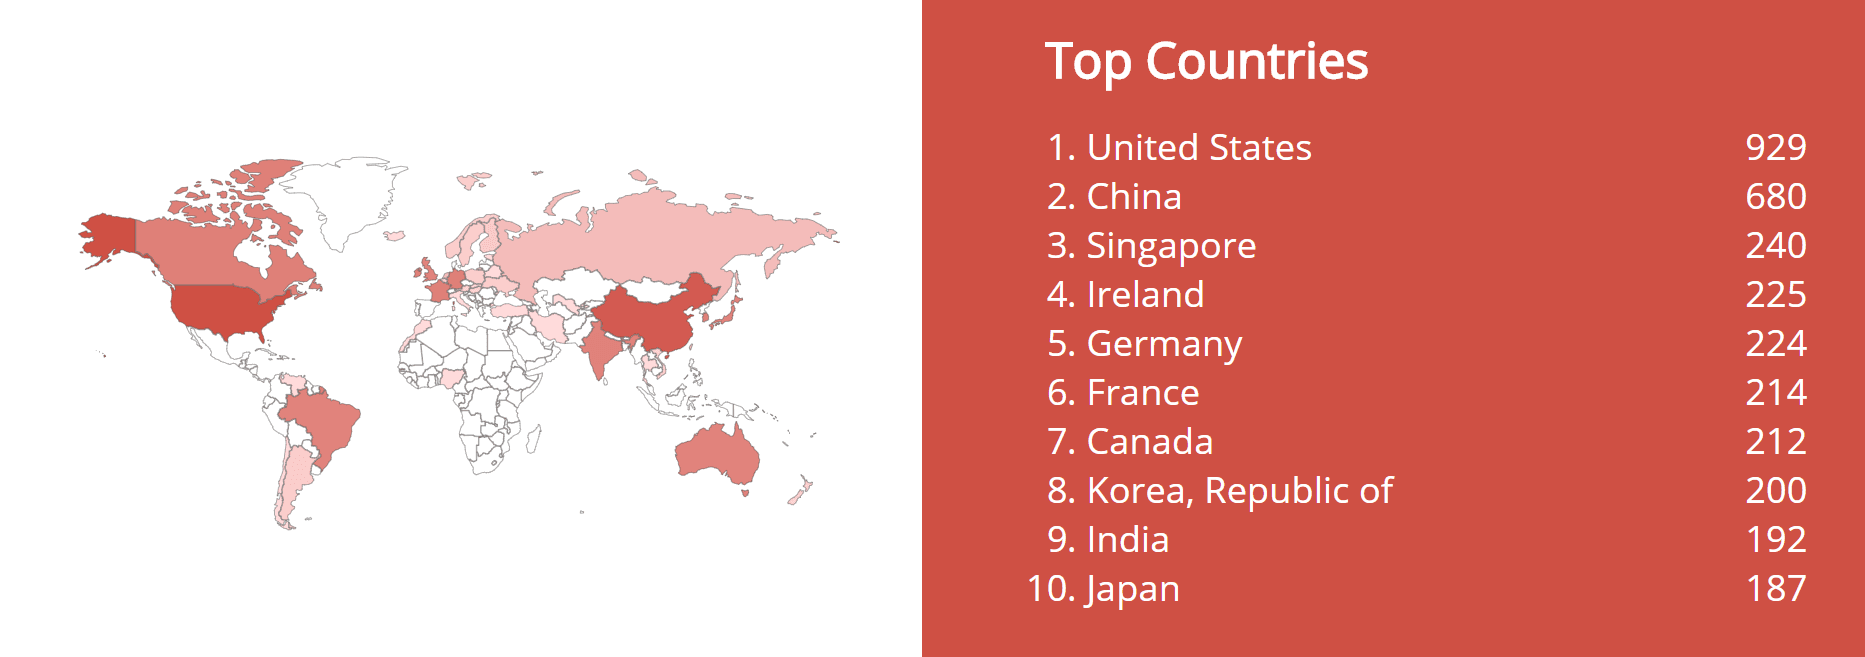
Docker released the v18.09.2 version to address the issue, but according to the experts, thousands of Docker daemons exposed online are still vulnerable, most of them in the US and China.

runc dockers

Default configurations of Red Hat Enterprise Linux and Red Hat OpenShift are protected, Linux distros Debian and Ubuntu are working to address the issue. Both Google Cloud and AWS published security advisories to recommend customers to update containers on affected services.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – runc, hacking)

[adrotate banner=”5″] [adrotate banner=”13″]

.


